Wireless bridge WB-3P-PTP6 |
|
Introduction
Annotation
Modern tendencies of telecommunication development necessitate operators to search for the most optimal technologies, allowing one to meet rapidly growing needs of subscribers, while maintaining at the same time consistency of business processes, development flexibility and reducing the costs of various services. Wireless technologies are spinning up more and more, and have paced a huge way for short time from unstable low-speed communication networks of low radius to broadband access networks equitable to speed of wired networks with high criteria to the quality of provided services.
WB-3P-PTP6 is a device designed for organizing long-distance radio bridges. A radio bridge is built using two such devices. WB-3P-PTP6 features a sealed housing designed for outdoor installation in various climatic conditions.
This user manual describes the purpose, main technical specifications, design, safe operation rules, installation and setup recommendations for the WB-3P-PTP6 wireless bridge.
Document conventions
Notes and warnings
Notes contain important information, tips, or recommendations for using and configuring the device. |
Warnings inform the user about situations that may harm the device or personnel, cause improper device operation, or data loss. |
Device description
Purpose
The WB-3P-PTP6 wireless bridge is a new-generation Wi-Fi 6 device designed to provide modern high-speed services.
With IEEE802.11ax support, the WB-3P-PTP6 wireless bridge provides data rates up to 2402 Mbps. The offset parabolic antenna makes WB-3P-PTP6 a universal solution for long-distance radio bridges.
The WB-3P-PTP6 wireless bridge (then "device") meets modern service quality requirements and allows traffic transmission in priority queues.
WB-3P-PTP6 can operate in a wide temperature range and high humidity conditions.
Device specification
Interfaces:
1 port of Ethernet 10/100/1000BASE-T (RJ-45) with PoE support;
Wi-Fi 6 GHz IEEE 802.11ax.
The power is supplied via 24 V PoE injector from 220 V.
Using a PoE injector with a voltage different from 24 V will damage the device. |
Functions:
WLAN capabilities:
Support for IEEE 802.11ax;
Data aggregation, including A-MPDU (Tx/Rx) and A-MSDU (Rx);
WMM-based packet priority and scheduling;
- Access point mode (AP-PTP/AP-PMP);
- Client mode (STA);
- Auto-distance detection;
- Automatic transmit power control;
Hidden SSID support;
MAC ACL support;
Third-party access point detection;
APSD support;
Channel list limiting;
- Spectrum analyzer;
Fixed center frequency support;
- TDD support;
Alignment.
Network features:
- automatic speed and duplex negotiation;
- VLAN support (Access, Trunk, General);
- C-VLAN configuration support;
- Management VLAN support;
- DHCP client;
- VLAN Mapping;
- Loopback Detection;
- MVR;
- NTP;
- Syslog;
- DHCP snooping;
- IGMP snooping (limit on the maximum number of groups);
- MAC Address Learning Limit;
- BPDU filtering;
- IPv6;
- LLDP;
- Ping Watchdog.
QoS functions:
Bandwidth limiting;
WMM parameter configuration for the radio interface;
Prioritization support by 802.1p, DSCP and VLAN ID;
- Traffic prioritization based on MAC/IP address.
Security:
Centralized authorization via RADIUS server (802.1X WPA3 Enterprise);
WPA3/OWE data encryption;
- RADIUS server authorization when logging into the device;
- User authentication protection system when logging into the device.
Figure 1 shows the WB-3P-PTP6 application diagram.
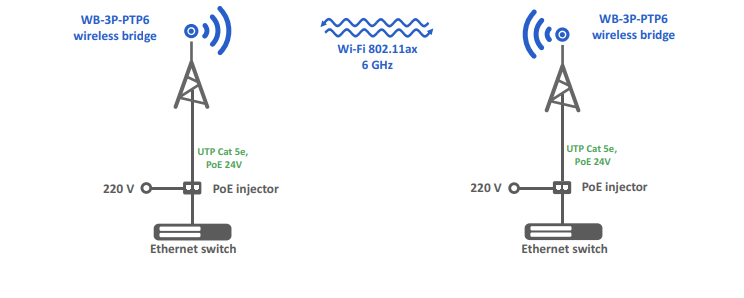
Figure 1 — WB-3P-PTP6 application diagram
Main technical specifications
The main technical specifications of the device are listed in Table 1.
Table 1 – Main specifications
| Ethernet interface parameters | |
| Number of ports | 1 |
| Electrical connector | RJ-45 |
| Data rate | 10/100/1000 Mbps, auto-negotiation |
| Standards | BASE-T |
| Wireless interface parameters | |
| Standards | 802.11ax |
| Frequency range | 5935–6425 MHz |
| Modulation | BPSK, QPSK, 16QAM, 64QAM, 256QAM, 1024QAM |
| Operating channels1 | 802.11ax: 1–93 (5935–6425 MHz) |
| Data rate2 | 802.11ax: 2402 Mbps |
| Maximum number of simultaneous connections | 6 GHz: 64 |
| Maximum output power of the transmitter1 | 6 GHz: 26 dBm |
| Receiver sensitivity | 6 GHz: up to -96 dBm |
| Security | WPA3/OWE |
| Antenna parameters | |
| Gain | 9 dBi |
| Polarization | linear, H/V |
| SWR | no more than 2 |
| Beam width (horizontal) | 65° |
| Beam width (vertical) | 65° |
| Management | |
| Remote management | web interface, CLI, Telnet, SSH, SNMP, NETCONF |
| Access restriction | by password, authentication via RADIUS server |
| General parameters | |
| Flash | 128 MB SPI-NAND Flash |
| RAM | 256 MB DDR3 RAM |
| Power supply | Passive PoE 24 V |
| Power consumption | no more than 10.5 W |
| Ingress protection | IP67 |
| Operating temperature range | from -45 to +65 °C |
| Relative humidity at 25 °C | up to 95 % |
| Dimensions (W × H × D) | 120 × 110 × 89 mm 120 × 110 × 144 mm (with cable gland) |
| Weight | 0.31 kg |
| Service life | no less than 15 years |
1 The number of channels and the value of the maximum output power will vary according to the rules of radio frequency regulation in your country.
2 The maximum wireless data rate is defined according to IEEE 802.11 standards. The real bandwidth can be different. Network operating conditions, environmental factors, including network traffic volume, building materials and structures, as well as network overhead data may reduce the actual bandwidth. The environment can influence the network coverage range.
Technical parameters of offset parabolic antenna
The main technical specifications of the offset parabolic antenna parameters are listed in Table 2.
Table 2 – Main specifications
| Parameters | Antenna 450 × 495 mm |
| Gain | 25.5 dBi |
| Offset angle | 24° |
| Polarization | linear, H/V |
| Radiation angle | 7° |
| Focal distance | 270 mm |
| Wind load | 130 km/h — operating 185 km/h — limit |
| Reflector dimensions | 450 × 495 mm |
| Dimensions (W × H × D) | 450 × 570 × 492 mm |
| Weight | 1.6 kg |
| Material | steel |
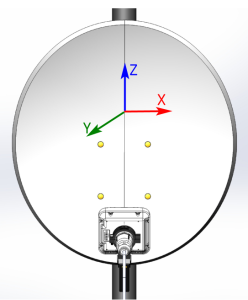
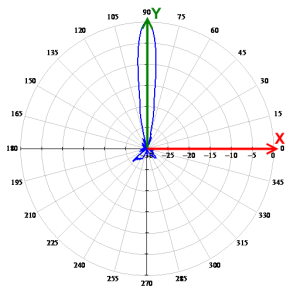
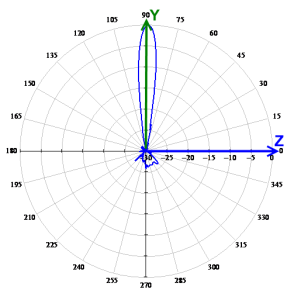
Radiation patterns
The radiation patterns of the device are shown in the figures below.
WB-3P-PTP6 radiation patterns | |
Measurement position
| |
AZIMUTH (XY)
| ELEVATION (YZ)
|
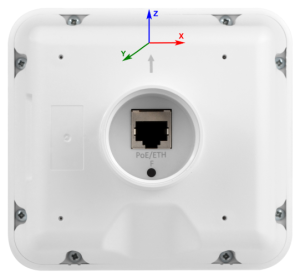
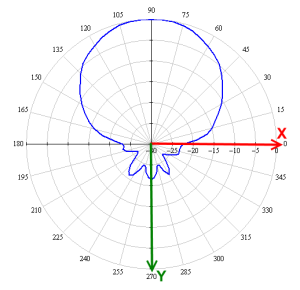
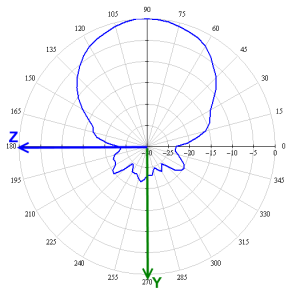
WB-3P-PTP6 radiation patterns | |
Measurement position
| |
AZIMUTH (XY)
| ELEVATION (YZ)
|
Design
The WB-3P-PTP6 device features a plastic housing in industrial design. The WB-3P-PTP6 main panel layout is shown in Figure 2.
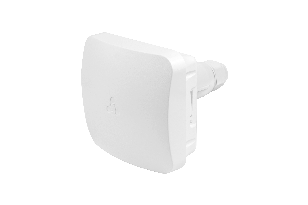
Figure 2 — WB-3P-PTP6 main panel layout
The WB-3P-PTP6 rear panel is shown in Figure 3.
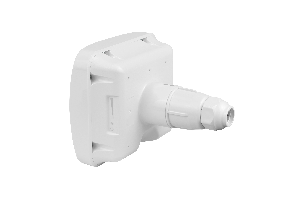
Figure 3 — WB-3P-PTP6 rear panel
On the WB-3P-PTP6 rear panel under the cable gland, there is a 10/100/1000BASE-T Ethernet port (RJ-45 connector) for connecting to the network and PoE power supply, as well as a factory reset button "F" (see Figure 4).
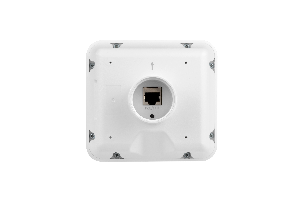
Figure 4 — RJ-45 сonnector and function button "F"
Light indication
The WB-3P-PTP6 indicator panel is shown in Figure 5.
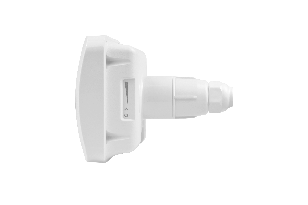
Figure 5 — WB-3P-PTP6 indicator panel
The device status is displayed by indicators on the side panel. The list of indicators and their status is provided in Table 3.
Table 3 — Light indication of device status
| Indicator / LED | Indicator status | Description | |
|---|---|---|---|
| WLAN — Received Signal Strength Indicators (RSSI) | solid | device is connected, signal level from the remote device is above -60 dBm |
| solid | device is connected, signal level from the remote device is above -70 dBm | |
| solid | device is connected, signal level from the remote device is above -80 dBm | |
| solid | device is connected, signal level from the remote device is above -100 dBm | |
| none of indicators is on | no connection between devices | ||
| LAN — Ethernet port indicator | solid | channel between WB-3P-PTP6 Ethernet-interface and connected device is active |
| flashing | process of packet data transfer between WB-3P-PTP6 Ethernet-interface and connected device | ||
| Power — power and device operation status indicator | solid | power connected, normal operation |
| flashing | device did not receive an address via DHCP | ||
| blinks frequently for 3 seconds, then solid | reboot/factory reset |

Restore the default configuration
There are two ways to reset the device to factory settings.
- Using the "F" button on the device. When the device is loaded, press and hold the "F" button (about 10–15 seconds) on the device rear panel, until all WLAN indicators start flashing.
- Using the PoE injector, that is included into the supply package. When the device is loaded, press and hold the "RST" button on the injector (for about 10–15 seconds) until all WLAN indicators start flashing.
The device will automatically reboot. Factory settings will start DHCP client. In case the address is not received via DHCP, the device will be available at IP address — 192.168.1.10, subnet mask — 255.255.255.0; username/password for web interface — admin/password. |
Supply package
The WB-3P-PTP6 basic supply package includes:
- WB-3P-PTP6 wireless bridge;
- Cable gland;
- Power injector Passive PoE 24 V;
- Power cable;
- Patch cord RJ-45, 5e cat., 1.5m;
- User manual on a CD (optional);
- Technical passport.
 Rules and recommendations for device installation
This section describes safety instructions, installation recommendations, set-up procedure and device power-on sequence.
Safety rules
- Do not open the device housing. There are no user-serviceable parts inside.
- Do not install this device during a thunderstorm. There is a risk of lightning strike.
- Voltage, current and frequency requirements specified in this manual must be observed.
- Before connecting measuring instruments and a computer to the device, they must be grounded first. The potential difference between equipment housings and measuring instruments must not exceed 1 V.
- Before power-on, ensure that the cables are intact and securely attached to the connectors.
- Do not install the device near heat sources or in rooms with temperatures below -45 °or higher 65 °C.
- When installing on elevated structures, established norms for working at height must be observed.
- The device must be operated by engineering personnel with special training.
- Only suitable auxiliary equipment should be connected to the device.
Installation recommendations
- The device can be installed to the pole/post, wall, or in an offset parabolic antenna holder. The installation height should be no less than 1 meters from the supporting surface, installation distance — no more than 5 meters from the edge of the surface. If it is not possible to comply with the last condition — increase the suspension height.
- Before installation and power-on, the device must be checked for visible mechanical damage. If damage is found, stop installation, draw up an inspection report, and contact the supplier.
- Evaluate signal level at the receiving point using free space propagation formulas.
- To ensure the best signal level, place the device on a post/pole so that its antenna is pointed as much as possible at the antenna of the remote device. In this case, direct visibility should be ensured between devices, and the Fresnel zone should be clear of obstacles. The highest signal level can be obtained by adjusting the antenna using RSSI indicators, web interface (more details in the Antenna Align submenu) or CLI command.
- After alignment, ensure that the signal from the remote device is as close as possible to the calculated value as possible and not below the allowable level -65 ÷ -70 dBm.
- If the signal exceeds -40 dBm, the remote device transmit power must be reduced.
- When installing offset parabolic antennas, consider the antenna offset angle: so that the maximum radiation direction is parallel to the ground, the tilt angle of the parabolic antenna must equal to the offset angle.
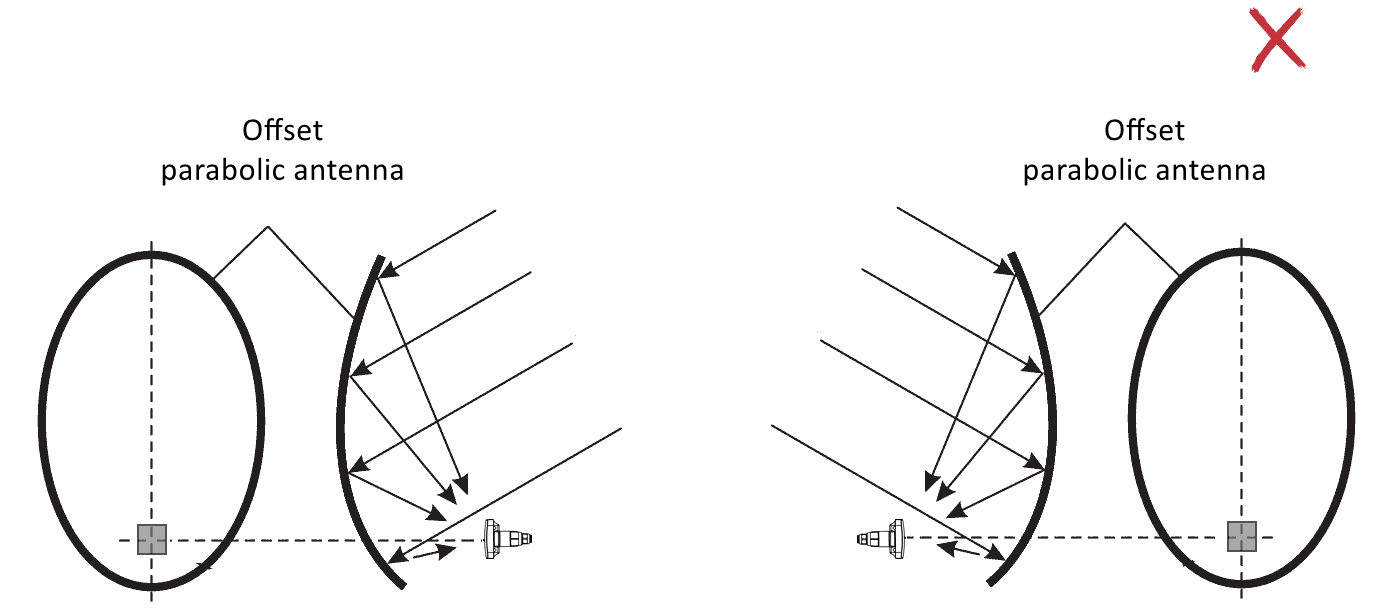
Figure 6 — Incorrect installation of offset parabolic antennas
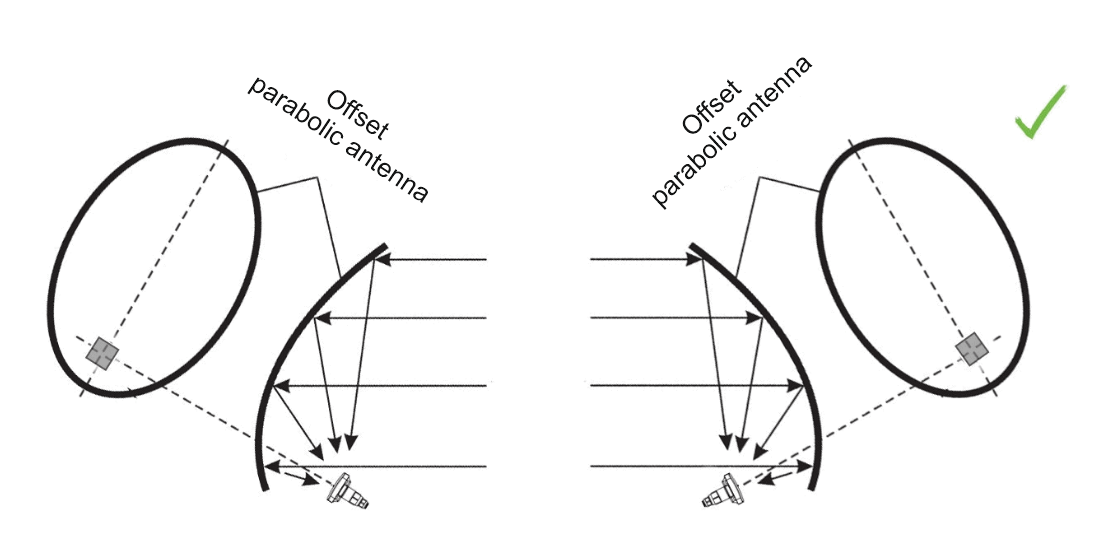
Figure 7 — Correct installation of offset parabolic antennas at the same suspension height
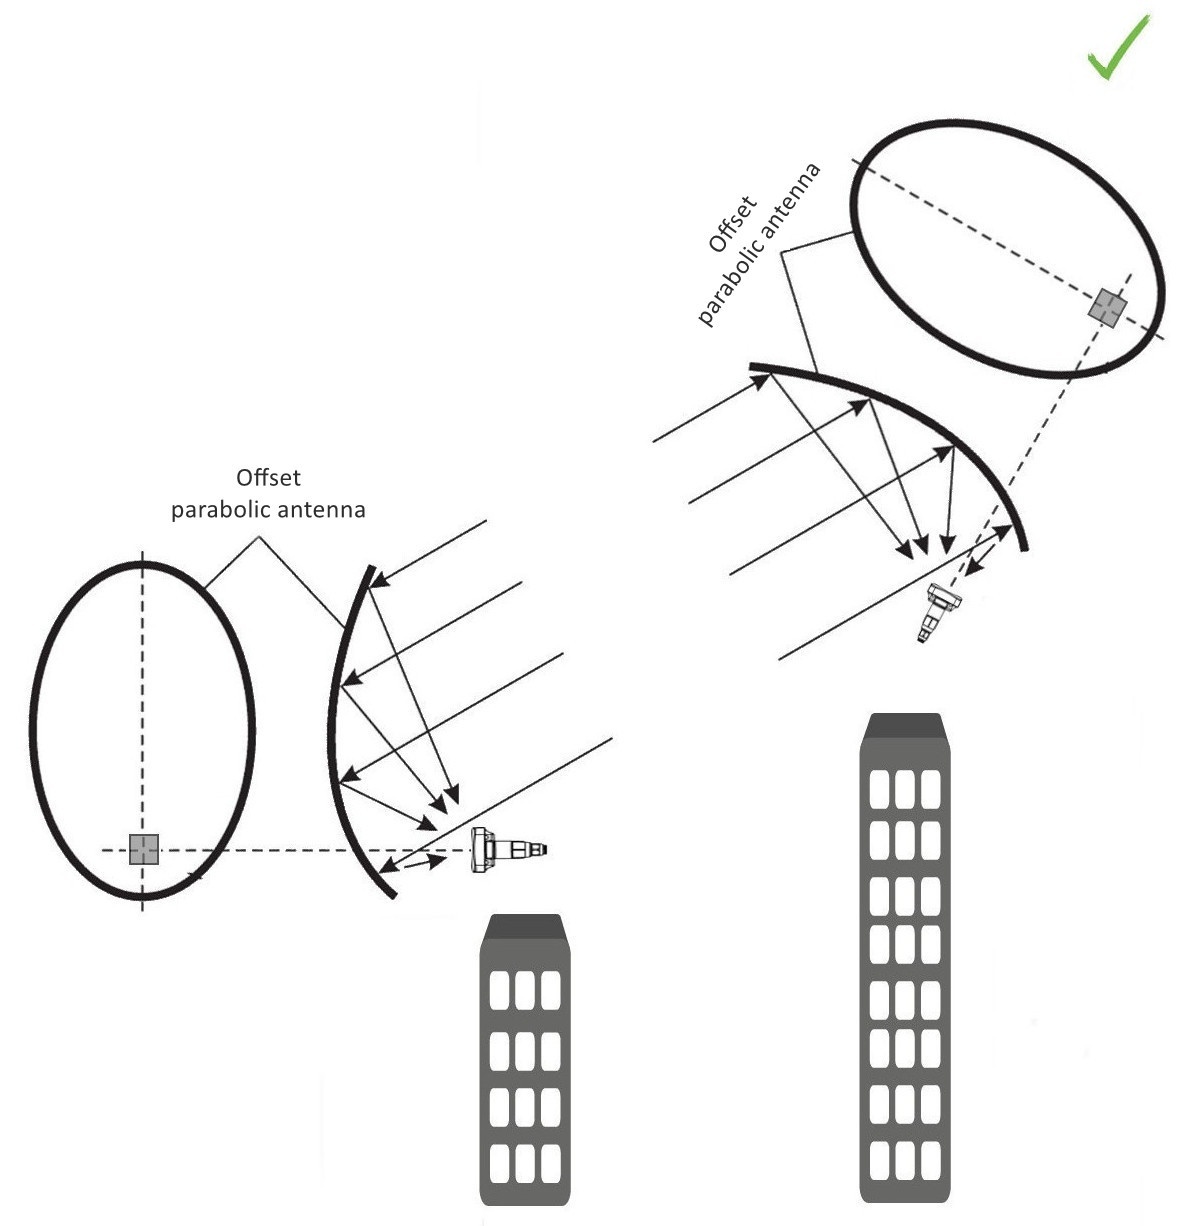
Figure 8 — Correct installation of offset parabolic antennas at different suspension heights
Recommendations for lightning protection
- Grounding must be done using an insulated multi-core wire. The grounding device and grounding wire cross-section must comply with the Electrical Installation Code.
- The first outdoor lightning protection must be installed as close as possible to the device, connecting with a short outdoor cable FTP-cable with shielded connectors.
- The second outdoor lightning protection must be installed as close as possible to the PoE injector, connecting them with a short outdoor FTP-cable with shielded connectors.
- The lightning protections are connected to each other with an outdoor FTP cable up to 100 m long.
- The PoE injector should be connected to a 220V grounded electrical outlet.
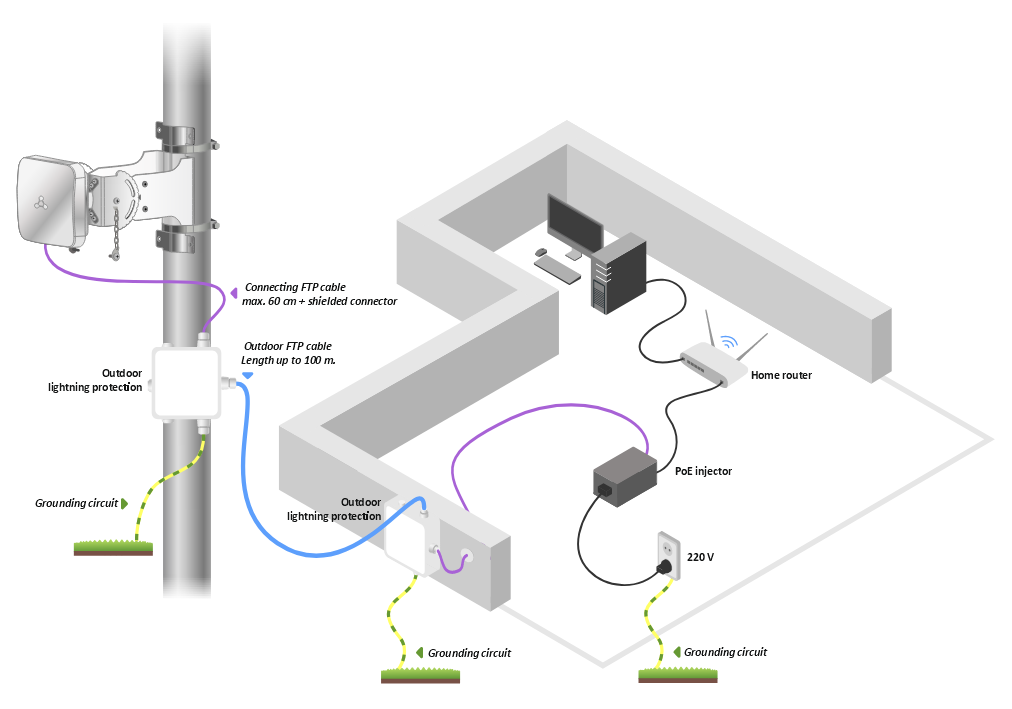
Figure 9 — Device wiring diagram for lightning protection
 Device preparation
1. Remove the device from the package.
2. Connect the Ethernet cable to the PoE/ETH port.
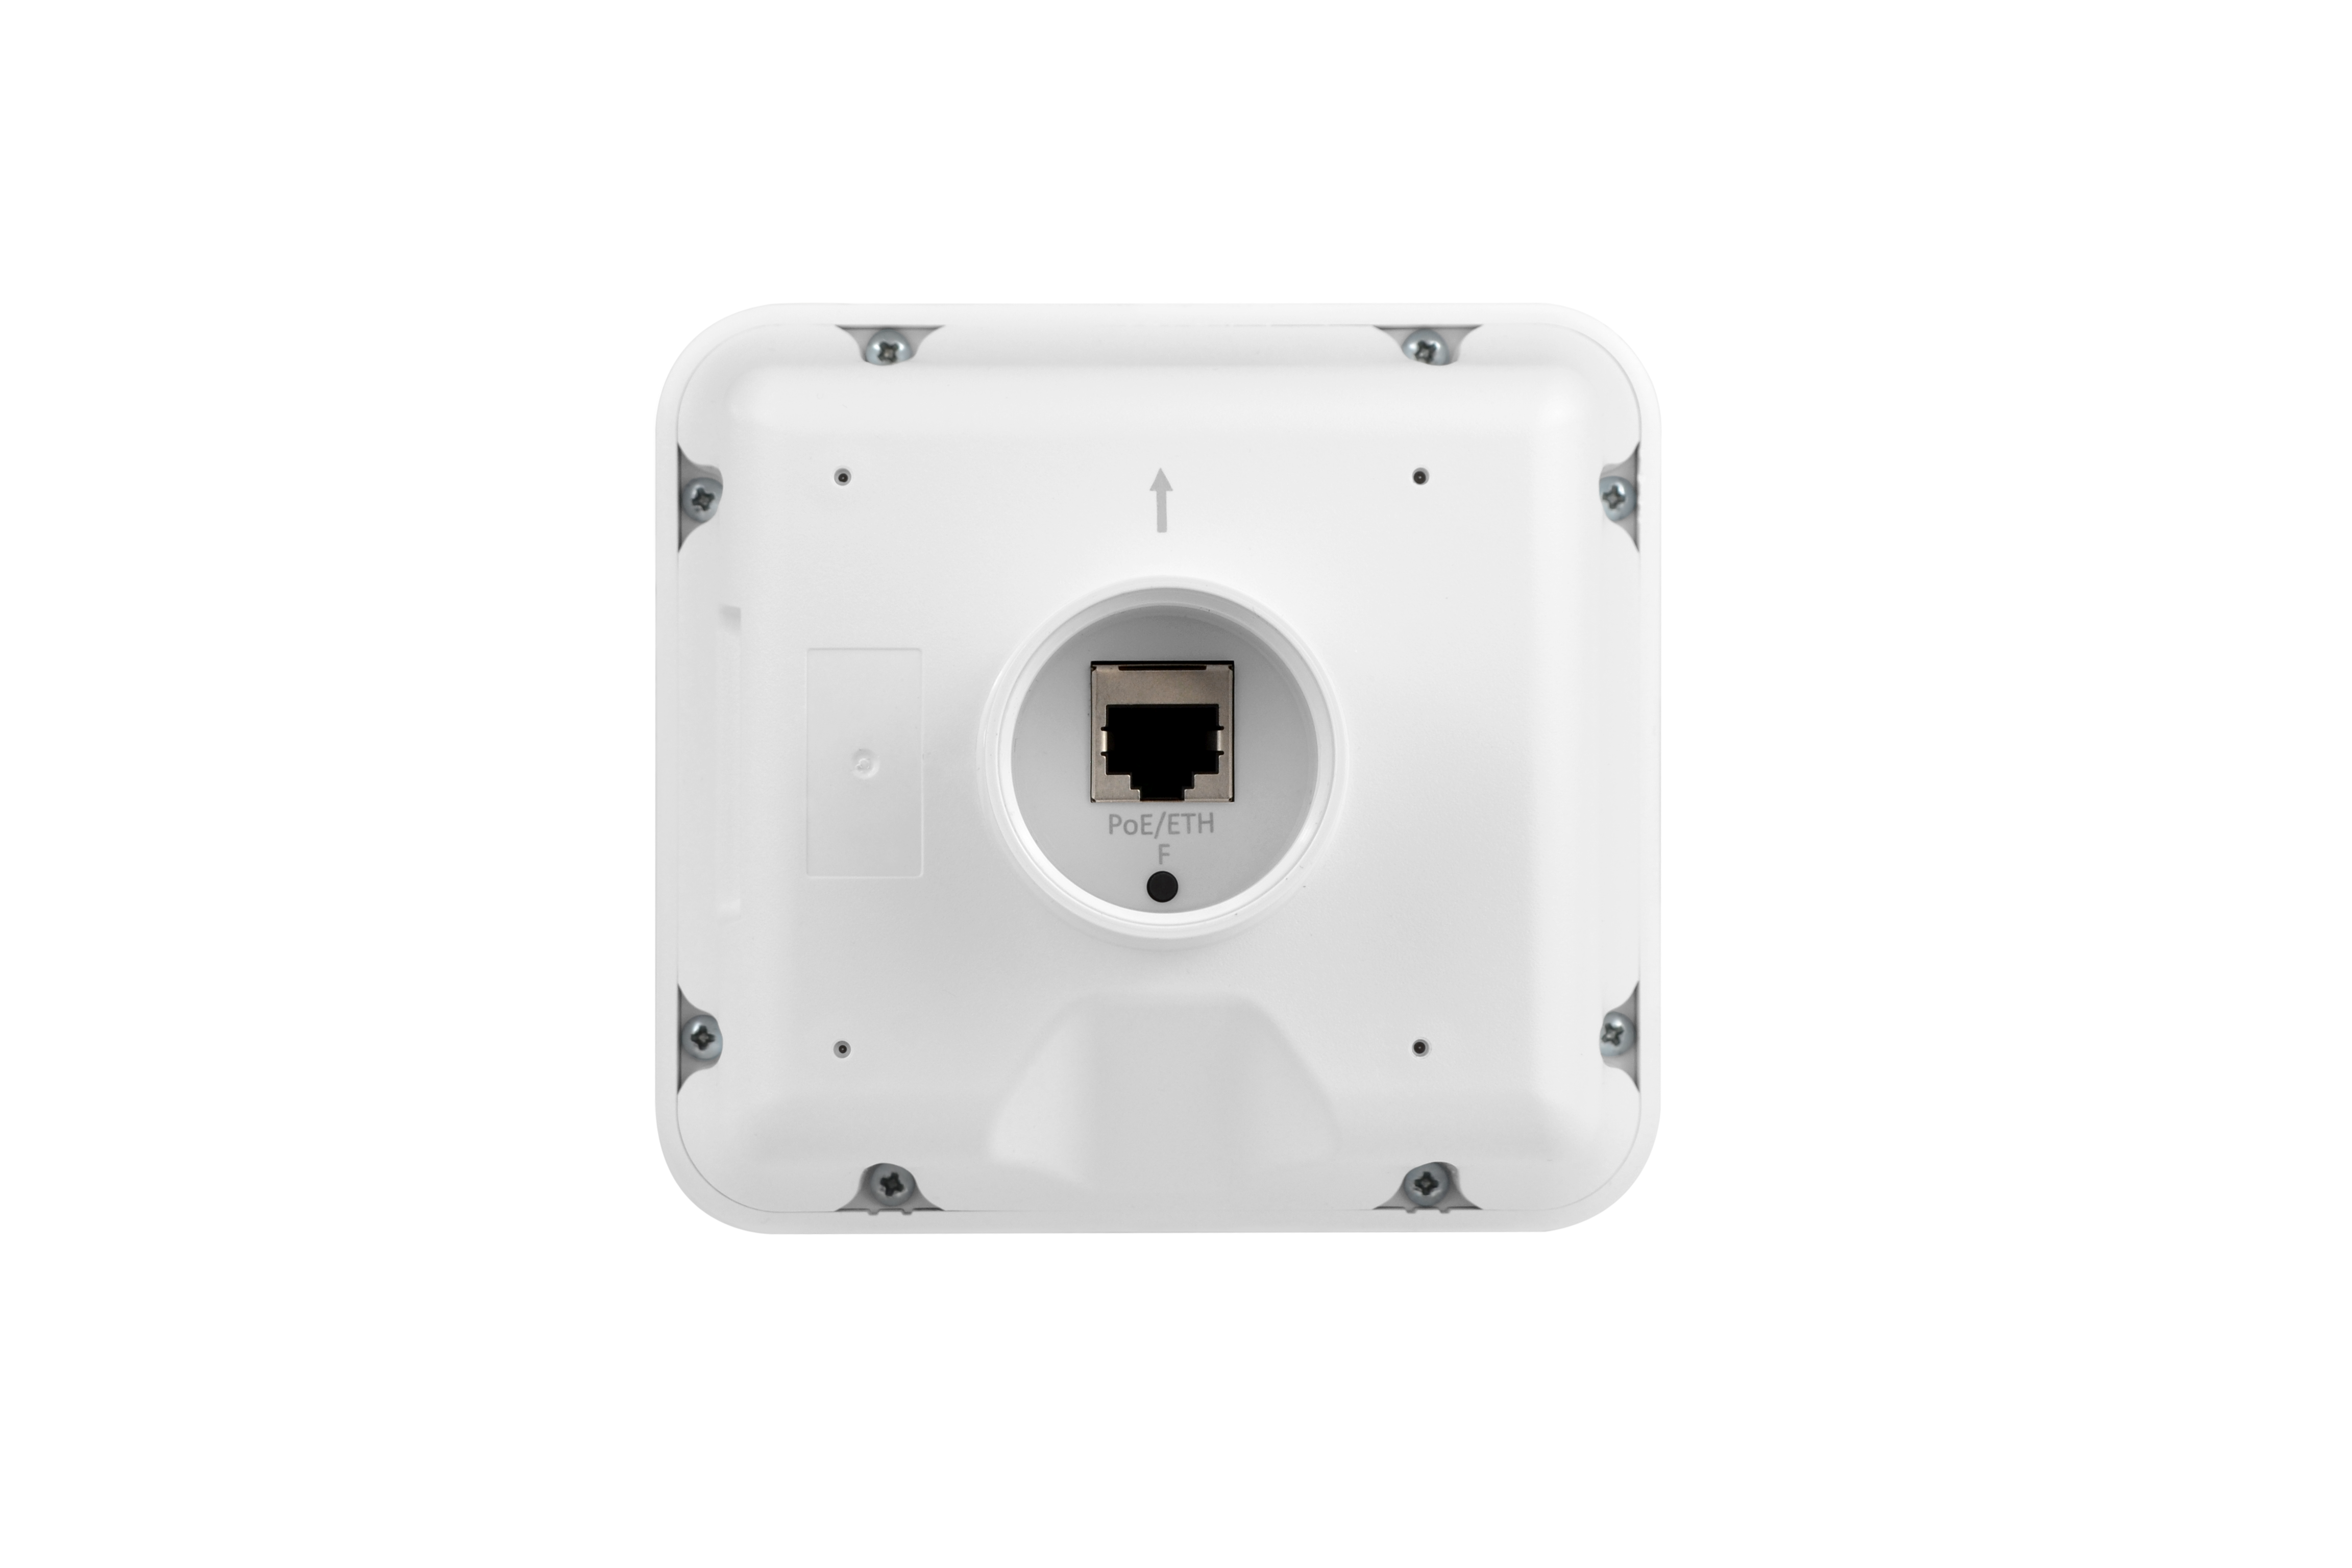
Figure 10 — RJ-45 connector and "F" button
 Device connection
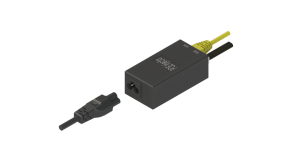
1. Connect the Ethernet cable from WB-3P-PTP5 to the PoE port of the injector.
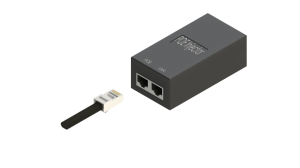
2. Connect the Ethernet cable of your network to the LAN port of the PoE injector.
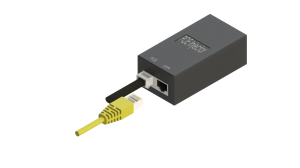
3. Connect the PoE injector to a 220V outlet using the power cord. After powering on, WB-3P-PTP5 will boot up within a minute.
4. Connect to the WB-3P-PTP5 web configurator using a browser, following the instructions in the section Device management via web interface.
5. If this is the first device startup, proceed to the section Preliminary setup.
 Preliminary setup
Perform preliminary device configuration before installation.
- Ensure that the power is connected.
- Follow the procedure from the section Example of device setup.
Ensure that a wireless connection is established between the devices: signal level indicators should be lit. The possible indicator states are described in the section Light indication.
Device installation 
The WB-3P-PTP6 wireless bridge has three mounting options: on a pole/post, on a wall and as a part of an offset parabolic antenna.
Device installation on a pole/post/wall
- Connect the device to the network and perform preliminary setup following the instructions in the section Preliminary setup. Then disconnect the device from the network and begin installation.
- Remove the bracket, hardware kit, and clamps from the packaging.
- Secure the bracket to the pole using a Ø60–80 clamp from the package. Final tightening of the Ø60–80 clamp is performed in step Alignment of devices mounted on a pole/post/wall. Fix the screw with the chain onto the bracket, then put the clamp Ø32–50 onto the tightening slats of the bracket. Follow the safety instructions. See Safety rules and Installation recommendations.
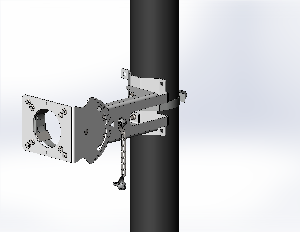
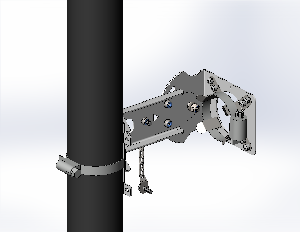
Figure 11 — Installing the bracket on pole
4. Disassemble the cable gland — unscrew the nut and remove the split gland from inside.
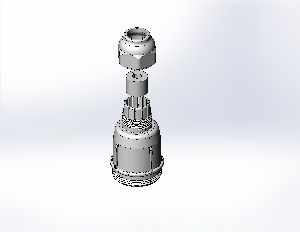
Figure 12 — Dismantling the cable gland
5. Pass the cable through the bracket and the cable gland as shown in Figure 13.
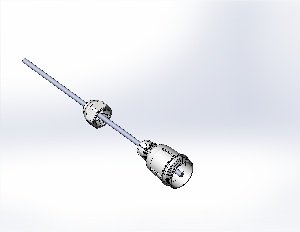
Figure 13 — Cable pulling through the cable gland
6. When installing the device with a deviation ±10 degrees, refer to Figure 14 (a). When installing the device with a deviation ±10–70 degrees, refer to Figure 14 (b).
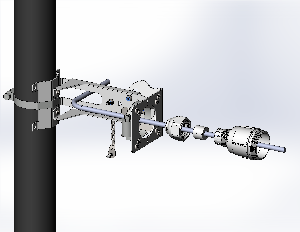
Figure 14 (a)
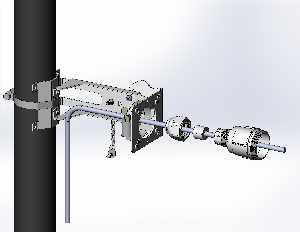
Figure 14 (b)
7. Crimp the RJ-45 connector on the cable and connect it into the mating part on the device housing.
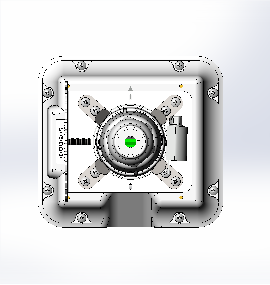
Figure 15 — RJ-45 connector on the device housing
8. Tighten the cable gland securely, place the split gland on the cable and insert it into the cable gland slats. Tighten the nut fully.
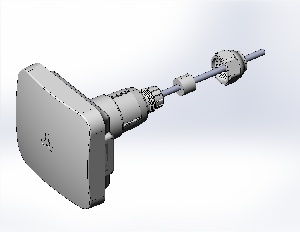
Figure 16 — Installing the cable gland
Incorrect cable gland installation may compromise device sealing. |
9. Insert the device into the bracket slats. Adjust the device by aligning the arrow on the housing with the hole in the bracket, then tighten the clamp Ø32–50.
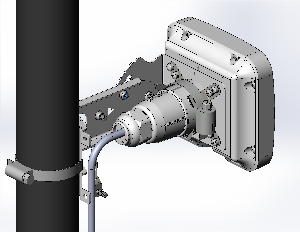
Figure 17 — Installing the device into the bracket
10. After installation, rotate the device to the required angle using the scale on the bracket as a reference. Tilt angle varies from -70 to 70 degrees.
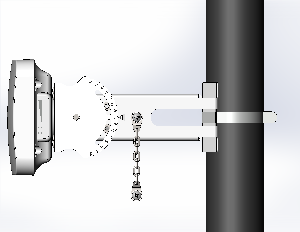
Figure 18 — Setting the required tilt angle
11. The bracket can also be installed on a wall. When installing on a wall, use screws or self-tapping screws 4×40 mm, if necessary — 6×40 mm dowels (Figure 19).
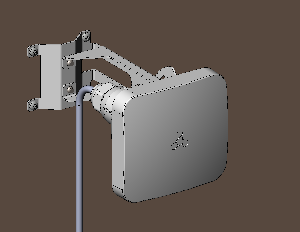
Figure 19 — Installing the device on a wall
12. Connect the device to the network following the procedures in the sections Device preparation and Device connection. Then proceed to device alignment.
Lightning protection is recommended to prevent device failure. |
Installation of the device as part of an offset parabolic antenna
Supply package:
- WB-3P-PTP6 basic supply package;
- Offset parabolic antenna with mounting kit.
To install the device in an offset parabolic antenna, perform the following steps:
1. Connect the device to the network and perform preliminary setup following the instructions in the section Preliminary setup. Then disconnect the device from the network and begin installation.
2. Assemble the device holder by inserting the upper part shaft into the lower part slots. On the right side of the holder, install an M4×20 screw with a nut.
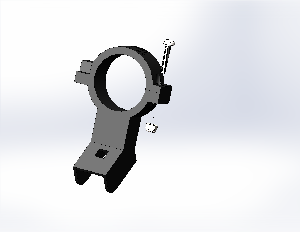
Figure 20 — Assembling the device holder
3. Attach the holder and the movable part of the bracket to the arc using M6×30 bolts, bracket and nuts from the mounting kit. Install a plug on the upper end of the arc.
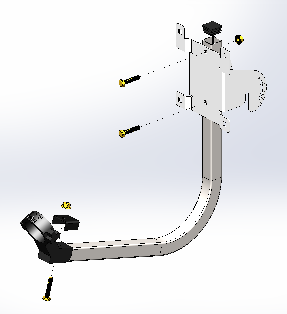
Figure 21 — Attaching the holder and movable bracket part to the arc
4. Connect the movable bracket part and antenna reflector using M6×12 bolts and nuts.
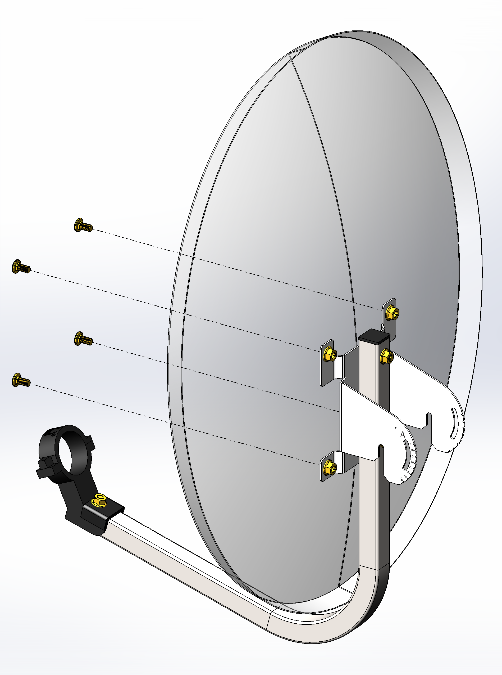
Figure 22 — Attaching the antenna reflector to the movable bracket part
5. Disassemble the cable gland — unscrew the nut and remove the split gland from inside.
Figure 23 — Dismantling cable gland
6. Pass the cable through the holder and the cable gland.
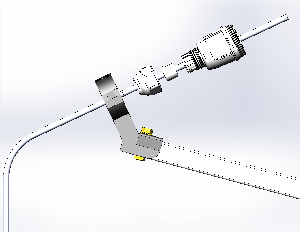
Figure 24 — Cable pulling through the holder and cable gland
7. Crimp the connector RJ-45 on the cable and connect it into the mating part on the device housing.
Figure 25 — Connector RJ-45 on the device housing
8. Tighten the cable gland securely, place the split gland on the cable and insert it into the cable gland slats. Tighten the nut fully.
Figure 26 — Installing the cable gland
Incorrect cable gland installation may compromise device sealing. |
9. Install the device in the holder and adjust the device to 0°, using the scale on the holder. Tighten the screw on the holder after adjustment.
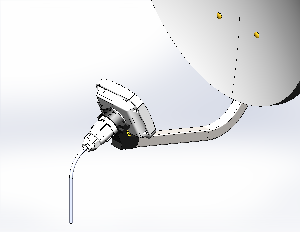
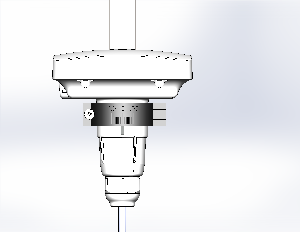
Figure 27 — Installing the device into the holder
10. Place the fixed part of the bracket on the pole as shown in Figure 28 and secure it with the clamps supplied with the device. The final tightening of the clamps is performed in Alignment of devices mounted on an offset parabolic antenna section. Install the chains; do not tighten the chain screws tightly, leaving a gap for installing the movable part of the bracket. Follow the instructions given in the sections Safety rules and Installation recommendations.
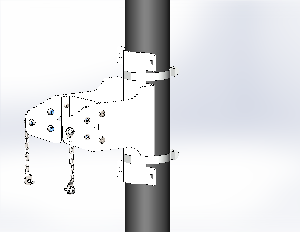
Figure 28 — Installing the fixed part of the bracket
11. Mount the reflector onto the fixed bracket. When installing, the previously under-tightened screws must engage the grooves of the movable bracket part.
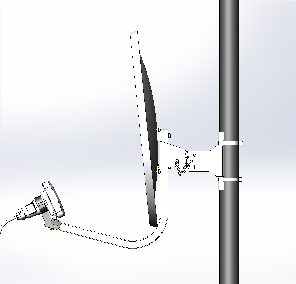
Figure 29 — Mounting the reflector onto the fixed bracket
12. If needed, the parabolic antenna can be mounted on a wall, for example using M6 bolts.
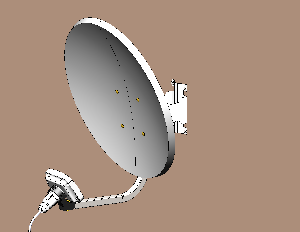
Figure 30 — Wall mounting of the parabolic antenna
13. Connect the device to the network following the procedures in the sections Device preparation and Device connection. Then proceed to device alignment.
 Device alignment
First, the horizontal alignment of the device is performed, then the vertical one. |
 Alignment of devices mounted on a pole/post/wall
1. Always perform alignment sequentially from both sides, using the calculated signal level obtained in the section Installation recommendations (it is necessary to obtain the closest possible value).
2. Adjust device positions by directing antennas approximately at each other, using maps and visual line of sight (for example, using binoculars) to the remote side.
With default settings, the client (STA) does not send a connection request, therefore, to establish a connection, first direct the access point (AP) to the client (STA). |
3. When establishing a connection between devices, align them sequentially, gradually increasing the values on the RSSI scale (indicator values are provided in section Light indication) in two planes — vertical and horizontal.
4. In the horizontal plane, one side covers a sector of 45–60 degrees — fixes the maximum, the second side performs a similar action.
5. Next, perform the second pass according to the above scheme. Finally tighten the clamp on the bracket. It is necessary to take into account that during alignment, hitting the side lobe of the radiation pattern may be interpreted as reaching the maximum signal level. To avoid this situation, it is necessary to perform a full pass in the sector and note any nonlinear level changes.
6. Repeat steps 4–5 in the vertical plane. Fix the resulting tilt angle using screws on the chain.
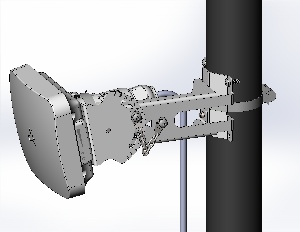
Figure 31 — Setting the required tilt angle
7. For more precise alignment, use the command in CLI or web interface (more details in the "Antenna Align" submenu), achieving maximum signal level values.
 Alignment of devices mounted on an offset parabolic antenna
1. Always perform alignment sequentially from both sides, using the calculated signal level obtained in the section Installation recommendations (it is necessary to obtain the closest possible value).
2. Adjust device positions by pointing antennas approximately at each other, using maps and visual line of sight (for example, using binoculars) to the remote side.
With default settings, the client (STA) does not send a connection request, therefore, to establish a connection, first direct the access point (AP) to the client (STA). |
3. When establishing a connection between devices, align them sequentially, gradually increasing the values on the scale RSSI (indicator values are provided in section Light indication) in two planes — vertical and horizontal.
4. In in the horizontal plane, one side covers a 30° sector 45–60 degrees — fixes the maximum, the second side — performs a similar action.
5. Then a second pass is performed following the scheme described above. Fully tighten the clamps on the fixed part of the bracket. Note that during alignment, entering a side lobe of the radiation pattern may be interpreted as reaching the maximum signal level. To avoid this, perform a full sweep across the sector and note nonlinear signal level changes.
6. Repeat the steps in the vertical plane 4–5: Rotate the device to the required angle using scales A and B on the bracket as references. Scale A — tilt angle of the parabolic antenna, scale B — elevation angle. Then secure the obtained tilt angle using the screw on the chain.
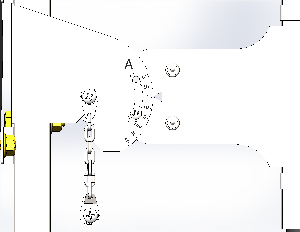
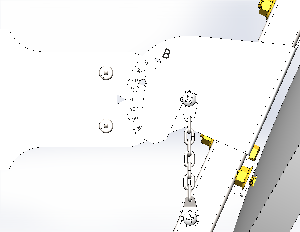
Figure 32 — "A" and "B" scales on the movable part of the bracket
7. When setting the angle on the "A" scale from -10 to 5 degrees, it is recommended to additionally fix the movable part of the bracket with a second screw from the kit.
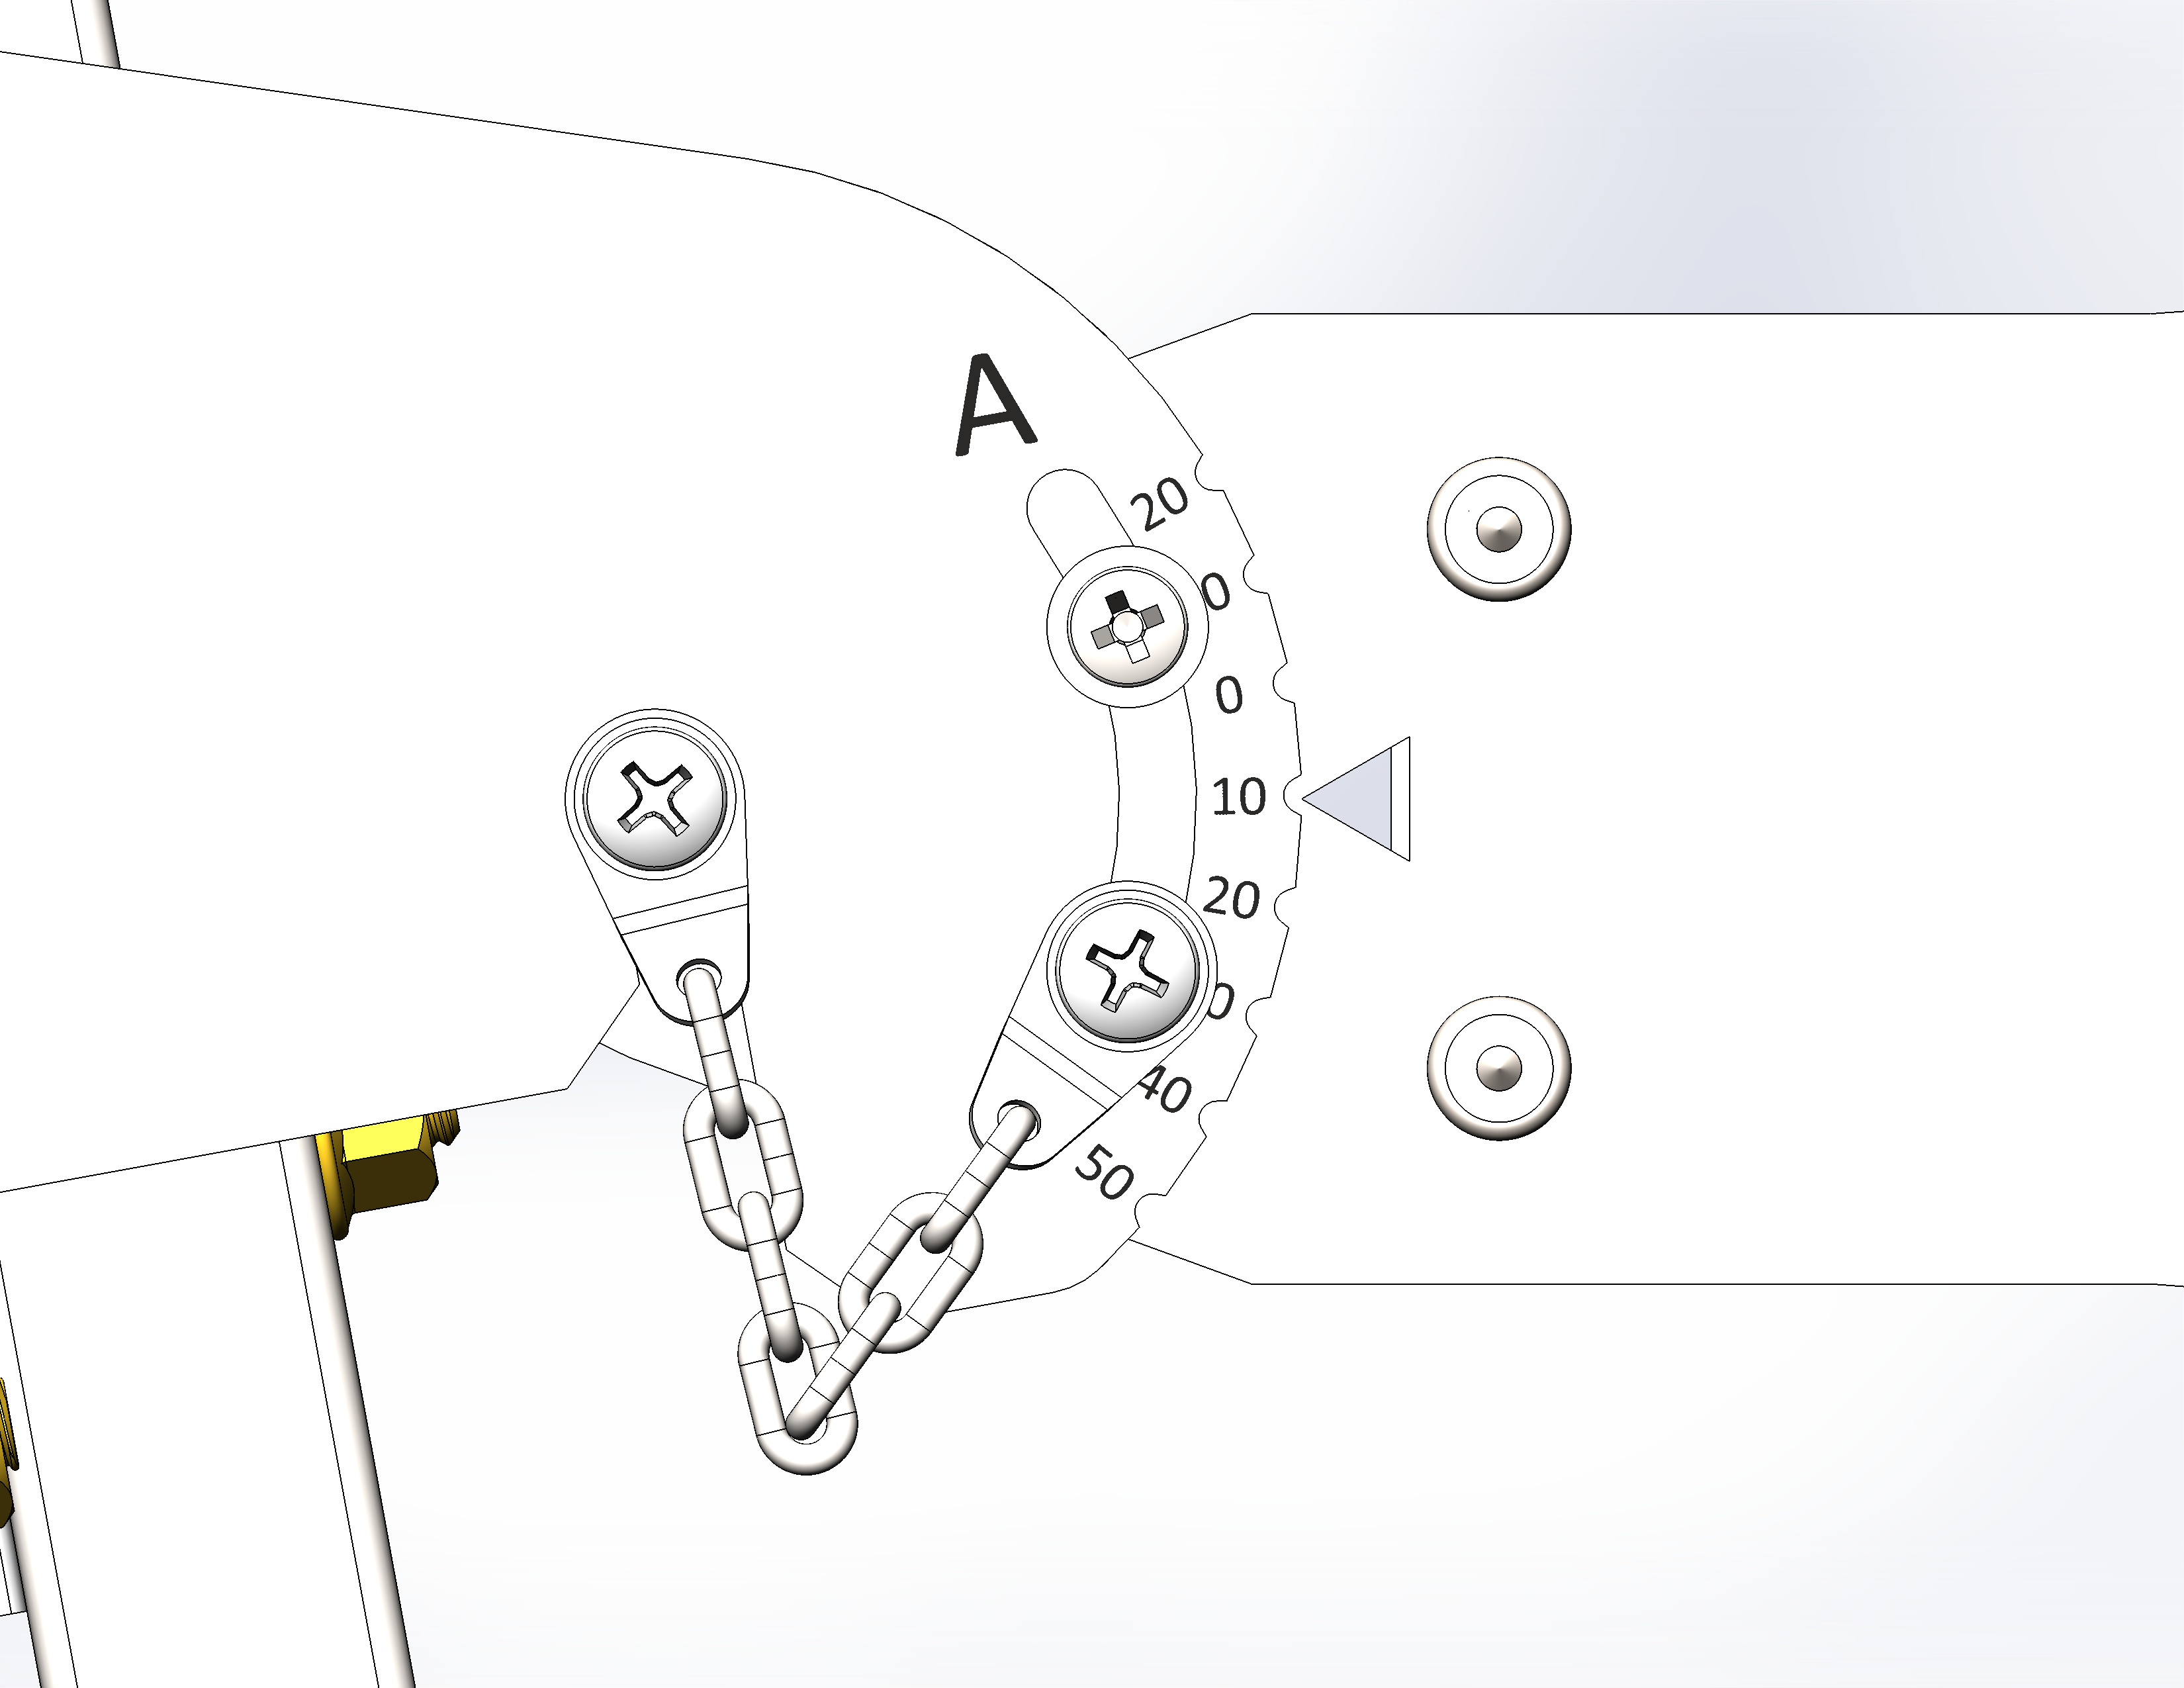
Figure 33 — Additional fixation of the bracket movable part
8. For more precise alignment, use the command in CLI or web interface (more details in the "Antenna Align" submenu), achieving maximum signal level values.
Final device setup
- It is recommended to select and set a static modulation on this and the remote devices. To select a static modulation, run a continuous ping to the devices. Then, in the "Monitoring" menu, under "Wireless Peer"/"Wireless Clients," note the automatically set modulation and set it statically in the channel transmission rate settings in the "Radio" menu. For reliability, you can set the modulation a couple of points lower than the automatic setting.
- Scan the environment with a spectrum analyzer and select the least congested channel.
- Set the final channel in the "Radio" menu.
 Device management via web interface
Getting started
To begin, connect to the device via the Ethernet interface using a web browser:
- Open web browser (a program for viewing hypertext documents), for example Firefox, Opera, Chrome.
Enter the device IP address in the browser address bar.
Factory IP address: 192.168.1.10, subnet mask: 255.255.255.0. By default, the device is capable to obtain an IP address via DHCP. |
After three unsuccessful attempts to enter the login and password, access to the account for this user will be blocked for 60 seconds. |
Upon successful device detection, the browser displays a username and password login page.
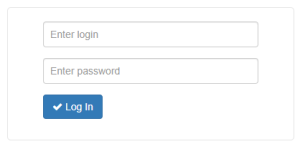
3. Enter the username in the field "Enter Login" and password in the line "Enter Password".
Factory settings: login: admin, password: password. |
After three unsuccessful attempts to enter the username and password, access to the account for this user will be blocked for 60 seconds. |
4. Click "Log In". The device status monitoring menu opens in the browser window.
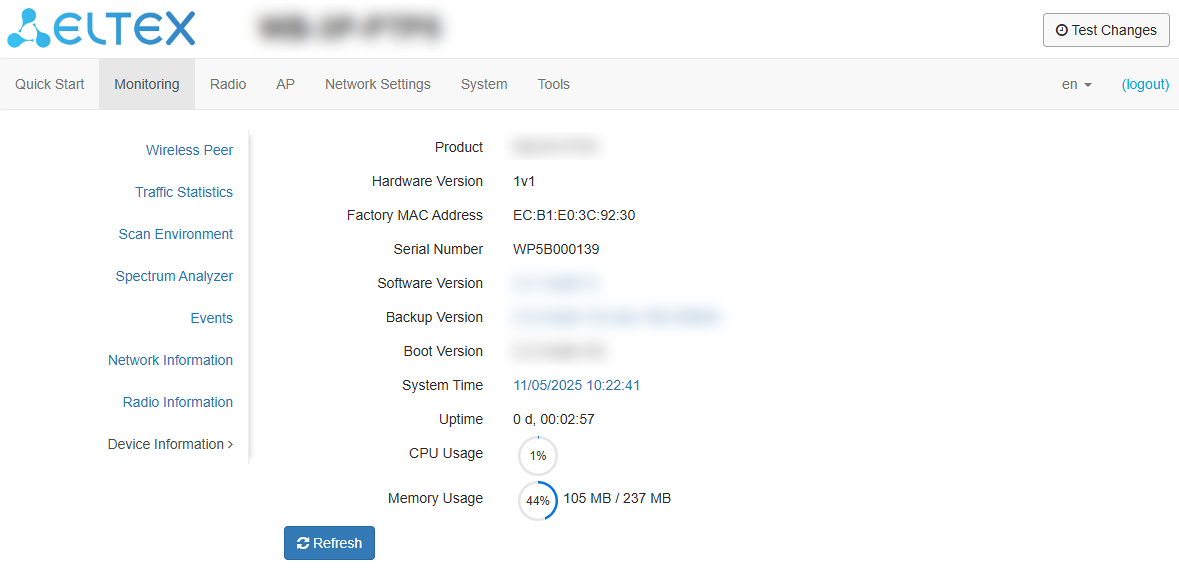
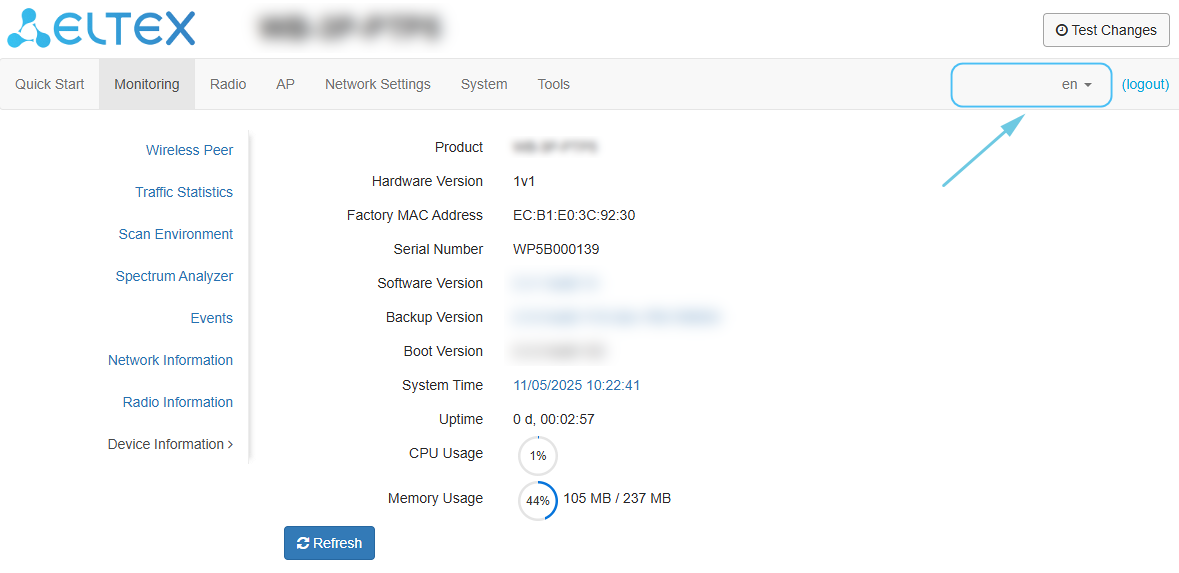
5. If necessary, select the information display language.
User change
The device has two types of users: admin and viewer:
- admin (password by default: password) has full access to the device: read and write any settings, full device status monitoring.
- viewer has read-only access to the entire device configuration with no editing capability; full device monitoring is available.
If to click the "Logout" button, the current user session will be terminated and the authorization window will be displayed:
To change access, specify the appropriate username and password, click the button "Log In".
Applying configuration and discarding changes
Applying configuration
When pressing the button
 the process of saving the configuration to flash-device memory and application of new settings. All settings take effect without a device reboot.
The web interface has a visual indication of the current status of the setting applying process (Table 4).
Table 4 — Visual indication of the current configuration application process status
Appearance | Status description |
|---|---|
| After clicking "Apply", the process of settings saving to device memory is launched. This is indicated by the icon |
| The successful save and application of settings is indicated by the icon |


2. Cancel changes
The changes can be discarded only before clicking the "Apply" button. If you click the "Apply" button, all the changed parameters will be applied and saved to device memory. After clicking the "Apply" button, return to the previous settings will not be possible. |
The button for discarding changes appears as follows:  .
Test mode
The device has a test mode for testing configurations.
To activate it, click the "Test Mode" button in the top panel of the web interface.

The test mode runs for 300 seconds (5 minutes). During this time, you can navigate the web configurator tabs and make any changes, applying them on each page using the "Apply" button.
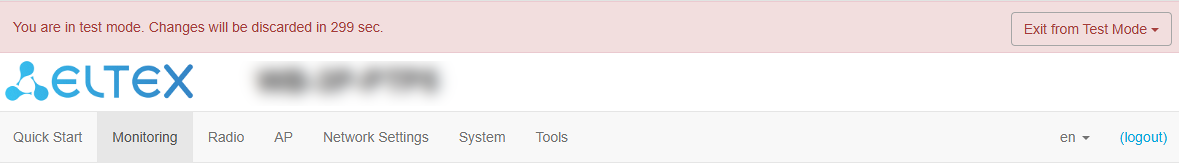
After checking the required configuration, click the "Exit from Test Mode" button and select the desired action:
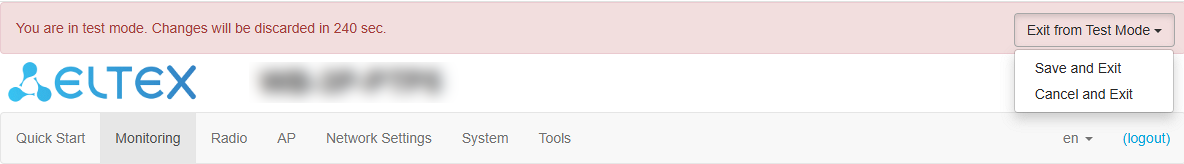
- "Save and Exit" — when pressed, the device will exit test mode and save all configuration changes made and applied in this mode to non-volatile memory. It will be impossible to cancel the changes made in test mode.
- "Cancel and Exit" — when pressed, the device will exit test mode and discard all changes made in this mode. The configuration that was active on the device before enabling test mode will be restored.
If the administrator does not exit test mode within 300 seconds, this will happen automatically, and all changes made in that mode will be undone. After the specified time expires, the configuration will be restored, even if the access to the device was lost as a result of these actions.
Web interface basic elements
Navigation elements of the web interface are shown in the figure below.
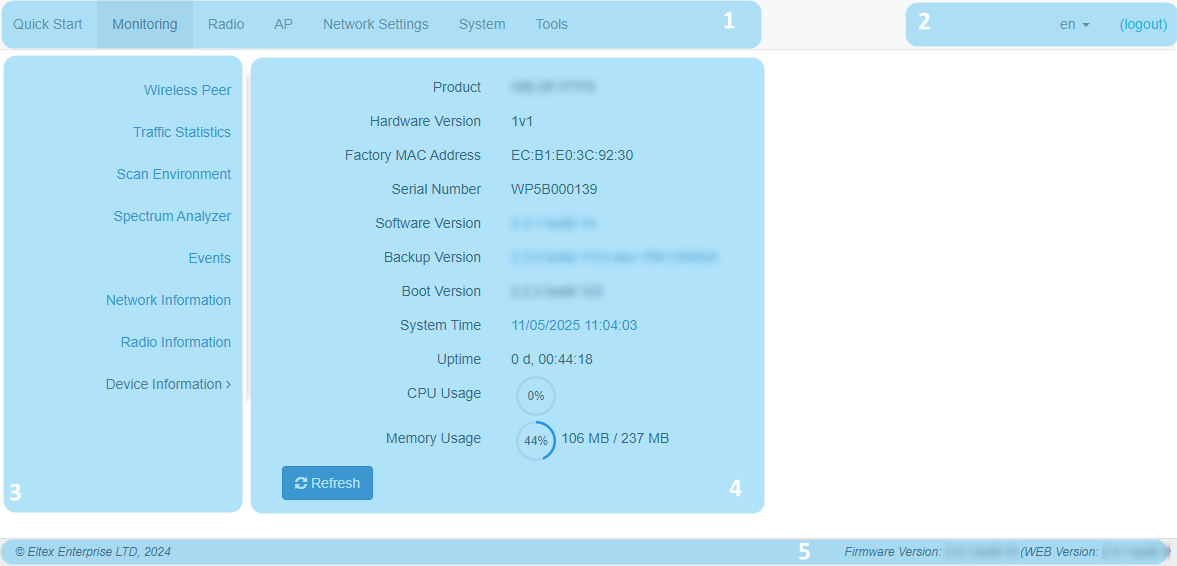
The user interface window is divided into five areas:
- Menu tabs for grouping submenus by categories: Quick Start, Monitoring, Radio, AP ("AP" menu available only in device mode "Access Point PTP" or "Access Point PMP") or STA ("STA" menu available only in device mode "Station / Client"), Network Settings, System, Tools.
- Interface language selection and Logout button designed to end a session in the web interface under a given user.
- Submenu tabs allow one to control settings field.
- Device configuration field displays data and configuration.
- Information field displays current firmware version.
"Quick Start" menu
In the "Quick Start" menu, the basic configuration of the device is performed.
"Quick Start" submenu
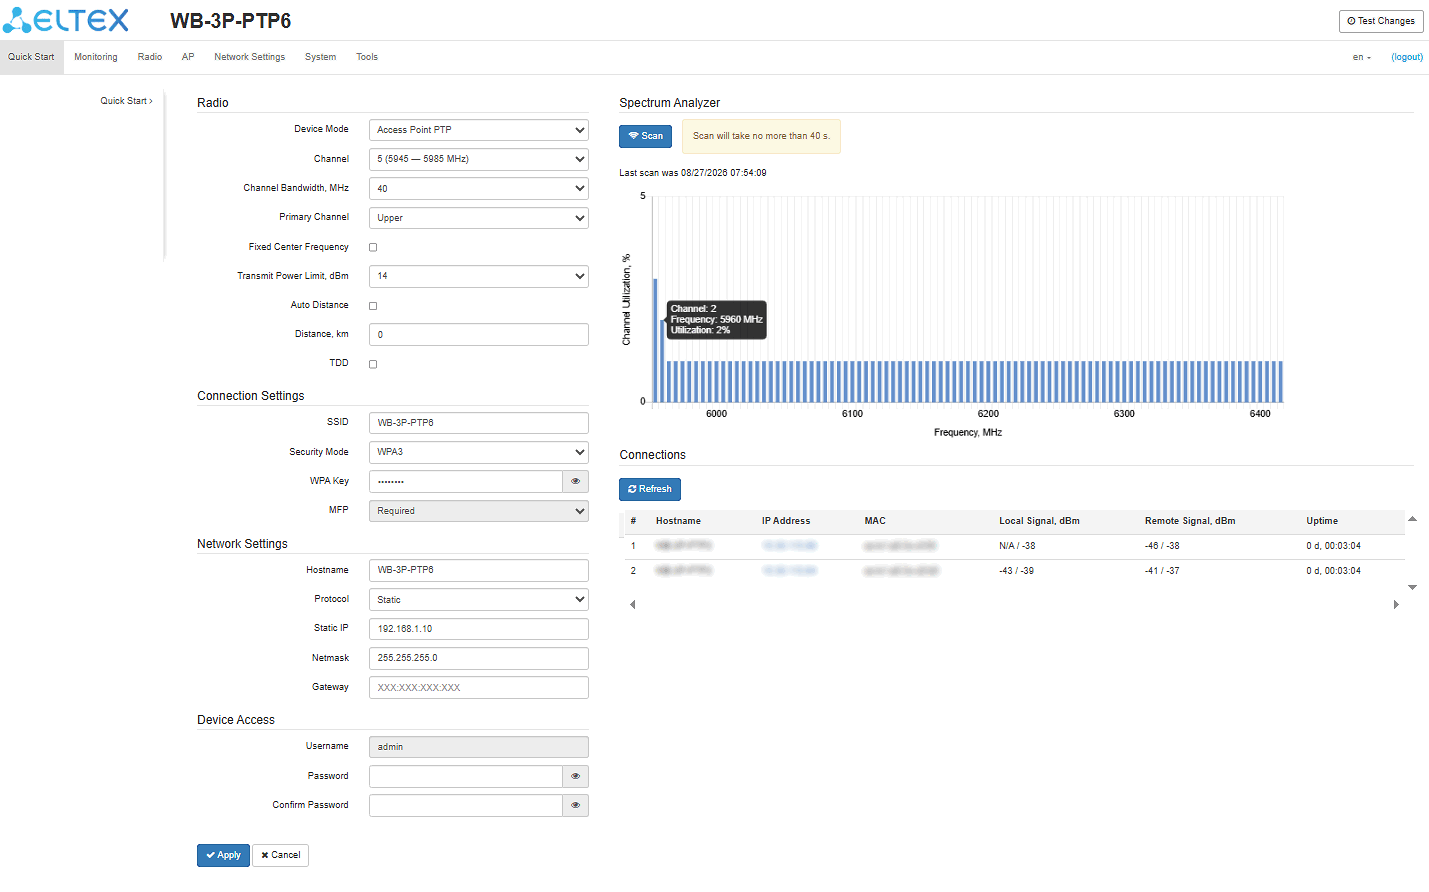
Radio
The "Radio" section configures the main device radio interface parameters.
- Device Mode — device radio interface operating mode. The following modes are available:
- Access Point PTP — Point-to-Point;
- Access Point PMP — Point-to-Multipoint;
- Station — wireless client (STA).
- Channel — data channel selection. If the "Auto Channel" is checked in the Radio menu, this setting will be locked;
- Channel Bandwidth, MHz — сhannel bandwidth on which the device operates; accepts values 20, 40, 80 and 160 MHz;
- Primary Channel — this parameter can only be changed when the statically set channel bandwidth equals to 40 MHz. The 40 MHz channel can be considered as consisting of two adjacent 20 MHz channels. These two 20 MHz channels are called primary and secondary channels:
- Upper — primary channel will be the upper 20 MHz channel in the 40 MHz band;
- Lower — primary channel will be the lower 20 MHz channel in the 40 MHz band.
- Fixed Center Frequency — when сhecked, all traffic (data and control packets) will be transmitted on the specified channel center frequency with the specified bandwidth (40/80/160 MHz). The function is proprietary, the transmission is not carried out according to IEEE 802.11 standards, which assume the use of different center frequencies for data and control traffic with a channel bandwidth of 40/80/160 MHz;
- Transmit Power Limit, dBm — Wi-Fi transmitter signal power adjustment in dBm;
- Auto Distance — when this option is enabled, the device will automatically detect and configure the distance between devices;
- Distance, km — distance between devices in kilometers. Changing the distance value will change the ACK timeout value. The distance should be rounded up. For example, if the distance between devices is 3.2 km, then 4 km should be specified;
- TDD — when сhecked, the option is enabled; otherwise, it is disabled. TDD is a collision-free time-division multiplexing (TDD) technology that synchronizes data transmission in both directions within a time frame.
The "Channel", "Channel Bandwidth", "Primary Channel" parameters are only available when the device mode is "Access Point PTP" or "Access Point PMP". |
Connection Settings:
- SSID — virtual wireless network name;
- Security Mode — wireless network access security mode:
- OWE (Opportunistic Wireless Encryption) — encryption method that provides the security of data transmitted over an unsecured network. In this case, users do not need to do any additional actions and enter a password to connect to the network;
- WPA3 — encryption methods, the selection of which makes the following settings available:
- WPA key — key/password required to connect to the wireless network. The key length is from 8 to 63 characters.
- MFP — management frame protection (available for WPA3, OWE security modes). When selecting the WPA3 and OWE security mode, MFP is set to Required:
- Required — management frame protection is enabled. The device cannot connect to a wireless network that does not support MFP.
Network Settings:
- Hostname — network name of the device, a string of 1–63 characters is specified: Latin uppercase and lowercase letters, digits, the hyphen sign "-" (the hyphen cannot be the last character in the name);
- Protocol — protocol used to connect the device via Ethernet interface to service provider network:
- DHCP — operating mode in which IP address, subnet mask, DNS server address, default gateway and other parameters required for operation in the network are obtained from DHCP server automatically;
- Static — operating mode in which IP address and all the necessary parameters for WAN interface are assigned statically. If "Static" is selected, the following parameters will be available to set:
- Static IP — device WAN interface IP address in the provider network;
- Netmask — external subnet mask;
- Gateway — address to which the packet is sent if the route in routing table is not found for it.
- Gateway — address to which the packet is sent if the route in routing table is not found for it.
Device Access:
The "Device Access" section is used to change the password.
When Logging In via web interface, administrator (password by default: password) has full access to the device: read and write access to any settings, full device status monitoring. To change the password, enter a new password first in the field "Password", then in the field "Confirm Password" and click the button "Apply" to save the new password.
Spectrum Analyzer:
The "Spectrum Analyzer" section is used to launch and monitor the spectrum analyzer.
The WB-3P-PTP6 devices can launch the spectrum analyzer on the Radio 6 GHz.
When the spectrum analyzer is launched, the radio interface will be switched to scanning mode, which will interrupt all Wi-Fi connections on this radio interface. |
To start the spectrum analyzer, click the "Scan" button. The information window located to the right of the button displays the time in seconds that has passed since the start of the scan. The scan on the Radio 6 GHz will take no more than 1 minutes.
- Last scan was... — date and time of the last scan;
- Channel Utilization — information about the radio channel congestion, expressed as a percentage;
- Frequency — channel frequency, on which scanning was performed, MHz;
- Channel — channel number corresponding to a given frequency.
The spectrum analyzer analyzes all channels in the range, regardless of the settings on the radio interface. |
Connections:
The "Connections" section displays information about the status of connected devices.
- # — number of the connected device in the list;
- Hostname — network device name;
- IP Address — IP address of the connected device;
- MAC — MAC address of the connected device;
- Local Signal, dBm — received signal level, dBm;
- Remote Signal, dBm — received signal level of the remote device, dBm;
- Uptime — connection time.
To apply a new configuration and save settings to non-volatile memory, click the "Apply" button. Click the "Cancel" button to discard the changes.
"Monitoring" menu
In the "Monitoring" menu the current system state is displayed.
"Wireless Peer/Wireless Clients" submenu
The "Wireless Peer"/"Wireless Clients" displays information about connected device status. Information about connected devices is not displayed in real time. To update the information on the page, click the "Refresh" button.
Depending on the mode devices, "Access Point PTP" or "Access Point PMP", the "Wireless Peer" or "Wireless Clients" submenu will be available respectively. |
For easy monitoring, it is possible to select the parameters to display. To do this, click |
 . When pressing "By default" button default parameters will be displayed.
 . The feature is available only in "Access Point PMP" device mode.
If the Link Quality, Link Quality Common, Link Capacity, RSSI and Remote RSSI values are highlighted in orange, the connection quality is deteriorating. If the values are highlighted in red, this indicates a significant deterioration in the connection. It is recommended to take measures to improve the connection conditions. |
Below are examples of the "Wireless Peer"/"Wireless Clients" submenus in the "Access Point PTP", "Access Point PMP", and "STA" device modes, respectively.
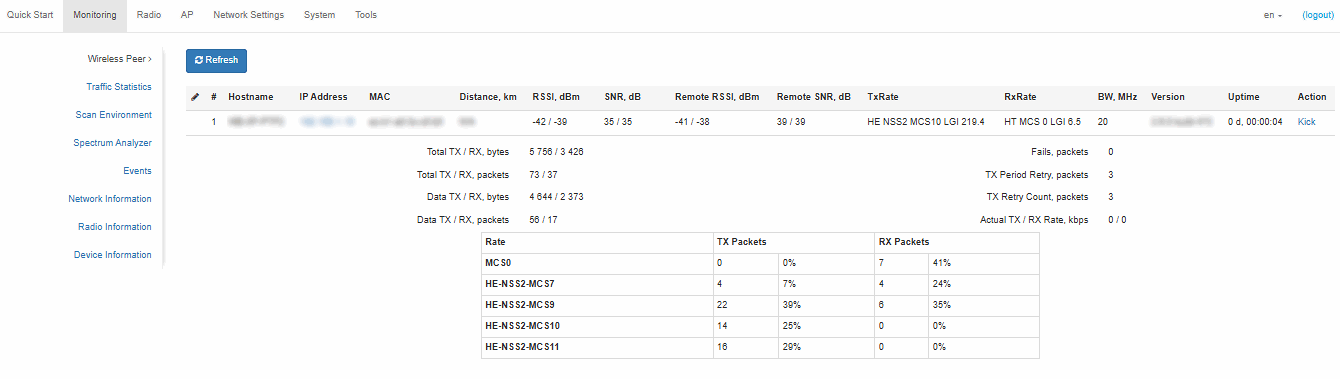
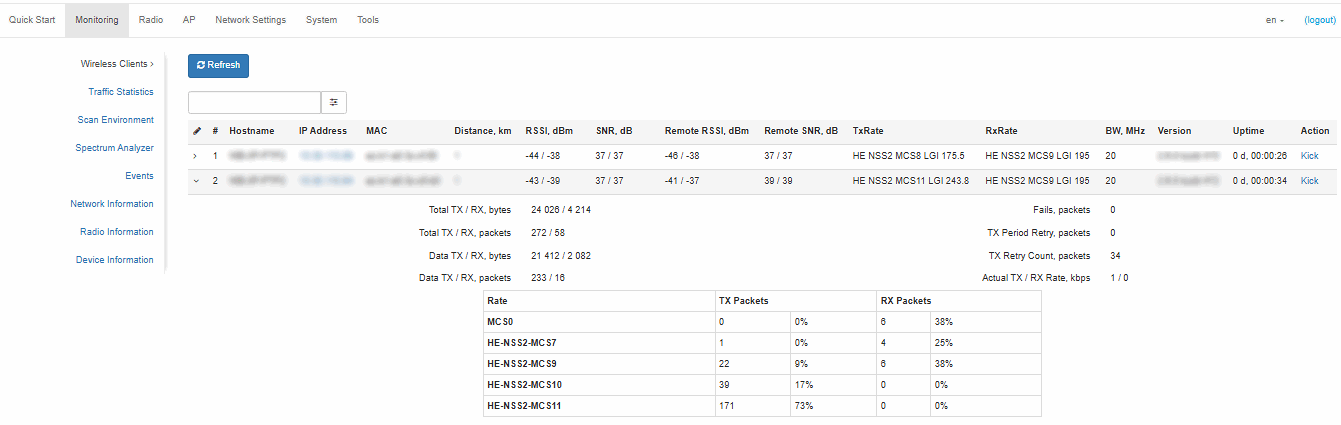
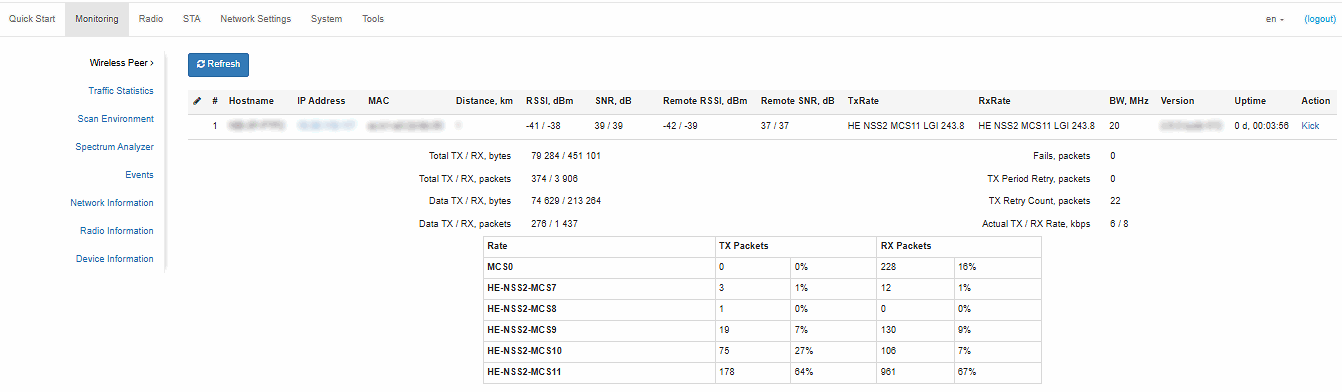
- # — number of the connected device in the list;
- Hostname — device network name;
- IP Address — IP Address of the connected device;
- MAC — MAC of the connected device;
- Distance — distance to the remote device, km;
- Link Capacity — parameter that displays the efficiency of modulation on the transmission used by the device. It is calculated based on the number of packets transmitted to the remote device on each modulation, and the reduction factors. The maximum value is 100% (meaning that all packets are transmitted to the remote device at maximum modulation for the maximum Nss type supported by a remote device). The minimum value is 2% (in the case when the packets are transmitted on the modulation Nss1MCS0 for a remote device with MIMO 3×3 support). The parameter value is calculated for the last 10 seconds;
- Link Quality — parameter that displays the status of the link to a remote device, calculated based on the number of retransmit packets sent to the remote device. The maximum value is 100% (all transmitted packets were sent on the first attempt), the minimum value is 0% (no packets were successfully sent to the remote device). The parameter value is calculated for the last 10 seconds;
- Link Quality Common — parameter that displays the status of the link to a remote device, calculated based on the number of retransmit packets sent to the remote device. The maximum value is 100% (all transmitted packets were sent on the first attempt), the minimum value is 0% (no packets were successfully sent to the remote device). The parameter value is calculated for the entire remote device connection time;
- RSSI — received signal level, dBm;
- SNR — signal-to-noise ratio, dB;
- Remote RSSI — received signal level of a remote device, dBm;
- Remote SNR — signal-to-noise ratio of a remote device, dB;
- TxRate — channel data transfer rate, Mbps;
- RxRate — channel data reception rate, Mbps;
- BW — transmission bandwidth of the wireless channel, MHz;
- Actual TX Rate — average data transfer rate over the last 10 seconds, Mbit/s;
- Actual RX Rate — average data reception rate over the last 10 seconds, Mbit/s;
- Version — firmware version of the connected device;
- Uptime — connection time;
- Action — if to press "Kick" button, the connection with the connected device will be broken. After disconnecting, the device will reconnect;
- Total TX/RX, bytes — number of bytes sent/received on the connected device;
- Total TX/RX, packets — number of packets sent/received on the connected device;
- Data TX/RX, bytes — number of data bytes sent/received on the connected device;
- Data TX/RX, packets — number of data packets sent/received on the connected device;
- Fails, packets — number of packets sent with errors on the connected device;
- TX Period Retry, packets — number of transmission retries to the connected device in the last 10 seconds;
- TX Retry Count, packets — number of transmission retries to the connected device during the entire connection;
- Actual TX/RX Rate, Kbps — current traffic transmission rate at the moment.
"Traffic Statistics" submenu
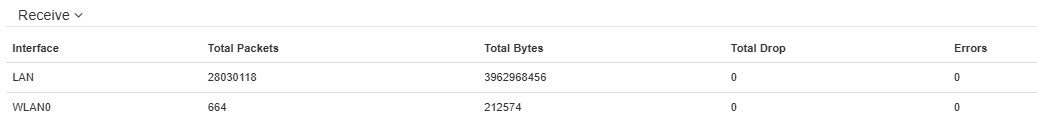
The "Traffic Statistics" submenu displays traffic reception/transmission rate graphs for the last 3 minutes, as well as information on the amount of transmitted/received traffic since the device was turned on.
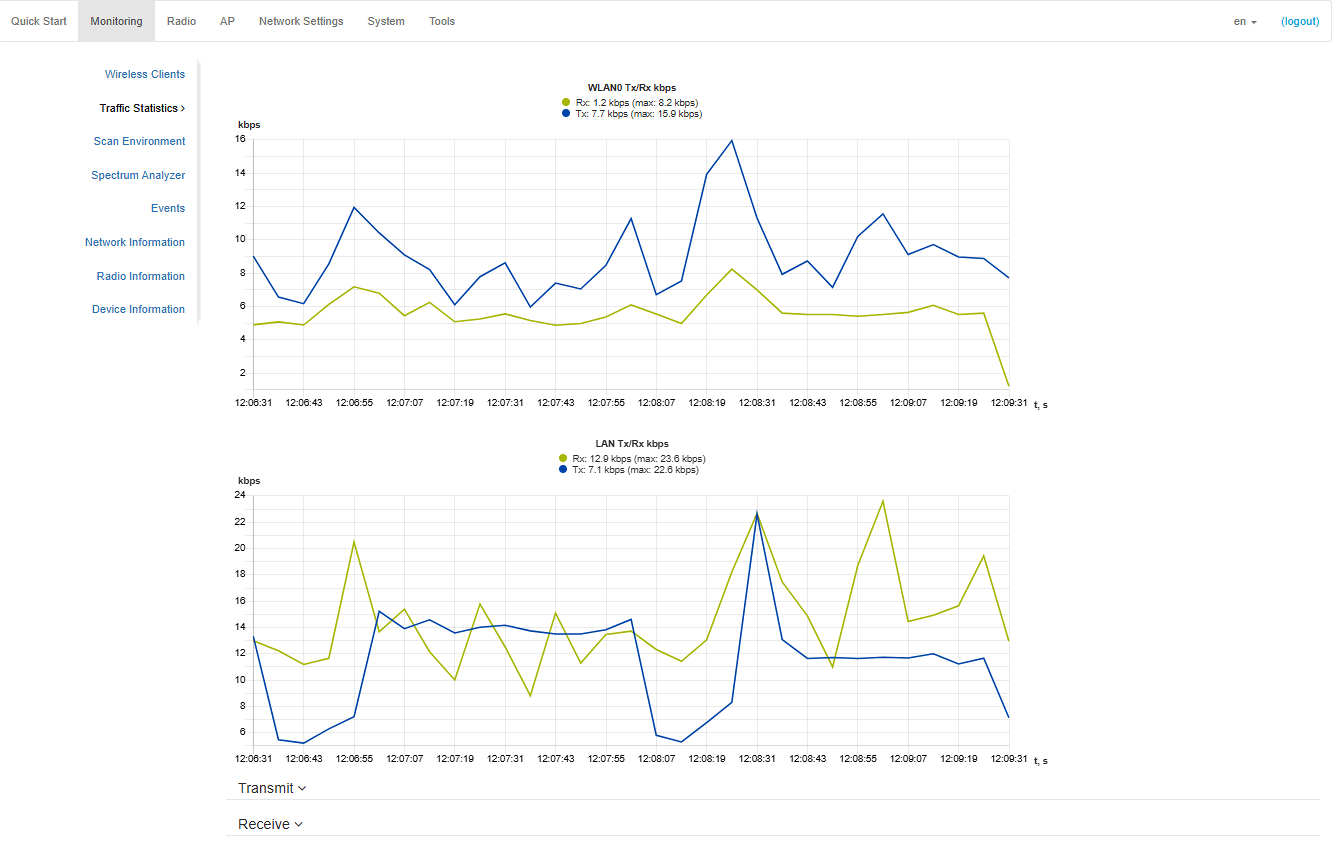
The LAN Tx/Rx graph shows the rate of the transmitted/received traffic via Ethernet interface of the device for the last 3 minutes. The graph is automatically updated every 6 seconds.
The WLAN0 Tx/Rx graph shows the rate of transmitted/received traffic via Radio interface of the device for the last 3 minutes. The graph is automatically updated every 6 seconds.
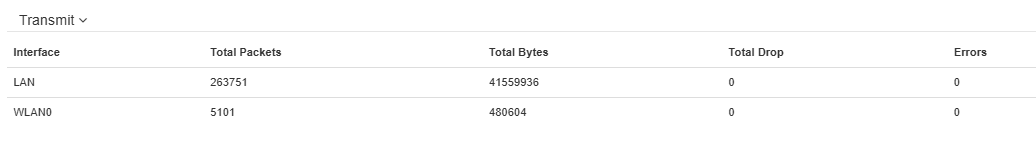
"Transmit" table description:
- Interface — name of the interface;
- Total Packets — number of successfully sent packets;
- Total Bytes — number of successfully sent bytes;
- Total Drop — number of rejected packets;
- Errors — number of errors.
"Receive" table description:
- Interface — name of the interface;
- Total Packets — number of successfully received packets;
- Total Bytes — number of successfully received bytes;
- Total Drop — number of rejected packets;
- Errors — number of errors.
"Scan Environment" submenu
In the "Scan Environment" submenu, air scanning and detection of neighboring devices are carried out.
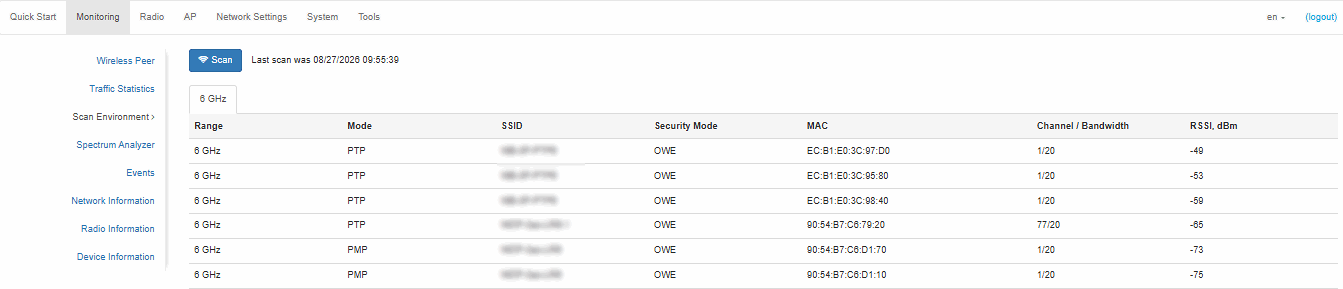
To start the scanning process, click the "Scan" button. After scanning is complete, a list of detected devices and information about them will appear:
- Last scan was... — date and time of the last scan;
- Range — specifies the 6 GHz range, in which the device was detected;
- Mode — device radio interface operating mode;
- SSID — SSID of the detected device;
- Security mode — security mode of the detected device;
- MAC — MAC address of the detected device;
- Channel/Bandwidth — radio channel on which the detected device operates;
- RSSI — level with which the device receives the signal of the detected device, dBm.
While scanning the environment, the device radio interface will be disabled, which will make it impossible to transfer data to Wi-Fi clients during scanning. |
"Spectrum Analyzer" submenu
The "Spectrum Analyzer" submenu is used to launch and monitor the spectrum analyzer.
On the WB-3P-PTP6 devices, it is possible to launch the spectrum analyzer on the Radio 6 GHz radio interface.
Launching the spectrum analyzer on the radio interface
When the spectrum analyzer is launched, the radio interface will be switched to scanning mode, which will interrupt all Wi-Fi connections on this radio interface. |
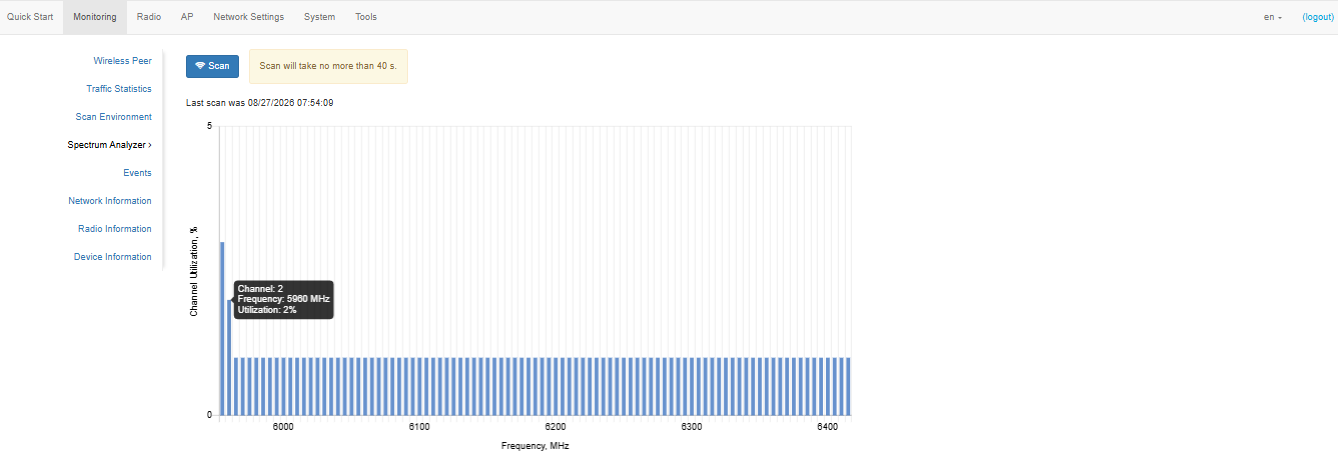
To start the spectrum analyzer, click the "Scan" button. The information window located to the right of the button displays the time in seconds that has passed since the start of the scan. The spectrum analyzer operation time on Radio 6 GHz is no more than 1 minute.
- Last scan was... — date and time of the last scan;
- Channel Utilization — information about the radio channel congestion, expressed as a percentage;
- Frequency, MHz — channel frequency, on which scanning was performed, MHz;
- Channel — channel number corresponding to a given frequency.
The spectrum analyzer analyzes all channels in the range, regardless of the radio interface settings. |
"Events" submenu 
In the "Events" submenu, it is possible to view a list of real-time informational messages which contains the following information:
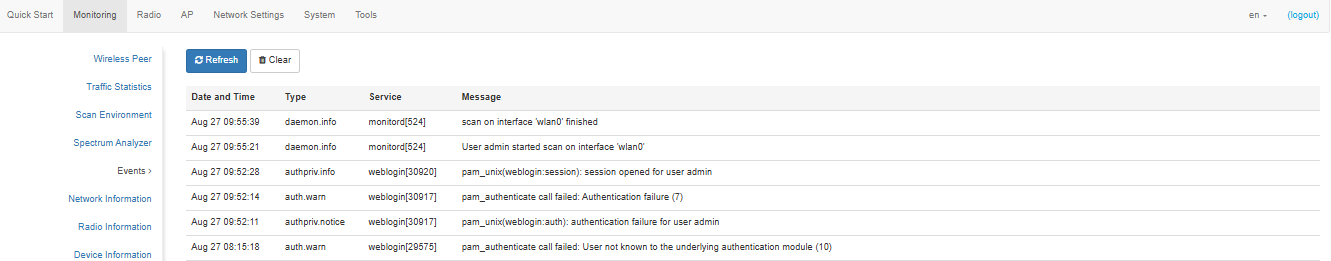
- Date and Time — date and time when the event was generated;
- Type — category and severity level of the event;
- Service — name of the process that generated the message;
- Message — event description.
Table 5 — Description of event severity levels
Level | Type message importance | Description |
|---|---|---|
| 0 | Emergency | A critical error has occurred in the system, the system may not work properly |
| 1 | Alert | Immediate intervention is required |
| 2 | Critical | A critical error has occurred in the system |
| 3 | Error | An error has occurred in the system |
| 4 | Warning | Warning, non-emergency message |
| 5 | Notice | System notice, non-emergency message |
| 6 | Informational | Informational system messages |
| 7 | troubleshooting | Troubleshooting messages provide the user with information to correctly configure the system |
To receive new messages in the event log, click "Refresh".
If necessary, all old messages can be deleted from the log by clicking the "Clear" button.
"Network Information" submenu
In the "Network Information" submenu, general network settings of the device can be viewed.
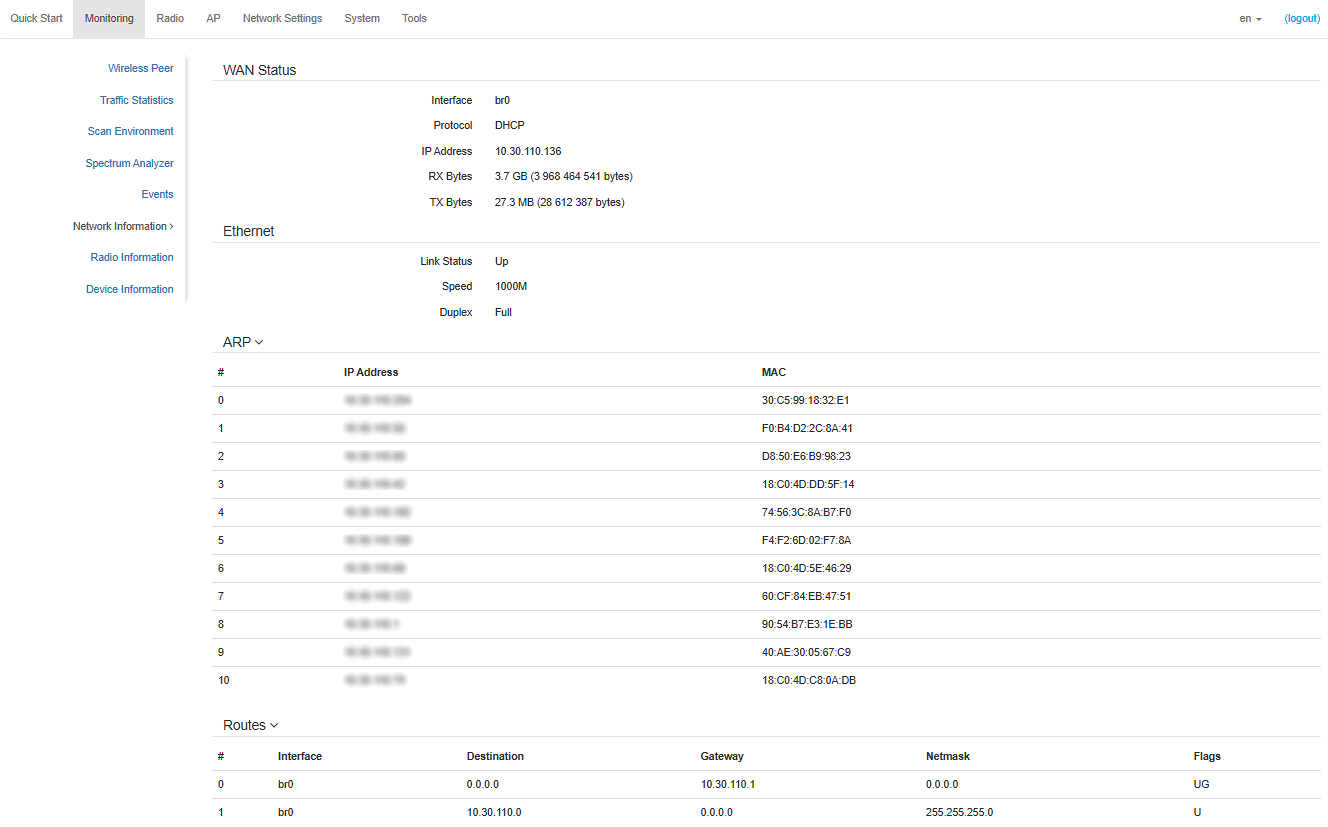
WAN Status:
- Interface — name of the bridge interface;
- Protocol — protocol used for access to WAN;
- IP address — device IP address in external network;
- RX Bytes — number of bytes received on WAN;
- TX Bytes — number of bytes sent from WAN.
Ethernet:
- Link Status — Ethernet port status;
- Speed — Ethernet port connection speed;
- Duplex — data transfer mode:
- Full — full duplex;
- Half — half-duplex.
ARP:
The ARP table contains mapping information between IP and MAC addresses of neighboring network devices:
- IP address — device IP address;
- MAC — device MAC address
Routes:
- Interface — name of the bridge interface;
- Destination — IP address of destination host or subnet that the route is established to;
- Gateway — IP address of the gateway through which access to the destination is carried out;
- Netmask — subnet mask;
- Flags — certain route characteristics.
The following flag values exist:
- U — means that the route is created and passable;
- H — indicates the route to the specific host;
- G — means that the route lies through the external gateway. System network interface provides routes in the network with direct connection. All other routes lie through the external gateways. G flag is used for all routes except for the routes in the direct connection networks;
- R — indicates that the route was most likely created by a dynamic routing protocol running on the local system using the reinstate parameter;
- D — indicates that the route was added as a result of receiving an ICMP Redirect Message. When the system learns the route from the ICMP Redirect message, the route will be added into the routing table in order to exclude redirection for the following packets intended for the same destination;
- M — means that the route was modified — likely by a dynamic routing protocol running on a local system with the "mod" parameter applied;
- A — points to a buffered route to which an entry in the ARP table corresponds;
- C — means that the route source is the core routing buffer;
- L — indicates that the destination of the route is one of the addresses of this computer. Such "local routes" exist in the routing buffer only;
- B — means that the route destination is a broadcasting address. Such "broadcast routes" exist in the routing buffer only;
- I — indicates that the route is connected to a ring (loopback) interface for a purpose other than to access the ring network. Such “internal routes” exist in the routing buffer only;
- ! — means that datagrams sent to this address will be rejected by the system.
"Radio Information" submenu
In the "Radio Information" submenu, the current status of the device radio interface is displayed.
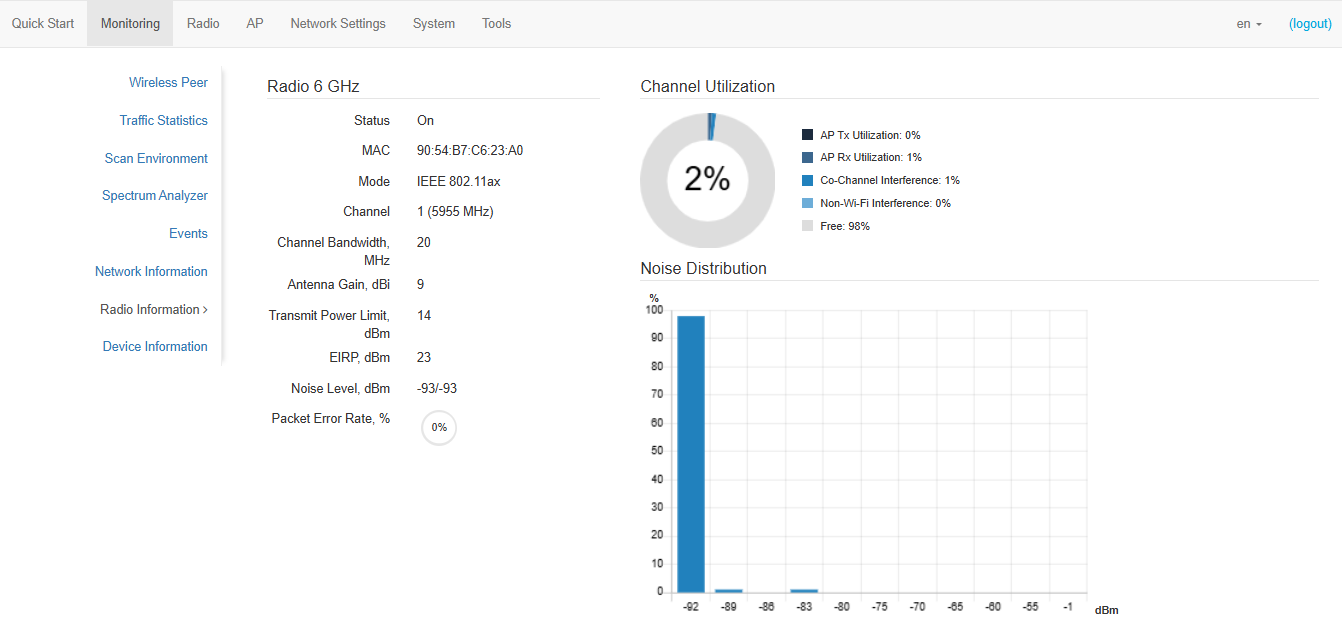
The device radio interface can be in two states: "On" or "Off". Depending on the interface status, the following information is available for monitoring:
"Off":
- Status — radio interface status;
- MAC — MAC radio interface;
"On":
- Status — radio interface status;
- MAC — MAC address of radio interface;
- Mode — radio interface operating mode in accordance with IEEE 802.11 standards;
- Connection status — client connection status (STA) to the access point (AP). Available only for "STA" device mode;
- Channel — wireless channel number on which the radio interface operates;
- Channel Bandwidth, MHz — channel bandwidth on which the radio interface operates;
- Antenna Gain, dBi — gain of the selected antenna;
- Transmit Power Limit, dBm — signal power at which the radio interface operates;
- EIRP, dBm — effective isotropic-radiated power;
- Noise Level, dBm — noise level on the channel where the radio interface operates;
- Packet Error Rate, % — proportion of packets that were received but contained errors and were dropped.
"Channel Utilization":
The "Channel utilization" diagram displays radio channel utilization expressed as a percentage. The total channel utilization (value in the center of the diagram) is calculated as the sum of the following components:
- AP Tx Utilization — percentage of time the device actively transmits data through the radio interface;
- AP Rx Utilization — percentage of time the device is busy receiving data on the radio interface;
- Co-Channel Interference — percentage of time the channel is occupied by other Wi-Fi devices using the same or an overlapping channel but not the intended recipient of the signal from the device;
- Non-Wi-Fi Interference — percentage of time the channel is busy due to signals generated by non-802.11 compliant devices;
- Free — percentage of time the channel is idle.
"Noise distribution":
The "Noise Distribution" graph displays statistical air noise distribution, showing the time proportion for each background noise level (dBm).
The data on the page is automatically updated every 5 seconds.
"Device Information" submenu
The "Device Information" the main device characteristics are displayed.
- Product — device model name;
- Hardware Version — device hardware version;
- Factory MAC Address — device WAN interface MAC address, factory set;
- Serial Number — device serial number, factory set;
- Software Version — device firmware version;
- Backup Version — previously installed firmware version;
- Boot Version — device firmware boot version;
- System Time — current time and date, set in the system;
- Uptime — operating time since the last time the device was turned on or rebooted;
- CPU Usage — average percentage of CPU load over the last 5 seconds;
- Memory Usage — percentage of device RAM usage.
"Radio" menu
In the "Radio" menu wireless interface configuration is performed.
"Radio" submenu
The "Radio" submenu configures the main device radio interface parameters.
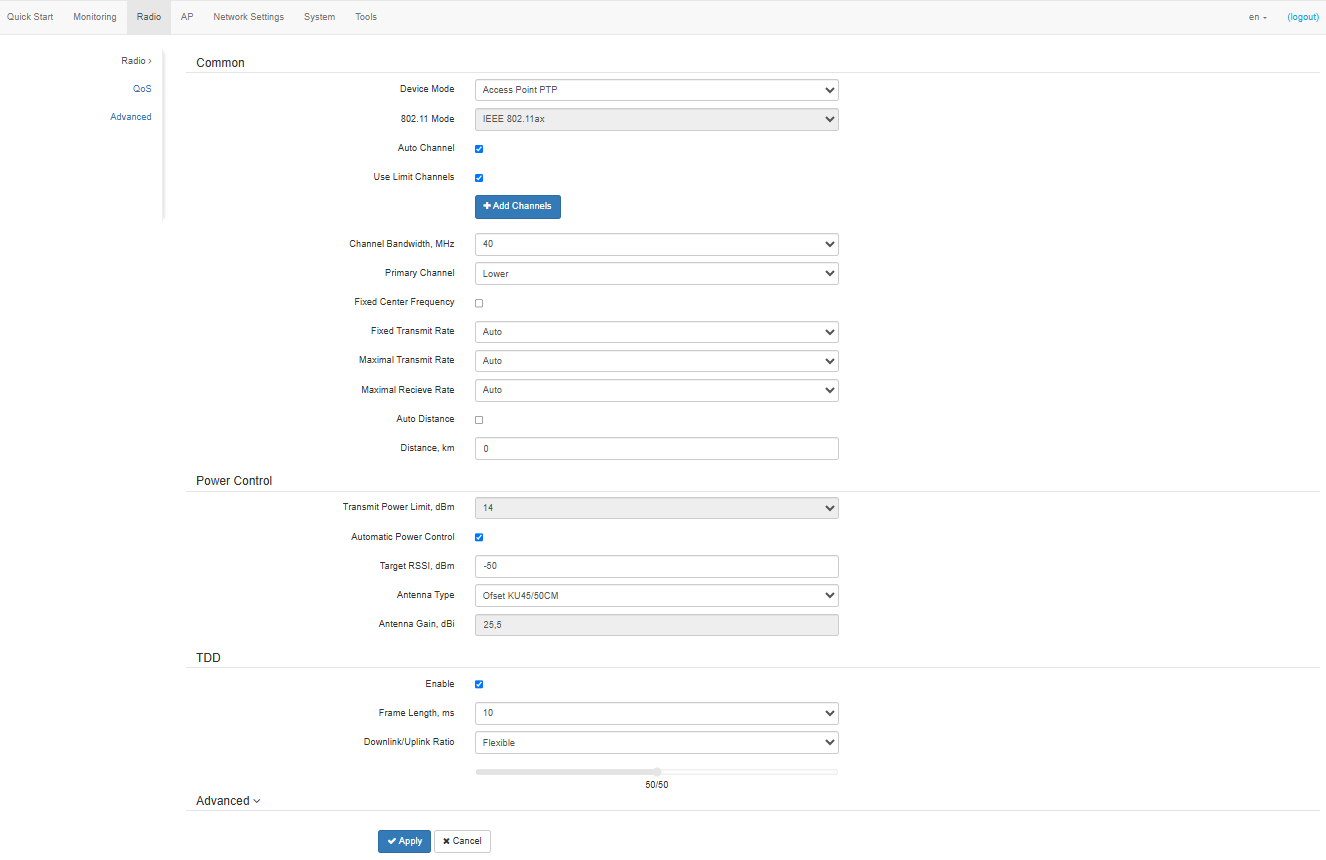
Common:
- Device Mode — operating mode of the device radio interface. The following modes are available:
- Access Point PTP — Point-to-Point;
- Access Point PMP — Point-to-Multipoint;
- Station — wireless client (STA).
- 802.11 Mode — interface operating mode according to standards:
- IEEE 802.11ax;
- Auto Channel — when checked, the device will automatically select the least congested radio channel for the radio interface operation. When unchecked, channel field appears;
- Channel — select channel for data transmission;
- Use Limit Channels — when checked, the device will use a user-defined list of channels to work in automatic channel selection mode. If "Use Limit channels" is unchecked or there are no channels in the list, the device will select the operation channel from all available channels in the given band. The 6 GHz band channels: 1–93;
- Limit Channels — setting is available in the device mode "Station". When checked, the device will use a user-defined list of channels to scan and detect remote devices. If the "Limit Channels" is unchecked or there are no channels in the list, the device will scan all available channels in the given frequency range. The 6 GHz band channels: 1–93;
- Сhannel Bandwidth, MHz — channel bandwidth, on which the device operates. The parameter may take values of 20, 40, 80 and 160 MHz;
- Primary Channel — parameter can only be changed if the bandwidth of a statically specified channel is equal to 40 MHz. The 40 MHz channel can be considered as consisting of two 20 MHz channels, which border in the frequency range. These two 20 MHz channels are called primary and secondary channels:
- Upper — primary channel will be the upper 20 MHz channel in the 40 MHz band;
- Lower — primary channel will be the lower 20 MHz channel in the 40 MHz band.
- Fixed Center Frequency — when checked, all traffic (data and control packets) will be transmitted at the specified channel center frequency with the specified bandwidth (40/80/160 MHz). This feature is proprietary and does not comply with IEEE 802.11 standards, which require the use of different center frequencies for data and control traffic with a channel width of 40/80/160 MHz;
- Fixed Transmit Rate — fixed wireless data transfer rate defined by IEEE 802.11/ax standard specifications;
- Maximal Transmit Rate — maximal wireless data rate of this device as defined by IEEE 802.11ax standard specifications;
- Maximal Receive Rate — maximal wireless data transfer rate of remote device, determined by IEEE 802.11ax standard specifications. Available only in the Access Point PTP and STA device modes;
- Auto Distance — when checked, the device will automatically determine and configure the distance between devices;
- Distance, km — distance between devices in kilometers. Changing the distance value will change the ACK timeout value. The distance should be rounded up. For example, if the distance between devices is 3.2 km, then 4 km should be specified;
The "Channel", "Channel Bandwidth", "Primary Channel" parameters are only available when the device mode is "Access Point PTP" or "Access Point PMP". |
If the "Use Limit Сhannels" list contains a channel that is not available for selection, it will be marked in grey. In order for the new configuration to be applied to the device, only available (blue highlighted) channels must be specified in the "Use Limit channels" list. Example. The device has not yet been configured, the default "Channel Bandwidth" for the 6 GHz Radio is set to 20 MHz, and no channels are listed in the "Use Limit Channels" list. Suppose channels 37, 41, 45, 49 were manually added to the "Use Limit Channels " list and the "Channel Bandwidth" parameter needs to be set to 40 MHz. When changing this parameter from 20 MHz to 40 MHz, the following happens:
If you change the "Channel Bandwidth" parameter to 40 MHz and do not remove the "grey" channels from the list, then clicking the "Apply" button in the browser will display the error — "There are errors in data. Changes were not applied". Accordingly, the device configuration will not be changed. This is due to the fact that channels in the "Use Limit channels" list that are highlighted in grey do not fit the definition "Primary Channel" = Upper. |
The "Maximal Receive Rate" parameter is used to specify the maximal channel transmit rate to a remote device. Therefore, when configuring the maximal channel receive rate, for example, on the client (STA), there is no need to configure the maximal transmit rate on an access point (AP). |
Power Control:
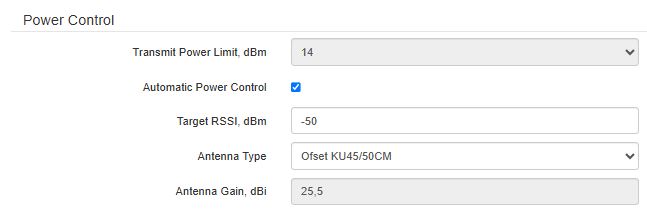
- Transmit Power Limit, dBm — Wi-Fi transmitter signal power adjustment;
- Automatic Power Control — automatic adjustment of Wi-Fi transmitter signal power;
- Target RSSI, dBm — target indicator of received radio signal power;
- Antenna Type — selection of the installed antenna type;
- Antenna Gain, dBi — gain factor for the selected antenna type.
TDD:
TDD — it is a collision-free time-division multiplexing (TDM) technology that synchronizes data transmission in both directions within a time frame:
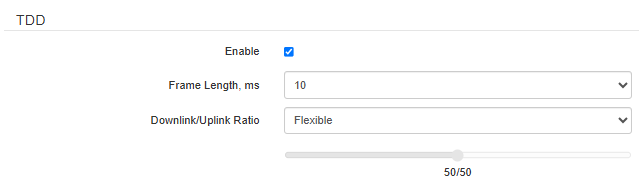
- Enable — when checked, the option is enabled; otherwise — disabled.
- Frame Length, ms — TDD frame duration in milliseconds, takes values of 5, 10 ms;
- Downlink/Uplink Ratio — time-slot ratio in TDD frame between Downlink and Uplink traffic:
- Fixed — manually set of Downlink and Uplink ratio;
- Flexible — dynamic change of the Downlink/Uplink ratio depending on the current channel load.
Advanced:
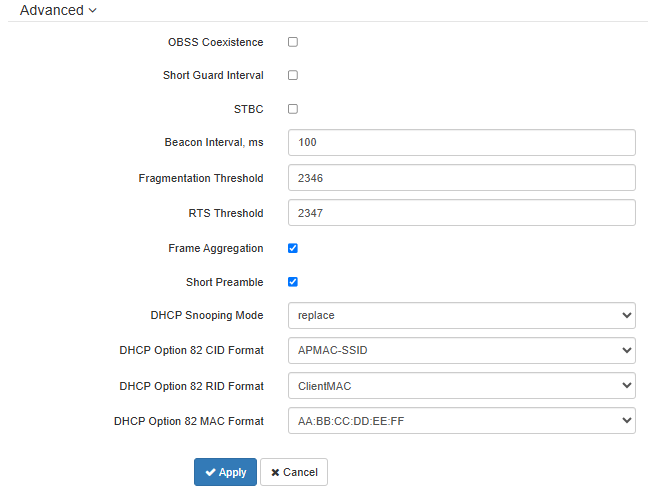
- OBSS Coexistence — automatic channel bandwidth reduction when the channel is loaded. When checked, the mode is enabled;
- Short Guard Interval — support for Short Guard Interval. The device transmits data using 400 ns guard interval (instead of 800 ns) to remote devices which also support Short Guard Interval;
- STBC — Space-Time Block Coding method dedicated to improve data transmission reliability. When checked, the device transmits one data flow through several antennas. When unchecked, the device does not transmit the same data flow through several antennas;
- Beacon Interval, ms — beacon frames transmission period. The frames are sent to detect a remote device in the air. The parameter takes values from 20 to 2000 ms, by default: 100 ms;
- Fragmentation Threshold — frame fragmentation threshold, bytes. The parameter takes values 256–2346, by default: 2346;
- RTS Threshold — number of bytes over which the Request to Send will be sent. Decreasing this value may improve the performance of the device when there are a lot of connected remote devices. However, this reduces general throughput of wireless network. The parameter takes values from 0 to 2347, by default: 2347;
- Frame Aggregation — enable support for AMPDU/AMSDU;
- Short Preamble — use of the packet short preamble;
- DHCP Snooping Mode — selection of DHCP option 82 processing policy. Available values for selection:
- ignore — option 82 processing is disabled. Default value;
- remove — device deletes the value of option 82;
- replace — device substitutes or replaces the value of option 82. When selecting this value to edit, the following parameters are opened:
- DHCP Option 82 CID format — replacement of the CID parameter value, can take values:
- APMAC-SSID — replacement of the CID parameter value to <MAC address of the device>-<SSID name>. Default value;
- SSID — replacement of the parameter value to device SSID name;
- custom — replacement of the CID parameter value to the value specified in the "DHCP Option 82 Custom CID";
- DHCP Option 82 Custom CID — an arbitrary string of up to 52 characters that will be passed to the CID. If the parameter value is not set, the device will change the CID to the default value — APMAC-SSID.
- DHCP Option 82 RID format — replacement of the RID parameter value, can take the following values:
- ClientMAC — change the RID content to the MAC address of the client device. Default value;
- APMAC — change the RID content to the MAC address of the device;
- APdomain — change the RID content to the domain in which the device is located;
- custom — change the RID content to the value specified in the "DHCP Option 82 RID format";
- DHCP Option 82 Custom RID — an arbitrary string of up to 63 characters that will be passed to the RID. If the parameter value is not set, the device will change the RID to the default value — ClientMAC.
- DHCP Option 82 MAC Format — selection of octet delimiters of the MAC address, which is transmitted in CID and RID:
- AA:BB:CC:DD:EE:FF — delimiter is a colon (:). Default value;
- AA-BB-CC-DD-EE-FF — delimiter is a dash (-).
- DHCP Option 82 CID format — replacement of the CID parameter value, can take values:
To apply a new configuration and save settings to non-volatile memory, click the "Apply" button. Click the "Cancel" button to discard the changes.
"QoS" submenu
The "QoS" submenu is used to configure Quality of Service functions.
- Wi-Fi Multimedia (WMM) — WMM (Wi-Fi Multimedia) support activation;
- Enable QoS — when checked, the setting of Quality of Service functions is available.
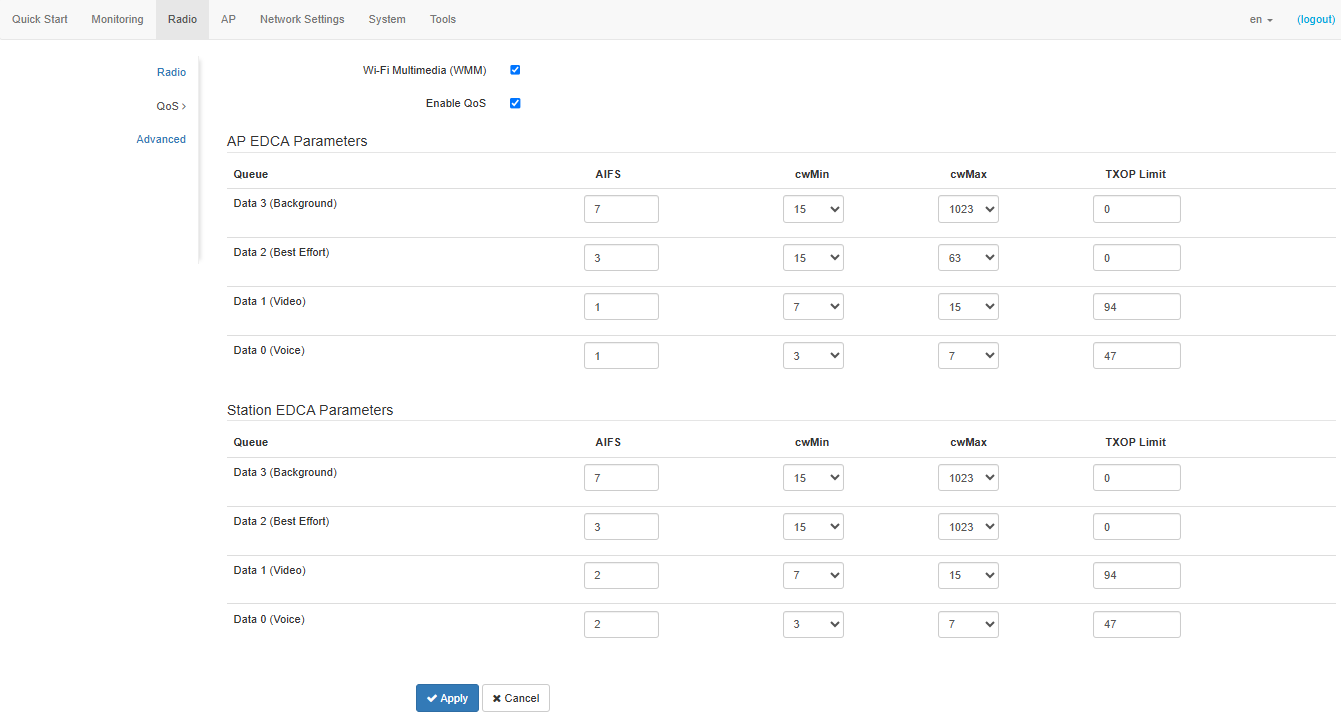
- AP EDCA parameters — device settings (traffic is transmitted to the client device):
- Queue — predefined queues for various kinds of traffic:
- Data 3 (Background) — low priority queue, high bandwidth (802.1p: cs1, cs2 priorities);
- Data 2 (Best Effort) — middle priority queue, middle bandwidth and delay. Most of the traditional IP data is sent to this queue (802.1p: cs0, cs3 priorities);
- Data 1 (Video) — high priority queue, minimal delay. In this queue, time-sensitive video data is automatically processed (802.1p: cs4, cs5 priorities);
- Data 0 (Voice) — high priority queue, minimal delay. In this queue, time sensitive data is automatically processed, such as: VoIP, streaming video (802.1p: cs6, cs7 priorities).
- AIFS — Arbitration Inter-Frame Spacing, defines the waiting time of data frames, measured in slots, takes values 1–255;
- cwMin — initial timeout value before resending a frame, specified in milliseconds, takes the values 1, 3, 7, 15, 31, 63, 127, 255, 511, 1023. The value of cwMin cannot exceed the value of cwMax;
- cwMax — maximum timeout value before resending a frame, specified in milliseconds, takes the values 1, 3, 7, 15, 31, 63, 127, 255, 511, 1023. The value of cwMax must exceed the value of cwMin;
- TXOP Limit — this parameter is used only for data transmitted from the client device. The transmission capability is the time interval, in milliseconds, when the remote WME station has the rights to initiate data transmission over the wireless medium to the device, the maximum value is 65535 milliseconds;
- Queue — predefined queues for various kinds of traffic:
- Station EDCA parameters — table of client device parameter settings (traffic is transmitted from the client device). For description of table fields, see above.
To apply a new configuration and save settings to non-volatile memory, click the "Apply" button. Click the "Cancel" button to discard the changes.
"Advanced" submenu
In the "Advanced” submenu, it is possible to configure advanced radio interface parameters of the device.
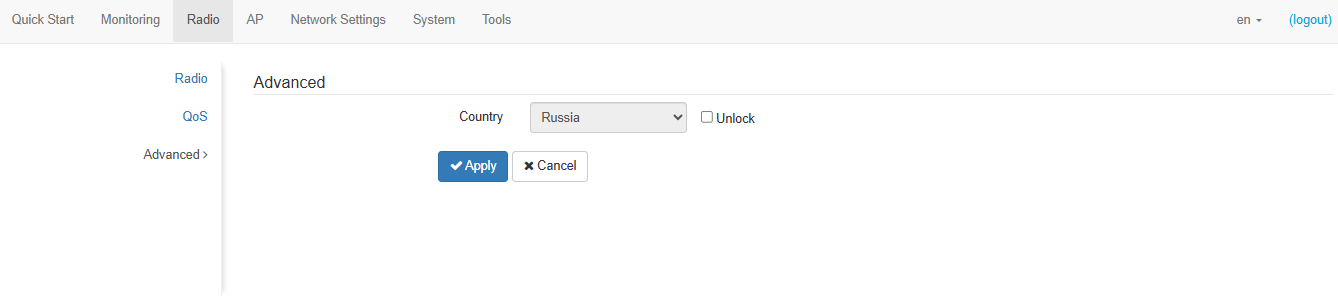
- Country — country of device operation. Select the "Unlock" checkbox to change a country. Depending on the selected value, the channel bandwidth and transmit power limit restrictions will be applied. The list of available frequency channels depends on the selected country, which affects the automatic channel selection in the Channel = Auto mode.
Local country regulations settings, including operation within legal frequency channels and output power, is the installer's responsibility. |
Selecting the wrong region may result in compatibility issues with different client devices. |
To apply a new configuration and save settings to non-volatile memory, click the "Apply" button. Click the "Cancel" button to discard the changes.
"AP" menu
In the "AP" menu access point configuration is performed (AP — Access Point) (then "AP").
The "AP" menu is available only in "Access Point PTP" or "Access Point PMP" device mode. |
"Access Point" submenu
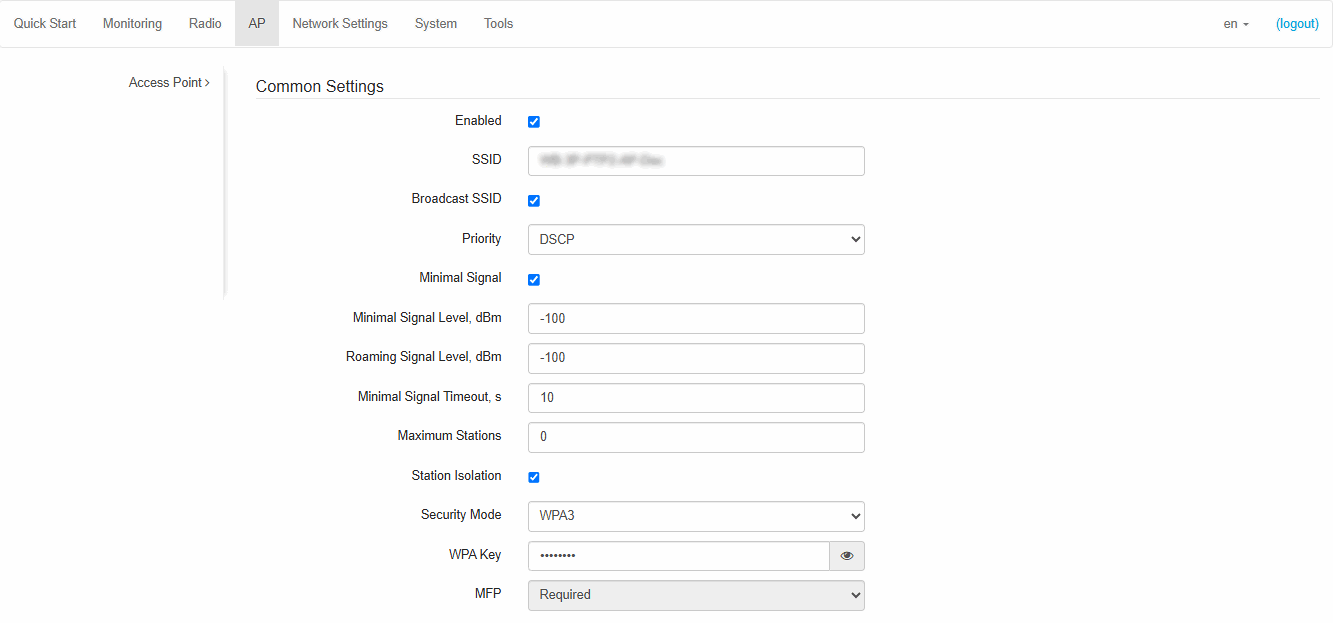
Common Settings:
- Enabled — when checked, the access point (AP) is enabled, otherwise it is disabled;
- SSID — virtual wireless network name;
- Broadcast SSID — when checked, broadcasting to the SSID is enabled, otherwise it is disabled;
- Priority — prioritization method. Defines the field based on which traffic transmitted to the radio interface will be distributed among WMM queues:
- DSCP — priority from the DSCP field of IP packet header will be analyzed;
- 802.1p — priority from the CoS (Class of Service) field of tagged packets will be analyzed.
- Minimal Signal — when checked, the function of disconnecting client devices at a low signal level (Minimal Signal) is enabled. For the functionality to work, the following parameters need to be configured:
- Minimal Signal Level, dBm — signal level, below which the client devices are disconnected from the wireless network;
- Roaming Signal Level, dBm — roaming sensitivity level, below which the client devices switch to another device. The parameter should be higher than the "Minimal Signal Level": if the "Minimal Signal Level" is -75 dBm, then the "Roaming Signal Level" should be, for example, -70 dBm;
- Minimal Signal Timeout, s — the period of time after which a decision is made to disconnect the client equipment from the wireless network.
- Maximum Stations — maximum number of client devices allowed to connect to the wireless network;
- Station Isolation — when checked, traffic isolation between connected devices is enabled;
- Security Mode — wireless network access security mode:
- OWE (Opportunistic Wireless Encryption) — encryption method that ensures the security of data transmitted over an unsecured network. Users are not required to take any additional actions or enter a password to connect to the network;
- WPA3 — encryption method, when selected the following setting will be available:
- WPA Key — key/password required to connect to the wireless network. The key length is from 8 to 63 characters.
- WPA3-Enterprise — a wireless link encryption mode in which the device authenticates via a centralized RADIUS server. This security mode requires specifying RADIUS server parameters. Selecting one of these methods makes the following RADIUS setting available (see below).
- MFP — management frame protection available in WPA3, WPA3-Enterprise, OWE. When WPA3, WPA3-Enterprise, OWE is selected, MFP is set to Required):
- Required — management frame protection is enabled. The device can not connect to the wireless network, that does not support MFP.
"Maximum Stations" and "Station Isolation" are available only in the "Access Point PMP" device modes. |
MAC ACL:
In this subsection, one can configure a list of MAC addresses of remote devices that are allowed or prohibited from connecting to this device, depending on the selected access policy.
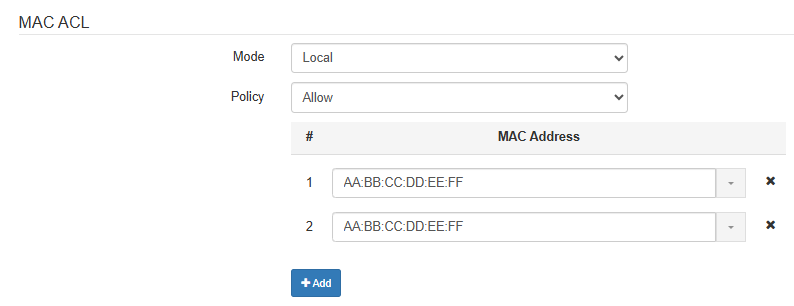
- Mode — selection of the access control mode by MAC:
- Off — function is not active;
- Local — check MAC by list on the device;
- RADIUS — check MAC via RADIUS server.
- Policy — access policy. Acceptable values:
- Deny — remote devices whose MAC addresses are on the list will be prohibited from connecting to this device. All other devices will be allowed access;
- Allow — only those remote devices whose MAC addresses are in the list will be allowed to connect to this device. All others will be denied access.
- MAC address — list of MAC addresses of remote devices that are allowed or denied access to this device. This list can contain up to 128 addresses.
To add an address to the list, click If it becomes necessary to add MAC of the connected device to the list: click at the end of the row By default the list displays up to 10 addresses. To view the full list if it contains more than 10 addresses, click the "Show All" button. |
 and enter MAC in the field that appears. To remove an address from the list, click the button
 in the corresponding row.
 and select the required address from the list; it will be automatically added to the field.
RADIUS:
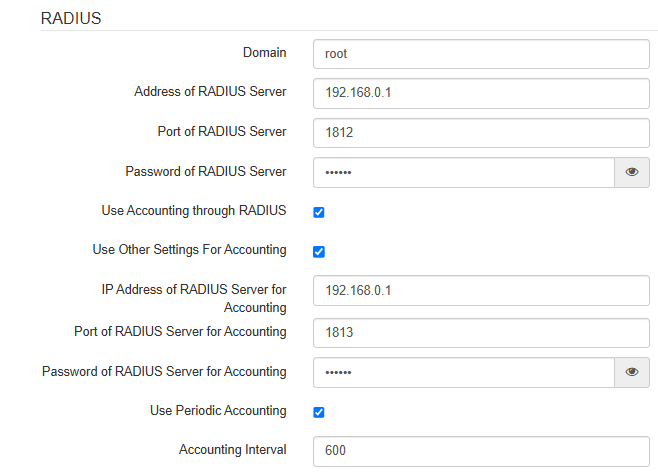
- Domain — user domain;
- Address of RADIUS Server — RADIUS server address;
- Port of RADIUS Server — port of RADIUS server that used for authentication and authorization;
- Password of RADIUS Server — password for RADIUS server used for authentication and authorization;
- Use Accounting through RADIUS — when checked, "Accounting" messages will be sent to the RADIUS server;
- Use Other Settings For Accounting:
- IP Address of RADIUS Server for Accounting — address of the RADIUS server, used for accounting;
- Password of RADIUS Server for Accounting — password for the RADIUS server used for accounting.
- Port of RADIUS Server for Accounting — port that will be used to collect accounts on the RADIUS server;
- Use Periodic Accounting — enable periodic sending of "Accounting" messages to the RADIUS server. The interval for sending messages can be set in the "Accounting Interval" field.
VLAN:
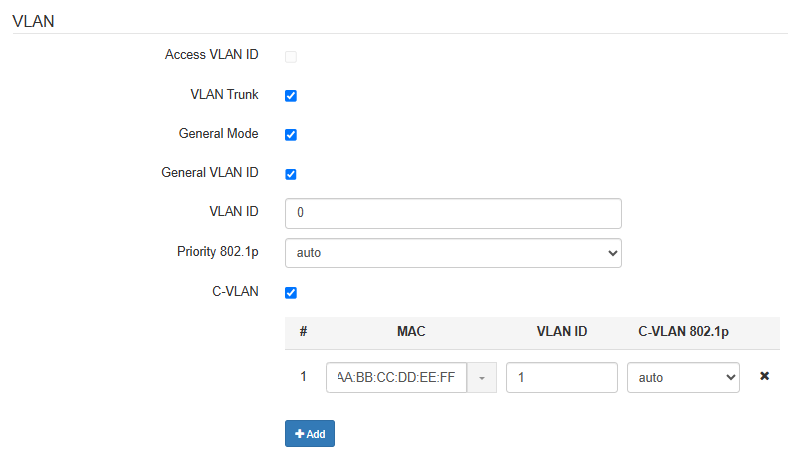
- Access VLAN ID — VLAN number from which the tag will be removed when transmitting traffic to client devices. When traffic passes in the opposite direction, untagged traffic from client devices will be tagged with a VLAN ID (available when VLAN Trunk mode is disabled);
- VLAN Trunk — when checked, tagged traffic is transmitted to client devices;
- General Mode — when checked, client devices are allowed to transmit untagged traffic together with tagged traffic (available when VLAN Trunk mode is enabled);
- General VLAN ID — VLAN number from which the tag will be removed when forwarding traffic to client devices. When passing traffic in the opposite direction, untagged traffic from client devices will be tagged with the General VLAN ID (available when VLAN Trunk and General Mode are enabled);
- Priority 802.1p — 802.1p priority number assigned to traffic tagged with a VLAN ID using the Access VLAN ID or General VLAN ID functionality (available when Access VLAN ID or General VLAN ID is enabled);
- C-VLAN — when checked, lists of MAC addresses of remote devices are configured, assigning them an isolated VLAN ID and an 802.1p priority:
- MAC — MAC address of the remote device;
- VLAN ID — VLAN number from which the tag will be removed when forwarding traffic to the remote device. When passing traffic in the opposite direction, untagged traffic from the remote device will be tagged with the VLAN ID;
- C-VLAN 802.1p — 802.1p priority number assigned to traffic that is tagged with a VLAN ID using the C-VLAN functionality.
To add an address to the list, click If there is a need to add the MAC address of a connected device to the list: click By default the list displays up to 10 addresses. To view the full list if it contains more than 10 addresses, click the "Show All" button. |
Mapping VLAN:
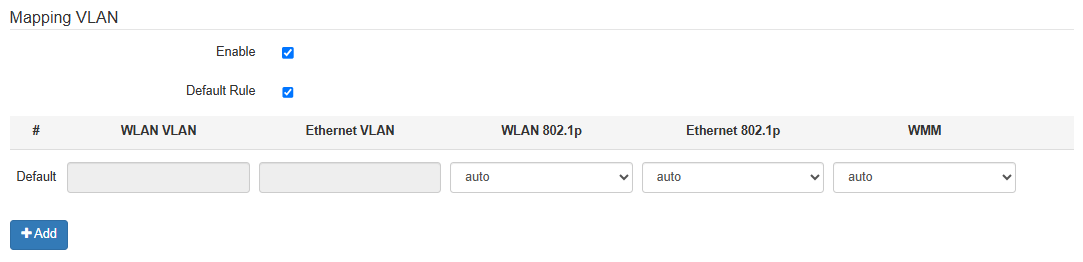
- Enable — when checked, the VLAN Mapping function is enabled, otherwise — disabled;
- Default Rule — when checked, the rule is activated; otherwise it disables the rule. The default rule determines the system's behavior for VLAN packets that don't match any explicitly defined user rules. It automatically assigns 802.1p priority and a WMM queue to such packets:
- WLAN VLAN — VLAN ID number when transmitting in WLAN. Takes values: 1–4094;
- Ethernet VLAN — VLAN ID number when transmitting to Ethernet. Takes values: 1–4094;
- WLAN 802.1p — 802.1p priority when transmitting in WLAN. Takes values: 0–7, auto. By default — auto;
- Ethernet 802.1p — 802.1p priority when transmitting to Ethernet. Takes values: 0–7, auto. By default — auto;
- WMM — WMM queue for this rule. Takes values: bk, be, vi, vo, auto. If the queue is not set to auto, the DSCP priority will be analyzed in the packet.
Works only when enabled VLAN Trunk. To add a rule to the list, click By default the list displays up to 9 addresses. To view the full list if it contains more than 9 addresses, click the button "Show All". |
Shapers:
For the device mode "Access Point PTP":
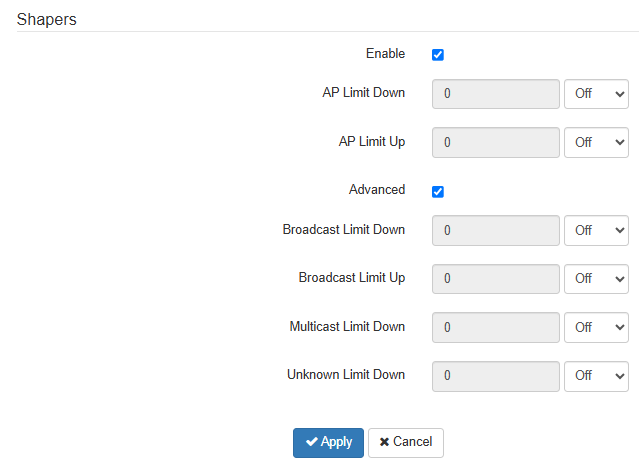
Enable — activate the settings field:
- AP Limit Down — bandwidth limiting in the direction from access point (AP) to client (STA);
- AP Limit Up — bandwidth limiting in the direction from client (STA) to access point (AP).
Advanced — activate the additional settings field:
- Unknown Limit Down
The following parameters are available for configuring restrictions:
- Off — bandwidth limiting is not applied;
- kbps — bandwidth limiting in kbps;
- pps — bandwidth limiting
For the "Access Point PMP" device mode:
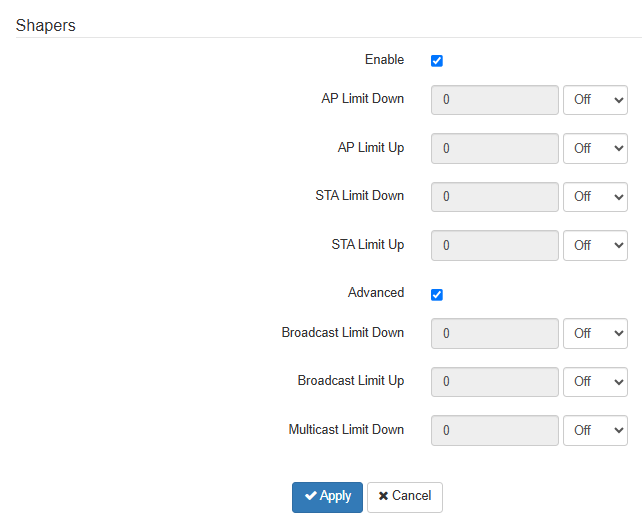
Enable — activate the settings field;
- AP Limit Down — bandwidth limiting in the direction from access point (AP) to client devices;
- AP Limit Up — bandwidth limiting in the direction from client devices to access point (AP);
- STA Limit Down
- STA Limit Up
Advanced — activate the additional settings field:
The following parameters are available for configuring restrictions:
- Off — bandwidth limiting is not applied;
- kbps — bandwidth limiting in kbps/s;
- pps — bandwidth limiting
After Changing "SSID" on the access point (AP) access to client devices may be lost. You must first change "SSID" on client devices in the "STA" menu, and then on the access point (AP) In the "AP" menu. |
"STA" menu
In the "STA" menu client configuration is performed (STA — Station) (then "STA").
The "STA" menu is only available in the "Station" device mode. |
"Station" submenu
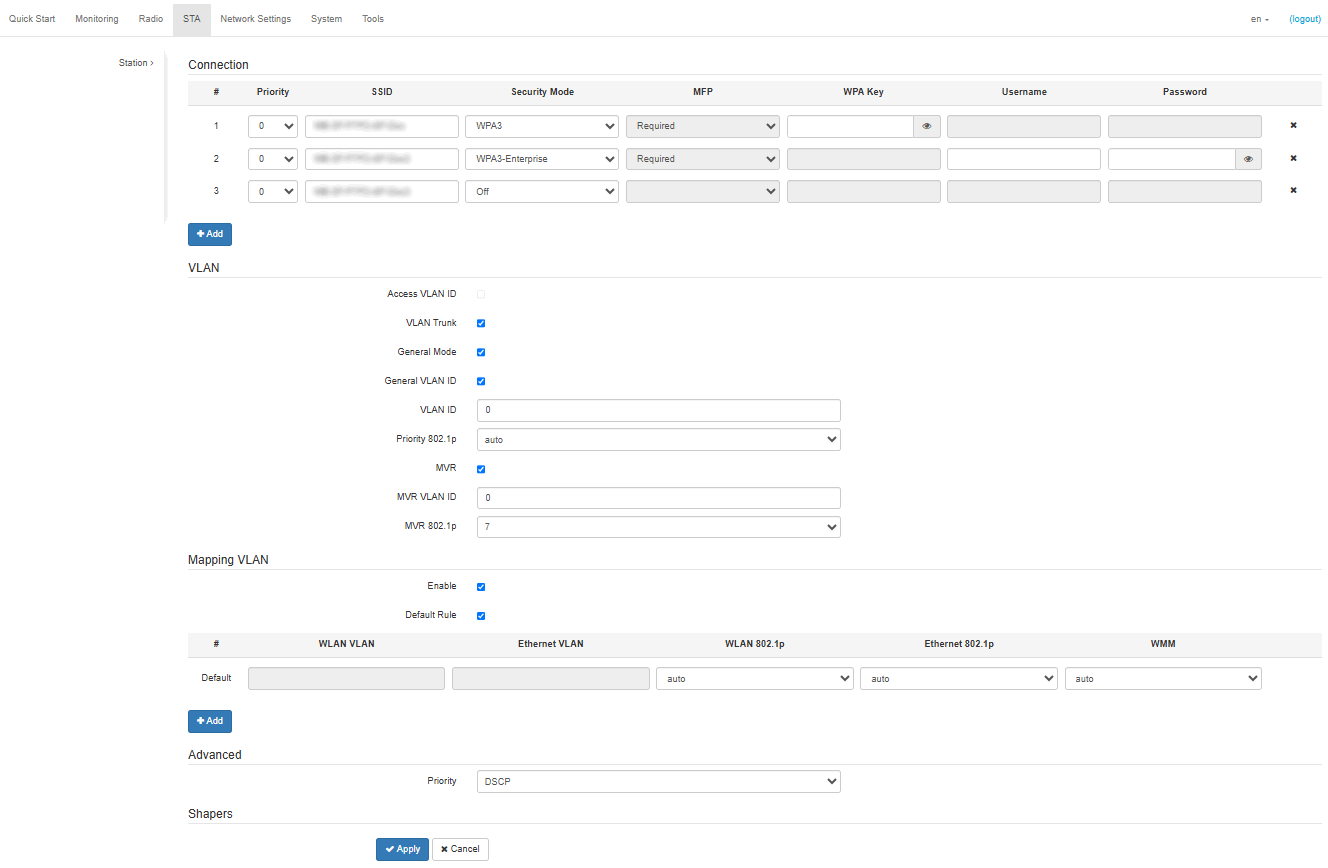
Connection:
- Priority — determines the order of profile usage. When searching for a network and connecting, the device uses the highest priority profile first. If priorities are equal, the device determines profile usage order based on encryption mode and RSSI;
- SSID — virtual wireless network name;
- Security Mode — wireless network access security mode:
- OWE (Opportunistic Wireless Encryption) — encryption method that ensures data security transmitted over an unsecured network.
- WPA3 — encryption method; the following settings become available when selected:
- WPA Key — key/password, required to connect to the wireless network. The key length is from 8 to 63 characters.
- WPA3-Enterprise — wireless channel encryption mode in which the device authenticates on a centralized RADIUS server. To use this security mode, connection parameters must be specified:
- Username — login, required for authorization on RADIUS-on the server;
- Password — key/password, required for authorization on RADIUS server.
- MFP — protection management frames (available for WPA3, WPA3-Enterprise, OWE security modes. When selecting the security mode WPA3, WPA3-Enterprise, OWE MFP is switched to Required):
- Required — protection is enabled. The device cannot connect to a wireless network that does not support MFP.
To add a new connection profile, click "Add profile". Maximum 8 profiles can be added.
VLAN:
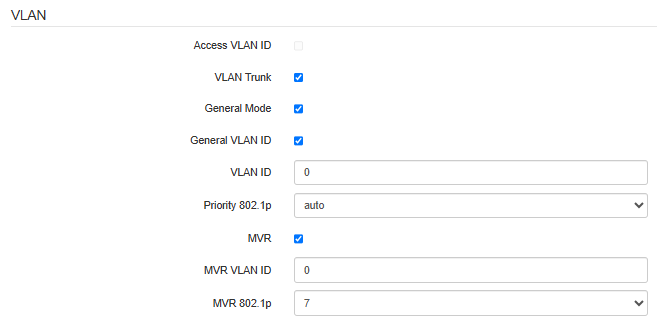
VLAN:
- Access VLAN ID — VLAN number from which the tag will be removed when forwarding traffic to Ethernet devices connected to the client (STA). When passing traffic in the opposite direction, untagged traffic will be tagged with VLAN ID (available when VLAN Trunk mode is disabled);
- VLAN Trunk — when checked, tagged traffic is transmitted to Ethernet devices connected to the client (STA);
- General Mode — when checked, Ethernet devices connected to the client (STA) are allowed to transmit untagged traffic with tagged traffic (available when VLAN Trunk mode is enabled);
- General VLAN ID — VLAN number from which the tag will be removed when transmitting traffic to Ethernet devices, connected to the client (STA). When traffic passes in the opposite direction, untagged traffic will be tagged with General VLAN ID (available when VLAN Trunk and General Mode are enabled);
- Priority 802.1p — 802.1p priority number assigned to traffic that is tagged with a VLAN ID using the Access VLAN ID or General VLAN ID functionality (available when Access VLAN ID or General VLAN ID is enabled);
- MVR — when checked, the MVR (Multicast VLAN Registration) functionality is enabled. Allows to use a separate VLAN for Multicast traffic;
- MVR VLAN ID — VLAN number of multicast traffic that will be untagged when transmitted to Ethernet devices connected to the client (STA). When traffic passes in the opposite direction, untagged IGMP packets from clients will be tagged with MVR VLAN ID;
Mapping VLAN:
- Enable — when checked, the function is enabled VLAN Mapping, otherwise — disabled;
- Default rule — when checked, the rule is activated; otherwise it disables the rule. The default rule defines system behavior for VLAN-Packets that do not match any user-defined rules. It allows automatically assigning priority to such packets 802.1p and queue WMM:
- WLAN VLAN — VLAN ID number when transmitting in WLAN. Takes values: 1–4094;
- Ethernet VLAN — VLAN ID number when transmitting to Ethernet. Takes values: 1–4094;
- WLAN 802.1p — priority 802.1p when transmitting in WLAN. Takes values: 0–7, auto. By default — auto;
- Ethernet 802.1p — priority 802.1p when transmitting to Ethernet. Takes values: 0–7, auto. By default — auto;
- WMM — WMM queue for this rule. Takes values: bk, be, vi, vo, auto. If the auto queue is not defined in this option, the DSCP priority in the packet will be analyzed.
Works only when enabled VLAN Trunk. To add a rule to the list, click By default the list displays up to 9 addresses. To view the full list if it contains more than 9 addresses, click the button "Show All". |
Advanced:
- Priority — prioritization method selection. Defines the field for distributing traffic entering the radio interface among queues WMM:
- DSCP — priority from the DSCP field of the IP packet header will be analyzed;
- 802.1p — priority from the CoS (Class of Service) field of tagged packets will be analyzed.
Shapers:
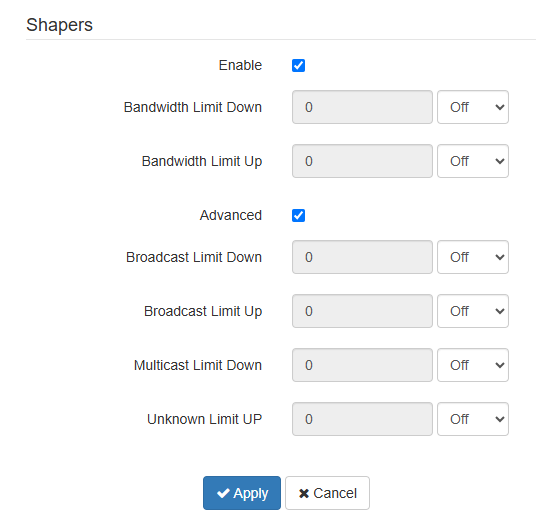
Enable — activate the settings field:
- Bandwidth Limit Down — bandwidth limiting in the direction from the client (STA) to Ethernet devices;
- Bandwidth Limit Up — bandwidth limiting in the direction from Ethernet devices to client (STA).
Advanced — activate the additional settings field:
- Unknown Limit UP
The following parameters are available for configuring restrictions:
- Off — bandwidth limiting is not applied;
- kbps — bandwidth limiting in kbps;
- pps — bandwidth limiting
To apply a new configuration and save settings to non-volatile memory, click the "Apply" button. Click the "Cancel" button to discard the changes.
"Network Settings" menu
"System Configuration" submenu
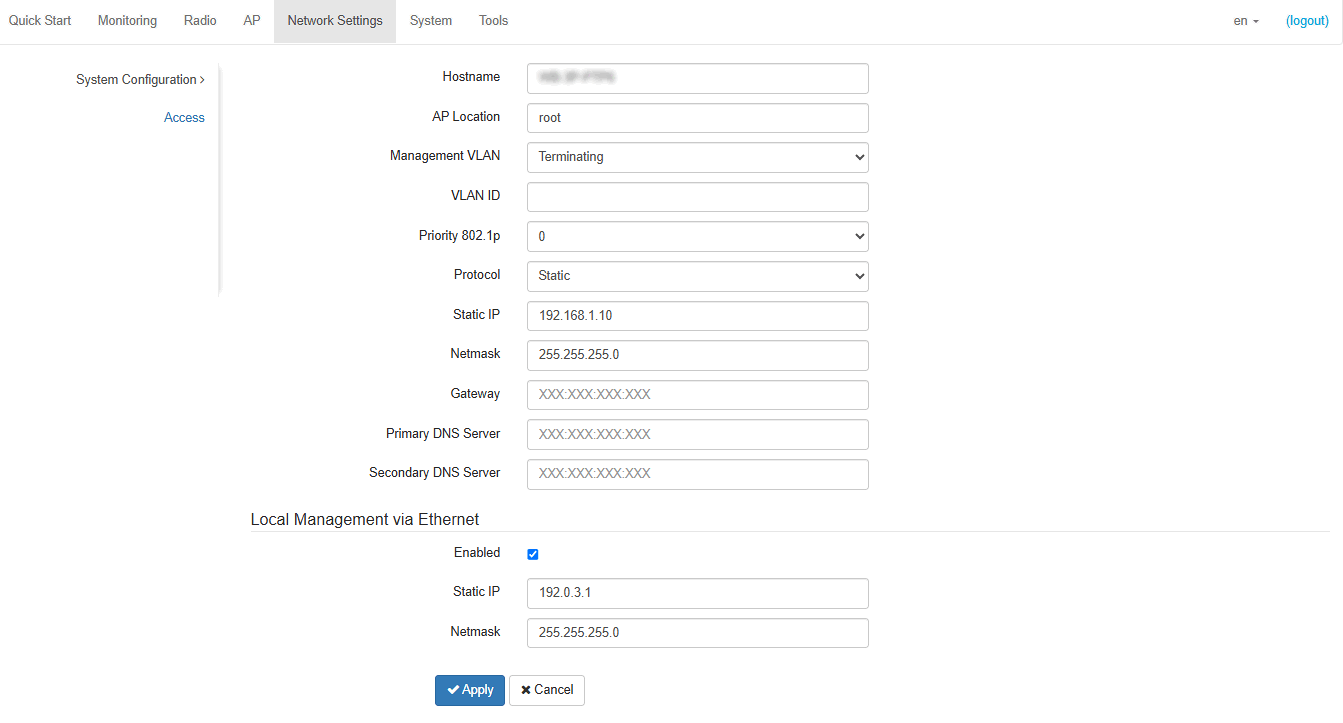
- Hostname — device network name, set as a string 1–63 characters: Latin uppercase and lowercase letters, digits, and the hyphen character "-" (a hyphen cannot be the last character in the name);
- AP Location — domain where the device is located;
- Management VLAN:
- Off — Management VLAN is not used;
- Terminating — mode in which Management VLAN is terminated on the device. In this case, remote devices connected via the radio interface have no access to the VLAN;
- Forwarding — mode in which Management VLAN is also transmitted to the radio interface (with the appropriate AP settings).
- VLAN ID — VLAN identifier used for device access; accepts values 1–4094;
- Priority 802.1p — 802.1p priority number, assigned to packets outgoing from Management VLAN interface of the device;
- Protocol — select protocol for connecting a device via Ethernet interface to the service provider network:
- DHCP — operating mode in which IP address, subnet mask, DNS server address, default gateway, and other parameters required for network operation will be obtained from the DHCP server automatically;
- Static — operating mode in which IP address and all necessary parameters on WAN interface is assigned statically. When selecting the "Static" type, the following parameters become available for editing:
- Static IP — IP address of WAN device interface in the provider network;
- Netmask — external subnet mask;
- Gateway — address to which a packet is sent if no route is found for it in the routing table.
- Primary DNS Server, Secondary DNS Server — IP Address of DNS servers. If addresses of DNS servers are not assigned automatically via the protocol DHCP, set them manually.
After "Management VLAN" configuration, access to the device may be lost. |
Local Management via Ethernet:
This subsection allows configuring untagged access to the device via Ethernet interface.
- Enabled — activates the setting;
- — IP address of device Ethernet interface in the local network (by default 192.0.3.1);
- subnet mask.
To apply a new configuration and save settings to non-volatile memory, click the "Apply" button. Click the "Cancel" button to discard the changes.
"Access" submenu
The "Access" configures device access via web interface, Telnet, SSH, NETCONF and SNMP.
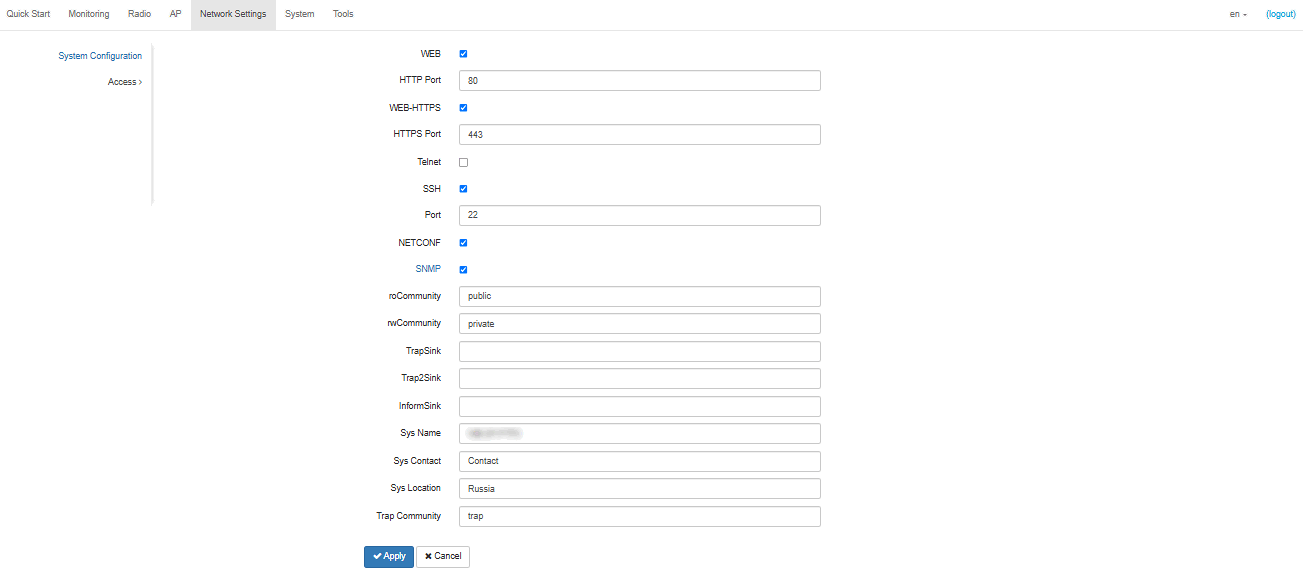
- To enable access to the device via the web interface via HTTP protocol, select the checkbox next to "WEB". In the window that appears, it is possible to change the HTTP port (by default: 80). The range of acceptable values of ports, in addition to the default, is from 1025 to 65535 inclusive;
- To enable access to the device via the web interface via HTTPS protocol, select the checkbox next to "WEB-HTTPS". In the window that appears, it is possible to change the HTTPS port (by default: 443). The range of acceptable values of ports, in addition to the default, is from 1025 to 65535 inclusive;
Note that the ports for the HTTP and HTTPS protocols should not have the same value.
- To enable access to the device via Telnet, select the checkbox next to "Telnet". In the window that appears, it is possible to change the Telnet port (23 by default). The range of acceptable port values, in addition to the default, is from 1025 to 65535 inclusive;
- To enable access to the device via SSH, select the checkbox next to "SSH". In the window that appears, it is possible to change the SSH port (22 by default). The range of acceptable port values, in addition to the default, is from 1025 to 65535 inclusive;
- To enable access to the device via NETCONF, select the checkbox next to "NETCONF".
The WB-3P-PTP6 software allows changing the device configuration, monitoring its status, as well as managing the device using the SNMP protocol.
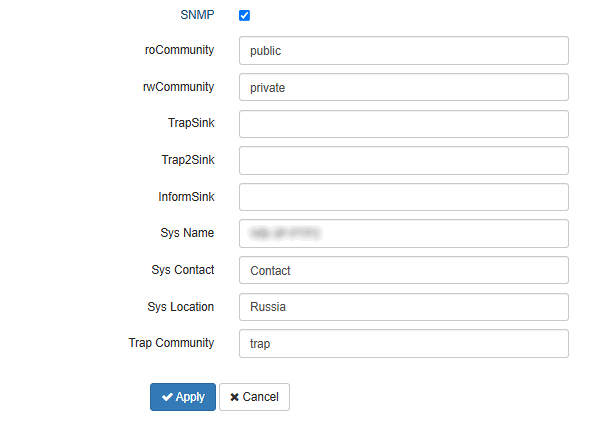
The device supports SNMPv1, SNMPv2, SNMPv3 protocols.
To change the SNMP settings, select the checkbox next to "SNMP", the following SNMP agent options become available:
- roCommunity — password to read the parameters (by default: public);
- rwCommunity — password to configure (write) parameters (by default: private);
- TrapSink — IP address or domain name of SNMPv1-trap message recipient in HOST [COMMUNITY [PORT]] format;
- Trap2Sink — IP address or domain name of SNMPv2-trap message recipient in HOST [COMMUNITY [PORT]] format;
- InformSink — IP address or domain name of Inform message recipient in HOST [COMMUNITY [PORT]] format;
- Sys Name — device name;
- Sys Contact — device vendor contact information;
- Sys Location — device location information;
- Trap community — password enclosed in traps (default value: trap).
The list of objects which are supported for reading and configuring via SNMP is given below:
- eltexLtd.1.127.1 — monitoring of device parameters;
- eltexLtd.1.127.3 — device management;
- eltexLtd.1.127.5 — device configuring.
where eltexLtd — 1.3.6.1.4.1.35265 is Eltex Enterprise ID.
To apply a new configuration and save settings to non-volatile memory, click "Apply”. Click "Cancel" to discard the changes.
"System" menu
In the "System" menu, the user can configure the system, time, syslog, change the password, upload/download the configuration, upgrade the firmware, and reboot the device.
"Device Firmware Upgrade" submenu
The "Device Firmware Upgrade" submenu is intended for upgrading the device firmware.
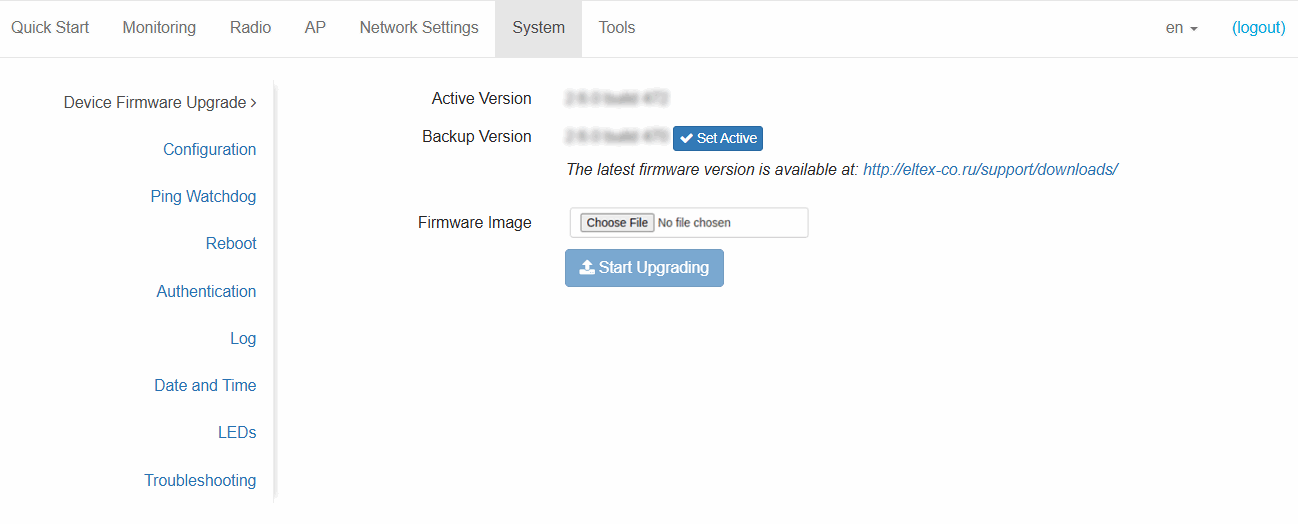
Active Version — installed firmware version, which is operating at the moment;
- Backup Version — installed firmware version that can be switched to without downloading a firmware file;
- Set active — button that allows making a backup version of the firmware active, this will require a device reboot. The active firmware version will not be set as a backup.
Firmware upgrade
Download the firmware file from http://eltex-co.com/support/downloads/ and save it on the PC. After that, click "Choose File" in the Firmware Image field and specify the path to the firmware file in .tar.gz format.
To start the update process, click the "Start Upgrading" button. The process may take several minutes (its current status will be shown on the page). The device will be automatically rebooted when the upgrade is completed.
The firmware should be upgraded first on the client (STA) and then on the access point (AP). |
Do not switch off or reboot the device during a firmware upgrade. |
"Configuration" submenu
In the "Configuration" submenu, the current configuration can be saved and updated.
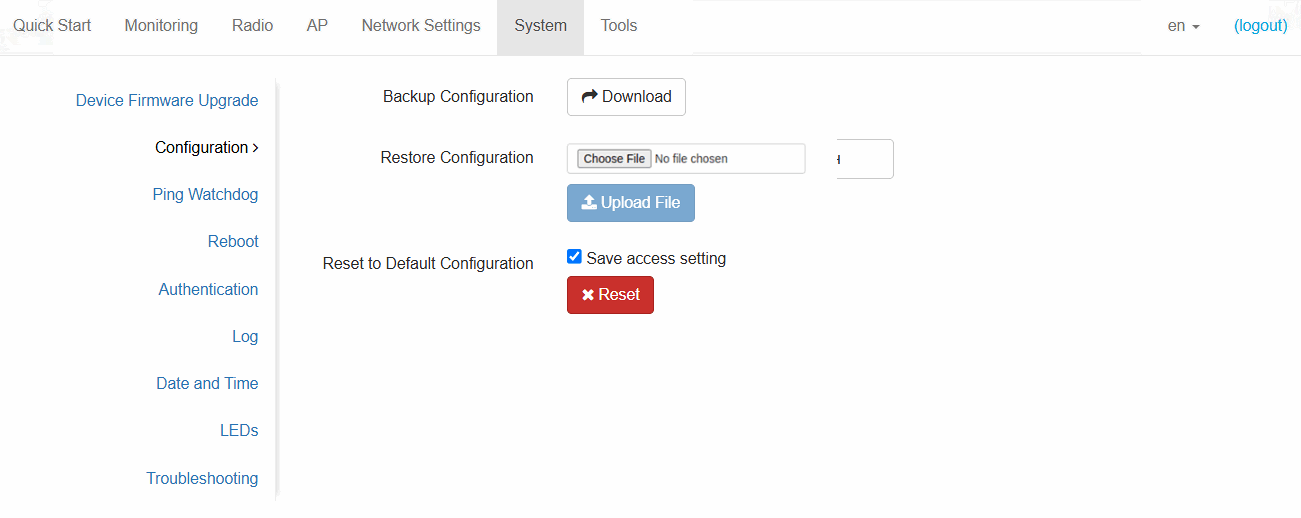
Backup Configuration
To save the current device configuration to local computer, click the "Download" button.
Restore Configuration
To upload the configuration file saved on the local computer, use the Restore Configuration item. To update the device configuration, click the "Chose File" button, specify a file (in .tar.gz format) and click the "Upload File" button. Uploaded configuration will be applied automatically and does not require device reboot.
Reset to Default Configuration
To reset all the settings to default values, click the "Reset" button. If the "Save access setting" checkbox is selected, then those configurations settings, that are responsible for access to the device (IP address settings, Telnet/SSH/SNMP/Netconf/Web access settings) will be saved.
"Ping Watchdog" submenu
The availability monitoring feature detects connectivity issues and reboots the device or its interfaces without user intervention. Restarting an interface also restarts the DHCP client on the current WAN interface.
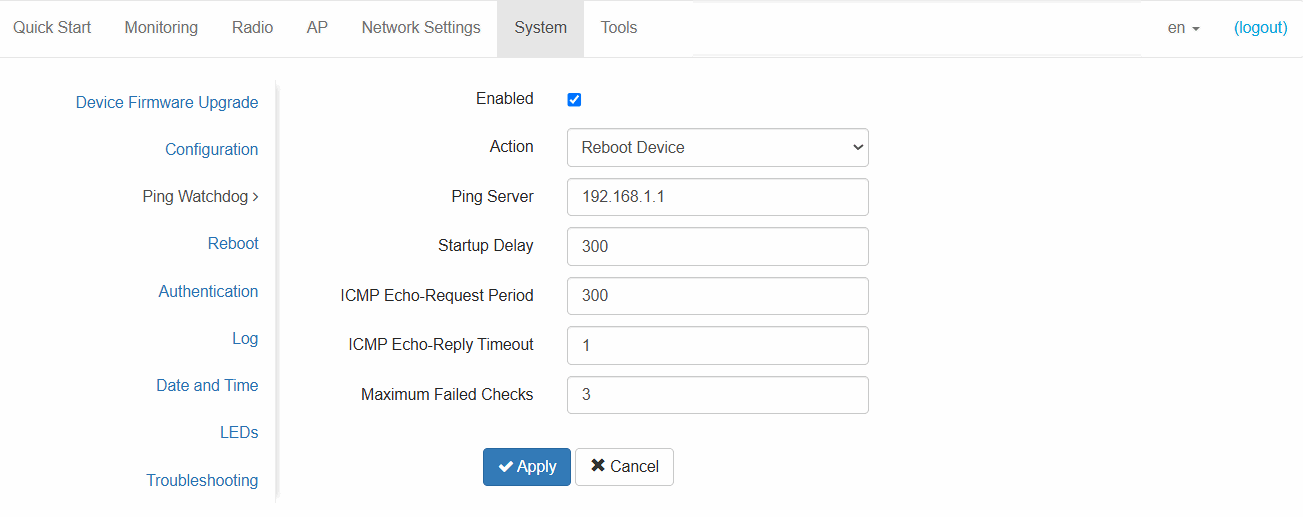
- Enabled — when checked, the ping watchdog feature is enabled, otherwise it is disabled;
- Action:
- Restart Ethernet Interface — if the specified Ping server is unavailable, the device Ethernet interface will restart;
- Restart Wireless Interface — if the specified Ping server is unavailable, the device wireless interface will restart;
- Reboot Device — if the specified Ping server is unavailable, the device will reboot.
- Ping Server — IP address or host domain name, where ICMP requests will be sent;
- Startup Delay — time in seconds after the device is powered on or the previous trigger, during which the availability monitoring will not operate. Acceptable values: 60–86400 inclusive;
- ICMP Echo-Request Period — time in seconds after which an ICMP request will be sent when receiving an ICMP reply or deciding that the previous ICMP request was unsuccessful. Acceptable values: 1–86400 inclusive;
- ICMP Echo-Reply Timeout — time in seconds during which an ICMP reply is expected after sending an ICMP request. If an ICMP reply is not received within this time, the ICMP request is considered unsuccessful. Acceptable values: 1–10 inclusive;
- Maximum Failed Checks — maximum number of failed ICMP requests. If the number of failed ICMP requests reaches the specified value, the designated action is performed. Acceptable values: 1–86400 inclusive.
To apply a new configuration and save settings to non-volatile memory, click "Apply”. Click "Cancel" to discard the changes.
"Reboot" submenu
To reboot the device, click the "Reboot" button. The device reboot process takes about 1 minute.
"Authentication" submenu
The "Authentication" submenu is used for configuring user authentication.
Authentication:
Factory account for device access: login: admin, password: password. |
Local
When enabled, authentication is performed using an account stored on this device.
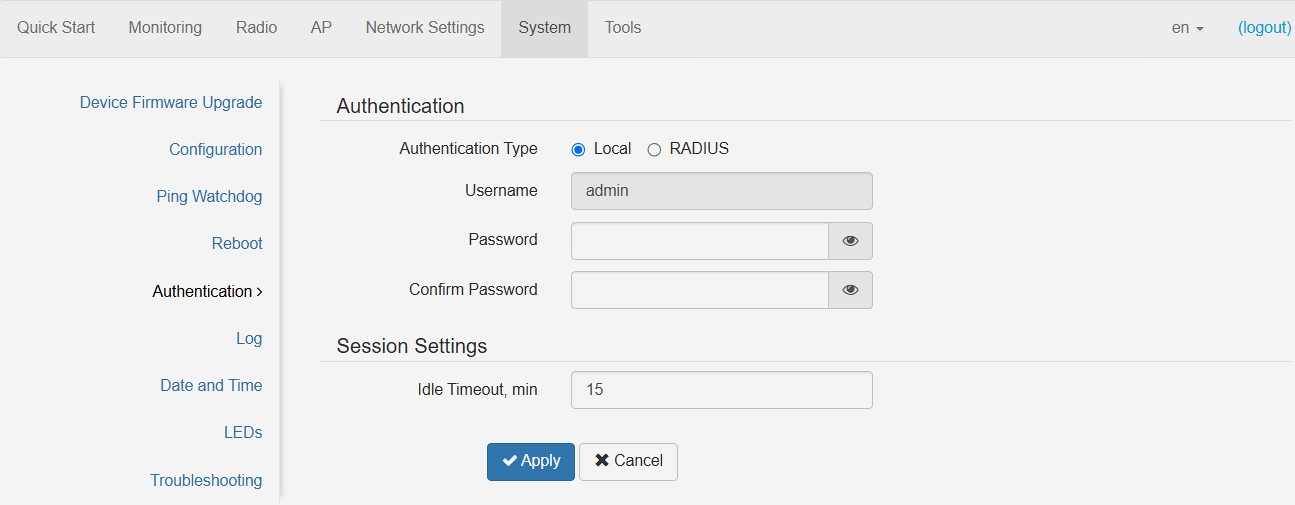
- Username — login of the configured account;
- Password — entering a new password;
- Confirm Password — confirming the new password.
Additional accounts with administrator or viewer roles can also be created (the setting is available only via CLI). Accounts with the administrator role have full access to the device: read and write access to any settings, full device status monitoring. Accounts with the viewer role have monitoring access only.
RADIUS
When enabled, authentication will be performed using an account on the RADIUS server.
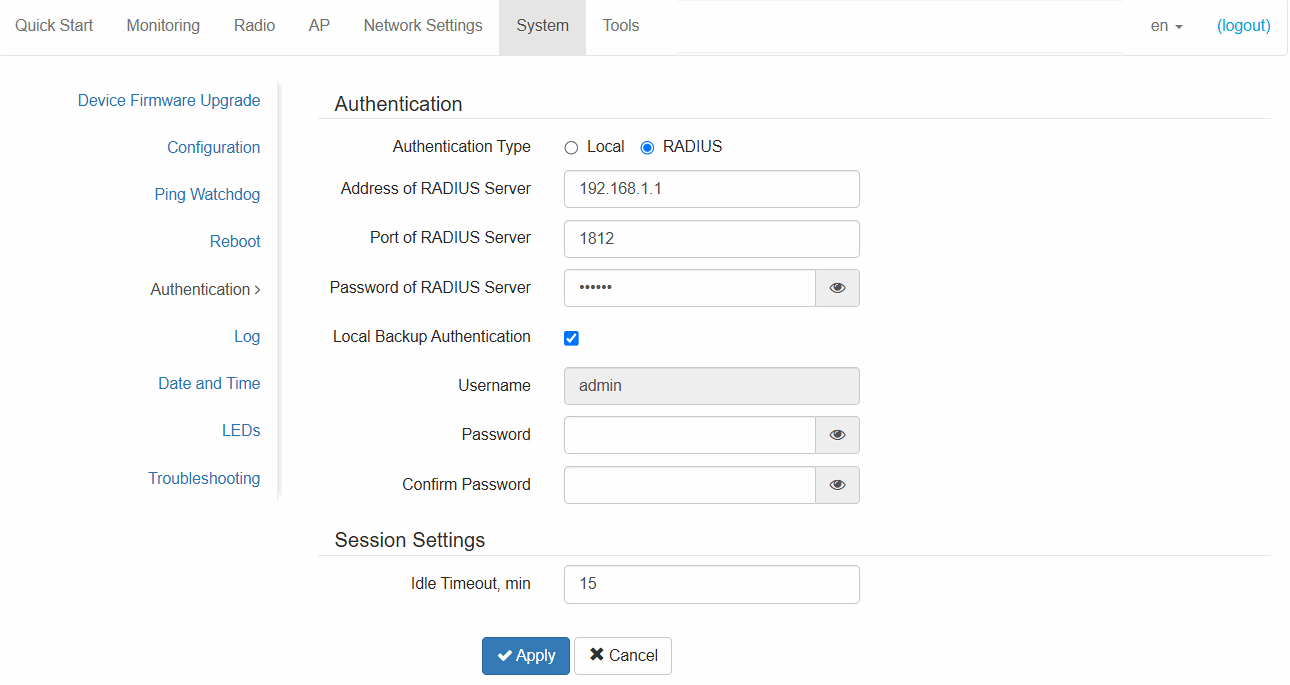
- Address of RADIUS server — IP Address of RADIUS server;
- Port of RADIUS server — RADIUS server port used for authentication and authorization;
- Password of RADIUS server — RADIUS server key used for authentication and authorization;
- Local Backup Authentication — when enabled, local account authentication is activated admin when there is no connection with RADIUS server;
- Username — login of the configured account;
- Password — entering a new password;
- Confirm Password — confirming the new password.
With the "Local Backup Authentication" option disabled, authorization occurs only via RADIUS server. If the RADIUS server is unavailable or data is incorrect, authorization will fail. |
For authentication via RADIUS server, accounts with appropriate roles are created only on the server. Accounts can be assigned the following roles: On the RADIUS server, the Cisco-AVPair = "shell:role=<role>" attribute is used to configure account roles (where <role> is either admin or viewer). |
Session Settings:
- Idle Timeout, min — user idle time in minutes after which the session is terminated automatically.
To apply a new configuration and save settings to non-volatile memory, click the "Apply" button. Click the "Cancel" button to discard the changes.
"Log" submenu
The "Log" submenu is designed to configure the output of various kinds of system messages in order to detect problem causes in the device operation.
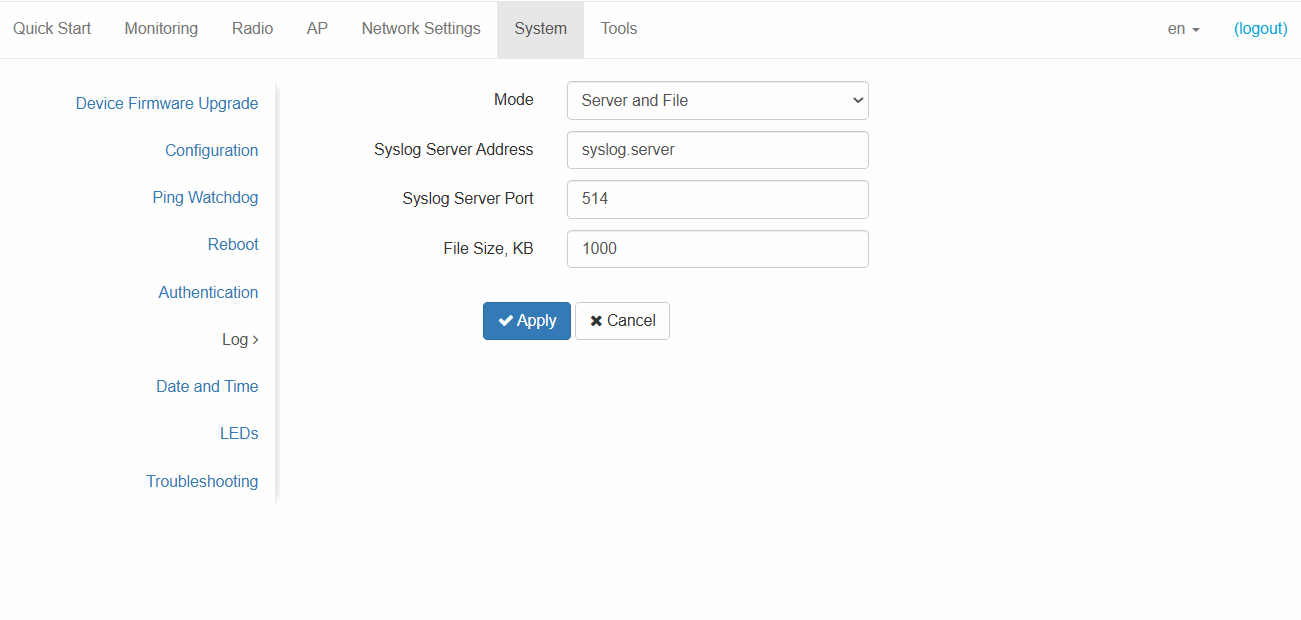
- Mode — Syslog agent operating mode:
- Local File — log information is stored in a local file and is available in the "Events" submenu;
- Server and File — log information is sent to a remote Syslog server and is saved to a local file.
- Syslog Server Address — IP address or domain name of the Syslog server;
- Syslog Server Port — port for incoming Syslog server messages (default: 514, acceptable values: from 1 to 65535);
- File Size, KB — maximum size of the log file (acceptable values: 1–1000 kB).
To apply a new configuration and save settings to non-volatile memory, click "Apply”. Click "Cancel" to discard the changes
"Date and Time" submenu
In the "Date and Time" submenu, it is possible to set the time manually or using the time synchronization protocol (NTP).
Manual
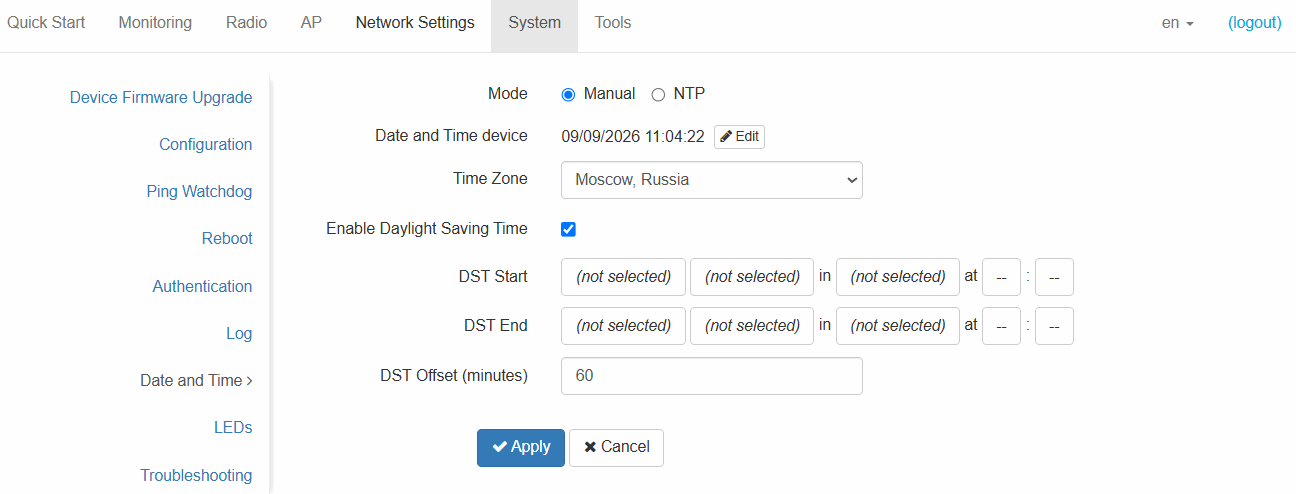
- Date and Time device — date and time on the device at the current moment. Click the "Edit" button to make corrections:
- Date, Time — set the current date and time or click the "Set current date and time" button to synchronize with the device;
- Time Zone — allows to set the time zone according to the nearest city for your region from the list;
- Enable daylight Saving Time — when selected, automatic daylight saving change will be performed automatically within the defined time period:
- DST Start — day and time, when daylight saving time starts;
- DST End — day and time, when daylight saving time ends;
- DST Offset (minutes) — time period in minutes, on which time offset is performing. The parameter can take a value from 0 to 720 minutes.
To apply a new configuration and save settings to non-volatile memory, click "Apply”. Click "Cancel" to discard the changes.
NTP Server
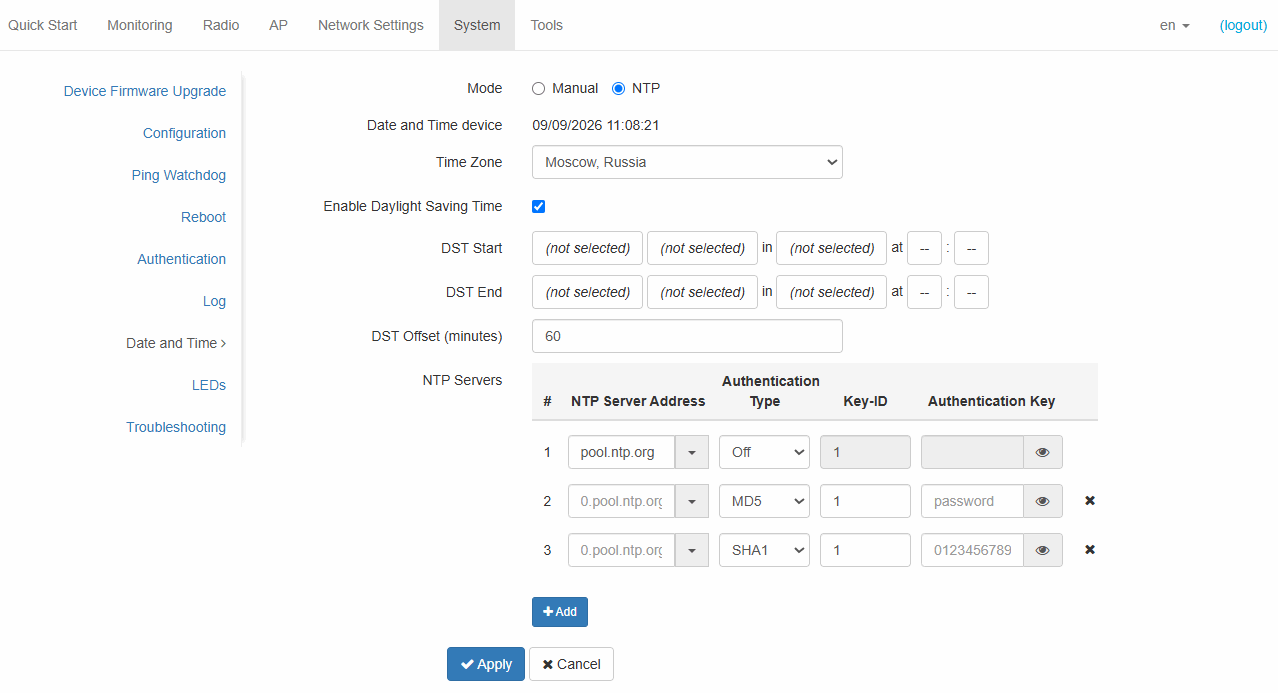
- Date and Time devices — current date and time on the device;
- Time Zone — sets the time zone according to the nearest city in your region from the given list;
- Enable Daylight Saving Time — when selected, automatic daylight saving change will be performed automatically within the defined time period:
- DST Start — day and time, when daylight saving time starts;
- DST End — day and time, when daylight saving time ends;
- DST Offset (minutes) — time period in minutes, on which time offset is performing. The parameter can take a value from 0 to 720 minutes.
- NTP Servers:
- NTP Server Address — IP address/domain name of the time synchronization server. An address can be specified or selected from the existing list;
- Authentication Type — selection of a hashing algorithm for authentication of NTP packets. Possible values: Off, MD5, SHA1;
- Key-ID — unique key number used for authentication during data exchange with NTP Server. Possible values: 1 to 65535;
- Authentication Key — secret key for authentication in text format.
To apply a new configuration and save settings to non-volatile memory, click the "Apply" button. Click the "Cancel" button to discard the changes.
"LEDs" submenu
In the "LEDs" submenu, LEDs on the device can be customized.
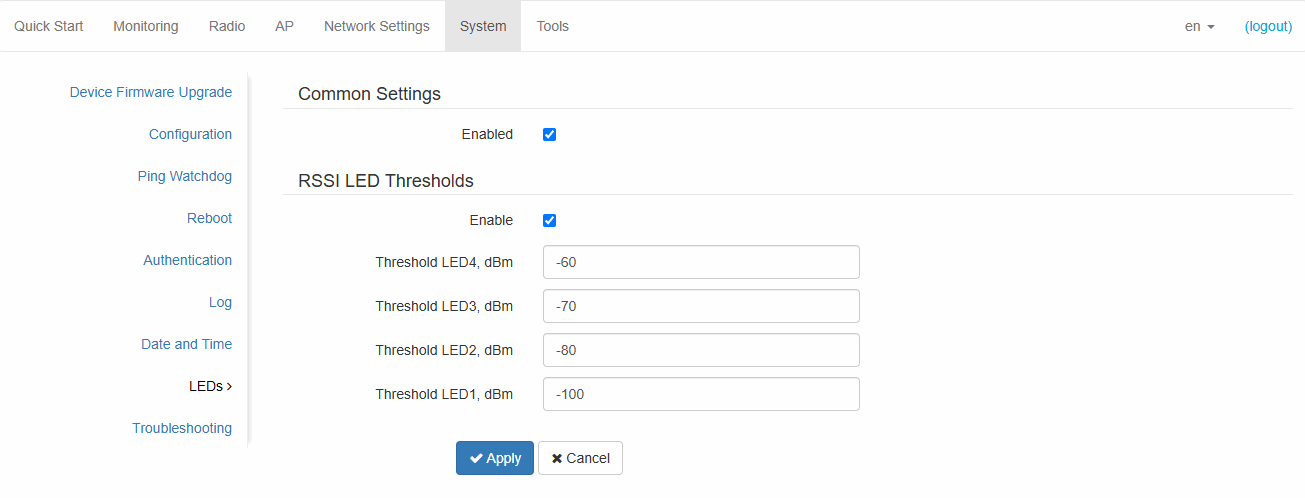
Common settings:
- Enabled — when checked, the indicators are enabled, otherwise they are disabled.
RSSI LED Threshold:
- Enable — when checked, the assignment of thresholds for each indicator is enabled, otherwise it is disabled;
- Threshold LED4, dBm — minimum signal level of a remote device (RSSI), at which LED4 turns on (by default: -60, acceptable values: -100–0);
- Threshold LED3, dBm — minimum signal level of a remote device (RSSI), at which LED3 turns on (by default: -70, acceptable values: -100–0);
- Threshold LED2, dBm — minimum signal level of a remote device (RSSI), at which LED2 turns on (by default: -80, acceptable values: -100–0);
- Threshold LED1, dBm — minimum signal level of a remote device (RSSI), at which LED1 turns on (by default: -100, acceptable values: -100–0).
To apply a new configuration and save settings to non-volatile memory, click "Apply”. Click "Cancel" to discard the changes.
"Troubleshooting" submenu
Troubleshooting File
To get WB-3P-PTP6_SN_troubleshooting.tar.gz archive from the device to a local computer, click "Download".
"Tools" menu
"Antenna Align" submenu
Alignment refers to adjusting the device antenna position in space to obtain the maximum signal.
To start alignment, click the "Start" button.
To stop alignment, click the "Stop" button.
Antenna Align:
- SSID — wireless network name;
- Channel — data channel;
- RSSI, dBm — received signal level, dBm;
- Remote RSSI, dBm — received signal level from the remote device, in dBm;
- Estimated RSSI, dBm — theoretical (expected) signal level value, dBm.
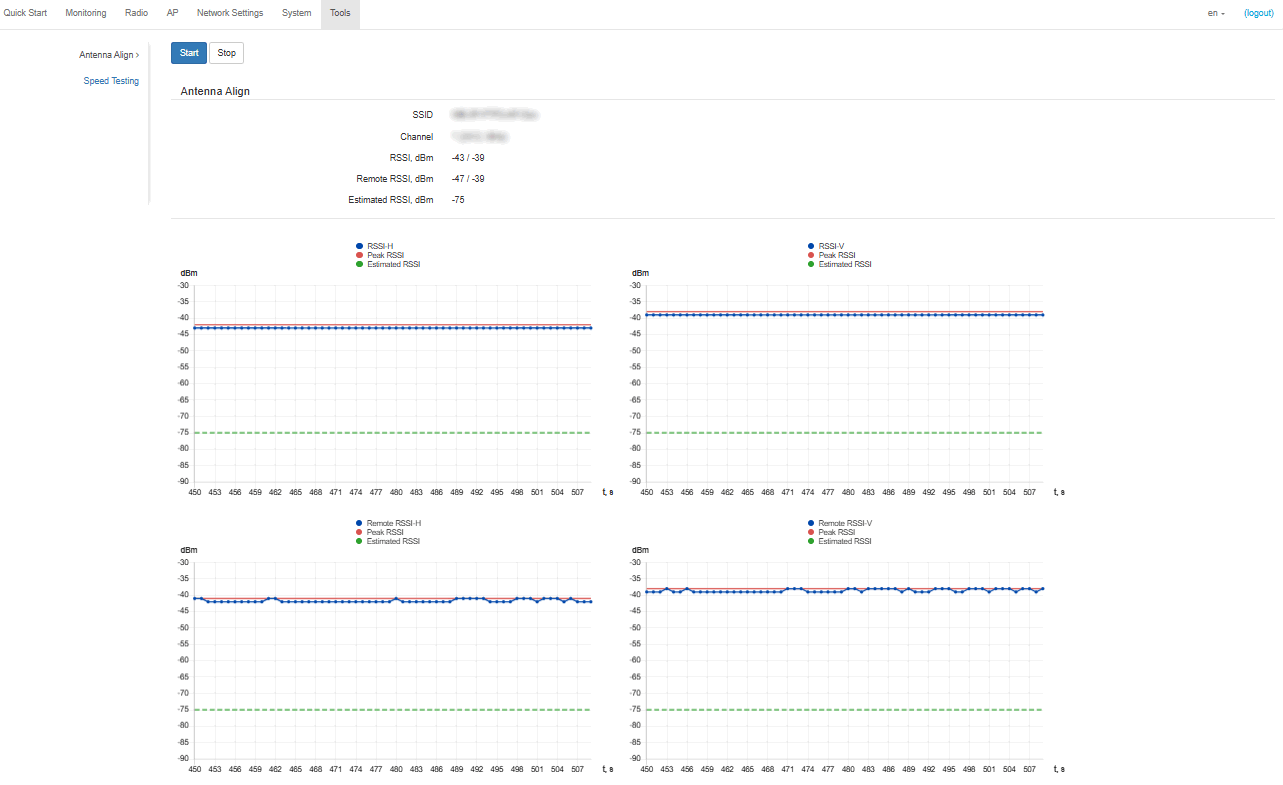
RSSI-H graph displays signal level changes on the first antenna in dBm over time in seconds.
RSSI-V graph displays signal level changes on the second antenna in dBm over time in seconds.
Remote RSSI-H graph displays signal level changes on the first antenna of the remote device in dBm over time in seconds.
Remote RSSI-V graph displays signal level changes on the second antenna of the remote device in dBm over time in seconds.
Peak RSSI — maximum signal level in dBm during the measurement period. Red line.
Estimated RSSI — theoretical (expected) signal level value, dBm. Dashed green line.
"Speed Testing" submenu
The "Speed Testing" submenu is used for link speed testing.
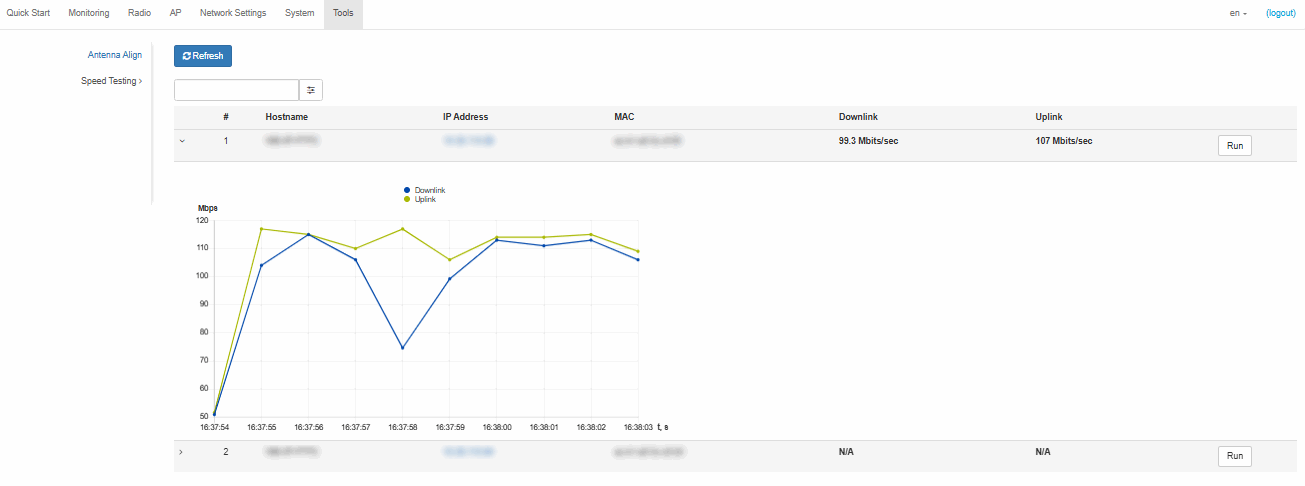
The test operates in bidirectional mode (Downlink+Uplink). First, the inbound data flow rate is measured (Downlink), then outgoing (Uplink).
The test is performed with TCP traffic and lasts 10 seconds for one direction. At any given time, a test can only be run to one remote device.
To start, press the "Run" button. Upon test completion, the result will be displayed in the corresponding field and on the graph.
By default, the test uses VLAN 7 and subnet 192.0.4.0/24. If the network already uses such a subnet and VLAN, it is required to change the test settings so that they do not overlap with the existing networks. This can be done via the CLI. The process is described in more detail in the Perftest utility section .
The following filters are available for searching connected devices: by all fields, by hostname, by IP Address, by MAC. To select a filter, click on |
Example of device setup
This section provides an example of initial device setup for establishing a wireless bridge.
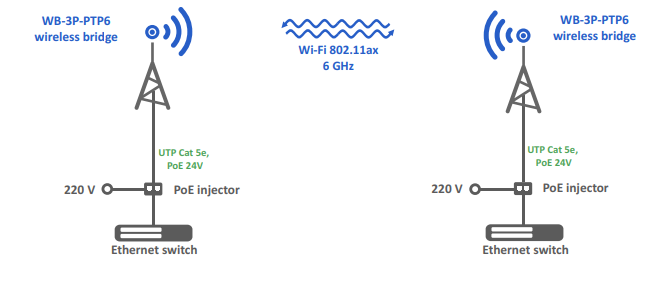
Figure 34 — WB-3P-PTP6 use case
In the browser address bar, enter the device IP address (by default 192.168.1.10, if the device has not received an address via DHCP). Upon successful connection to the device, a window will appear asking for login and password. Fill in the fields and click the "Log In" button. By default — login: admin, password: password. |
If this window does not appear, ensure the PC is on the same network as the device.
Configuring Access point (AP):
- By default WB-3P-PTP6 is configured to receive an address via DHCP. If the address was not obtained, connect to the device using the factory IP Address: 192.168.1.10, subnet mask: 255.255.255.0.
- The device firmware must be updated to the latest version as described in the Device Firmware Upgrade section.
- In the "Radio" menu, perform preliminary radio interface configuration. Select the data channel and specify the distance between devices in kilometers.
- Save the settings by clicking the "Apply" button.
- In the "AP" menu in the "SSID" field, specify the wireless network identifier to which the client will connect (STA).
- In the "Security Mode" field, select the security mode for network authentication and set the key if an encrypted network is used.
- Save the settings by clicking the "Apply" button.
Configuring the client (STA) to connect to the access point (AP):
- By default WB-3P-PTP6 is configured to receive an address via DHCP. If the address was not obtained, connect to the device using the factory IP Address: 192.168.1.10, subnet mask: 255.255.255.0.
- The device firmware must be updated to the latest version as described in the section Device Firmware Upgrade.
- If static or default settings are used to connect to the provider network, then in the "Network Settings" menu in the field "Protocol" you need to select a value "Static", fill in the fields "Static IP", "Network mask", "Gateway".
- In the "STA" menu in the "SSID" field, specify the wireless network identifier to connect to.
- In the "Security Mode" field, select the security mode for network authentication and set the key if an encrypted network is used.
- After pressing the "Apply" button, client (STA) will search for the specified SSID in the air and will attempt to connect to the access point upon detection (AP) with the specified parameters.
- Check that In the "Monitoring" menu in the "Wireless Peer" section an access point (AP) has appeared. Check the availability of the access point (AP) by entering the device's IP address into your browser's address bar.
If all the above items are completed successfully, the wireless connection between devices is configured.
Managing the device using the command line
To enter configuration mode, enter the command configure. To display the current settings of a specific configuration section, enter the command show-config. To get a hint about acceptable values for a device configuration parameter, press the key combination (in English keyboard layout) [Shift + ?]. To get a list of parameters available for editing in this configuration section, press the Tab key. To save the settings, enter the save command. To return to the previous configuration section, enter the exit command. To exit configuration mode, enter the end command. |
Configuration must begin with the client device to avoid losing connection to it. |
Connection to the device
By default WB-3P-PTP6 is configured to receive an address via DHCP. If the address was not obtained, connect to the device using the factory IP Address.
The factory IP address for WB-3P-PTP6: 192.168.1.10, subnet mask: 255.255.255.0. |
Connection to the device is performed using SSH:
ssh admin@<IP address of the device>, then enter password |
Network parameters configuration
WB-3P-PTP6(root):/# configure Adding a static route WB-3P-PTP6(config):/interface/br0/common# exit |
WB-3P-PTP6(root):/# configure |
Network parameters configuration using the set-management-vlan-mode utility
Obtaining network settings via DHCP WB-3P-PTP6(root):/# set-management-vlan-mode off protocol dhcp Static settings WB-3P-PTP6(root):/# set-management-vlan-mode off protocol static-ip ip-addr X.X.X.X netmask Y.Y.Y.Y gateway Z.Z.Z.Z (where X.X.X.X — static IP address, Y.Y.Y.Y — subnet mask, Z.Z.Z.Z — gateway) |
Obtaining network settings via DHCP WB-3P-PTP6(root):/# set-management-vlan-mode terminating vlan-id X protocol dhcp (where X — VLAN ID, used for device access. Possible values: 1–4094) Static settings WB-3P-PTP6(root):/# set-management-vlan-mode terminating vlan-id X protocol static-ip ip-addr X.X.X.X netmask Y.Y.Y.Y gateway Z.Z.Z.Z (where X — VLAN ID, used for device access; possible values: 1–4094; X.X.X.X — static IP address; Y.Y.Y.Y — subnet mask; Z.Z.Z.Z — gateway) |
Obtaining network settings via DHCP WB-3P-PTP6(root):/# set-management-vlan-mode forwarding vlan-id X protocol dhcp (where X — VLAN ID, used for device access. Possible values: 1–4094) Static settings WB-3P-PTP6(root):/# set-management-vlan-mode forwarding vlan-id X protocol static-ip ip-addr X.X.X.X netmask Y.Y.Y.Y gateway Z.Z.Z.Z (where X — VLAN ID, used for device access; possible values: 1–4094; X.X.X.X — static IP address; Y.Y.Y.Y — subnet mask; Z.Z.Z.Z — gateway) |
WB-3P-PTP6(root):/# save (saving settings) |
Configuring 802.1p priority for Management VLAN
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
Remote management configuration
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
IPv6 network parameters configuration
By default access to the device via the protocol IPv6 is disabled on the device. |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
 Radio settings
To change the radio channel, channel bandwidth, or power, use the following commands:
WB-3P-PTP6(root):/# configure |
Lists of available channels In Radio 6 GHz for locations "Russia (RU)"/"Unlimited (ALL)" the following channels are available for selection:
In Radio 6 GHz for locations "Russia (RU)"/"Unlimited (ALL)" the following channels are available for selection when fixed center frequency is enabled:
|
Advanced Radio settings
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# country X (parameter X can take a value: RU, ALL) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# work-mode X (where X — radio interface operating mode in accordance with the IEEE 802.11 standard. Possible values: ax) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# control-sideband lower (parameter can take the value: lower, upper. By default: lower) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# center-frequency true (enabling fixed center frequency. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# sgi true (enabling the use of short guard interval for data transmission — 400 ns, instead 800 ns. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# use-limit-channels true (enabling the use of a limited channel list. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# sensitivity-threshold-mode X (where X — receiver sensitivity threshold mode. Takes values: dynamic — dynamic sensitivity adjustment; fixed — fixed receiver sensitivity threshold) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# stbc true (enabling the Space-Time Block Coding (STBC) method, Designed to improve data transmission reliability. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# aggregation true (enabling aggregation on Radio — support for AMPDU/AMSDU. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# short-preamble true (enabling the use of short packet preamble. To disable, enter false) |
| WB-3P-PTP6(config):/interface/wlan0/wlan/radio# fixed-rate X (where X — modulation name in uppercase letters without spaces, for example, HE-NSS2-MCS10. Allowed values are determined by the radio interface operating mode and channel bandwidth) WB-3P-PTP6(config):/interface/wlan0/wlan/radio# enable-fixed-rate true (enabling fixed channel data transfer rate. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# maximal-rate-tx |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# maximal-rate-rx |
| WB-3P-PTP6(config):/interface/wlan0/wlan/radio# minimal-rate-rx WB-3P-PTP6(config):/interface/wlan0/wlan/radio/minimal-rate-rx# he X (where X — modulation name in uppercase letters without spaces, for example, NSS1-MCS0. This parameter is used when connecting devices in IEEE 802.11ax mode) WB-3P-PTP6(config):/interface/wlan0/wlan/radio/minimal-rate-rx# enable true (enabling minimum channel data receive rate. To disable, enter false. Access is only in ap-ptp and sta device modes) WB-3P-PTP6(config):/interface/wlan0/wlan/radio/qos# save (saving settings) |
The maximal and minimal receive rate parameters are used to specify the maximal and minimal transmit rate to a remote device. Therefore, when configuring maximal and/or minimal receive rate, for example, on a client (STA), there is no need to configure maximal and/or minimal transmit rate on an access point (AP). |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# auto-distance true (enabling automatic distance calculation between devices. To disable, enter false) |
During the use of the antenna-align utility, automatic power control function is disabled. |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# auto-tx-power |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio/tdd# enable true (enabling Time Division Duplex (TDD) technology, which synchronizes data transmission in both directions within a time frame. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# dtim-interval X (where X — DTIM interval. Possible values: 1–255. By default: 64) |
WB-3P-PTP6(config):/interface/wlan0/wlan/radio# qos |
The configuration method edca-sta is similar to the configuration method edca-ap.
Configuring parameters for queues be, vi, vo is similar to configuring parameters for the queue bk.
WB-3P-PTP6(config):/interface/wlan0/wlan/radio/antenna-configuration# type custom (antenna type selection. The parameter can take the values: internal — integrated antenna; custom — custom antenna, offset KU45/50CM — offset parabolic antenna. By default: internal) |
Configuring DHCP option 82
Modes of operation DHCP snooping:
- ignore – option 82 processing is disabled. Default value;
- replace – device inserts or replaces the value of option 82;
- remove – device removes the value of option 82.
WB-3P-PTP6(root):/# configure |
If the radio interface is configured with a policy for processing the option 82 replace, the following parameters become available for configuration:
WB-3P-PTP6(config):/interface/wlan0/common/dhcp-snooping# dhcp-option-82-CID-format custom (where custom — replacing the CID content to the value specified in the dhcp-option-82-customCID parameter. The parameter can take the values: APMAC-SSID — replacing the CID content on <device MAC address>-<name SSID>. SSID — replacing the CID content to device SSID name. By default: APMAC-SSID) |
Configuring wireless network
Table 6 — Commands for configuring device mode
| Device | Operating mode | Command for configuring the mode |
| Access Point (AP) | Access Point PTP | mode ap-ptp |
| Access Point (AP) | Access Point PMP | mode ap-pmp |
| Client (STA) / Station | Station / Client | mode sta |
Table 7 — Commands for configuring security mode
| Mode security | Command for configuring security mode |
| WPA3 | mode WPA3 |
| OWE | mode OWE |
| WPA3-Enterprise | mode WPA3_1X |
Network settings for access point (AP)
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
Advanced settings for access point (AP)
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# vlan-id X (where X — VLAN-ID number) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# vlan-trunk true (enabling VLAN Trunk. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# general-vlan-mode true (enabling General VLAN on SSID. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# customer-vlans |
In case the access point is configured with Enterprise authorization and C-VLAN is specified for the client on RADIUS server, then this C-VLAN will be used for communication with this client, that means C-VLAN, configured on the access point, will be ignored. The VLAN value is transmitted to Tunnel-Private-Group-Id RADIUS attribute. |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# vlan-priority X (where X — 802.1p priority value assigned to packets that are VLAN tagged using the VLAN-ID or General VLAN functionality. Possible values: 0–7, auto. Default value: auto) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# priority-by-dscp false (priority analysis from the CoS (Class of Service) field of tagged packets. Default value: true. In this case the priority from the field is analyzed DSCP header IP-packet) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# hidden true (enabling hidden SSID. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# check-signal-enable true (enabling Minimal Signal. To disable, enter false) |
Configuring the shaper in the direction from the client (STA) to the access point (AP): Configuring the shaper in the direction from the access point (AP) to the client (STA): |
Configuring the shaper in the direction from the client (STA) to the access point (AP): Configuring the shaper in the direction from the access point (AP) to the client (STA): |
Configuring the shaper in the direction from the client (STA) to the access point (AP): Configuring the shaper in the direction from the access point (AP) to the client (STA): |
Configuring the shaper in the direction from the access point (AP) to the client (STA): WB-3P-PTP6(config):/interface/wlan0/wlan/ap# shaper-mcast-tx |
Configuring the shaper in the direction from the access point (AP) to the client (STA): |
Configuring the shaper in the direction from the client (STA) to the access point (AP): |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# sta-limit X (where X — maximum allowed number of client devices that can connect to the wireless network. Available only in ap-pmp device mode) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# station-isolation true (enabling traffic isolation between connected devices. To disable, enter false. Available only in ap-pmp device mode) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# acl |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# acl |
| WB-3P-PTP6(config):/interface/wlan0/wlan/ap# vlan-mapping WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping# rule WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping/rule# add name1 (where name1 — mapping rule name. To remove a rule, use the command del) WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping/rule# name1 WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping/rule/name1# eth-vlan-id X (where X — VLAN ID in Ethernet) WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping/rule/name1# eth-priority X (where X — 802.1p priority when transmitting to Ethernet. Possible values: 0–7, auto. If the priority is auto or not defined in this option — the original will be used) WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping/rule/name1# wlan-vlan-id X (where X — VLAN ID in WLAN) WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping/rule/name1# wlan-priority X (where X — 802.1p priority when transmitting in WLAN. Possible values: 0–7, auto. If the priority is auto or not defined in this option — the original will be used) WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping/rule/name1# exit WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping/rule# exit WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping# enable true (enabling vlan-mapping. To disable, enter false) WB-3P-PTP6(config):/interface/wlan0/wlan/ap/vlan-mapping# save (saving settings) |
There is a predefined rule in the vlan-mapping configuration — default-rule. It is used to change the 802.1p priority and WMM queue of all packets whose VLAN number does not match the user-defined rules. |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# vlan-mapping |
Configuring a rule for tagged traffic WB-3P-PTP6(config):/interface/wlan0/wlan/ap# mac-priority Configuring a rule for untagged traffic WB-3P-PTP6(config):/interface/wlan0/wlan/ap# mac-priority |
For packets going from the access point (AP) to the client (STA), src-mac parameter — source MAC address, dst-mac — MAC address of Client (STA). For packets going from the client (STA) to the access point (AP), src-mac parameter — MAC address of client (STA), dst-mac — Recipient MAC address. |
Configuring a rule for tagged traffic WB-3P-PTP6(config):/interface/wlan0/wlan/ap# ip-priority Configuring a rule for untagged traffic WB-3P-PTP6(config):/interface/wlan0/wlan/ap# ip-priority |
If a packet matches more than one of the Vlan-Mapping, MAC-Priority, and IP-Priority rule types at the same time, the 802.1P priority assignment decision will be made based on the Priority-Order of the rule type, where 1 is the minimum priority and 100 is the maximum priority. For example, if a packet matches a Vlan-Mapping rule with Priority-Order of 1, a MAC-priority with Priority-Order of 25, and an IP-priority with Priority-Order of 80, then this packet will be assigned a priority according to the IP-Priority rule, since it has the highest Priority-Order. |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# priority-order |
Network settings for client (STA)
In sta device mode, multiple access point (AP) connection profiles can be configured (up to 8 profiles). |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
Advanced settings for client (STA)
WB-3P-PTP6(config):/interface/wlan0/wlan/sta# vlan-id X (where X — VLAN-ID number) |
WB-3P-PTP6(config):/interface/wlan0/wlan/sta# vlan-trunk true (enabling VLAN Trunk. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/sta# general-vlan-mode true (enabling General VLAN on SSID. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/sta# mvr-enable true (enabling MVR. To disable, enter false) |
WB-3P-PTP6(config):/interface/wlan0/wlan/ap# vlan-priority X (where X — 802.1p priority value assigned to packets that are VLAN tagged using the VLAN-ID or General VLAN functionality. Possible values: 0–7, auto. Default value: auto) |
WB-3P-PTP6(config):/interface/wlan0/wlan/sta# priority-by-dscp false (priority analysis from the field CoS (Class of Service) tagged packets. Default value: true. In this case, the priority from the DSCP field of the IP packet header is analyzed. |
Configuring the shaper in the direction from the client (STA) to the access point (AP): Configuring the shaper in the direction from the access point (AP) to the client (STA): |
Configuring the shaper in the direction from the access point (AP) to the client (STA): Configuring the shaper in the direction from the client (STA) to the access point (AP): |
Configuring the shaper in the direction from the access point (AP) to the client (STA): |
Configuring the shaper in the direction from the client (STA) to the access point (AP): |
Configuring the shaper in the direction from the access point (AP) to the client (STA): |
The remote device is configured similarly.
WB-3P-PTP6(config):/interface# eth0 |
| WB-3P-PTP6(config):/interface/wlan0/wlan/sta# vlan-mapping WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping# rule WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping/rule# add name1 (where name1 — mapping rule name. To remove a rule, use the command del) WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping/rule# name1 WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping/rule/name1# eth-vlan-id X (where X — VLAN ID in Ethernet) WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping/rule/name1# eth-priority X (where X — 802.1p priority when transmitting to Ethernet. Possible values: 0–7, auto. If the priority is auto or not defined in this option — the original will be used) WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping/rule/name1# wlan-vlan-id X (where X — VLAN ID in WLAN) WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping/rule/name1# wlan-priority X (where X — 802.1p priority when transmitting in WLAN. Possible values: 0–7, auto. If the priority is auto or not defined in this option — the original will be used) WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping/rule/name1# exit WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping/rule# exit WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping# enable true (enabling vlan-mapping. To disable, enter false) WB-3P-PTP6(config):/interface/wlan0/wlan/sta/vlan-mapping# save (saving settings) |
There is a predefined rule in the vlan-mapping configuration — default-rule. It is used to change the 802.1p priority and WMM queue of all packets whose VLAN number does not match the user-defined rules. |
WB-3P-PTP6(config):/interface/wlan0/wlan/sta# vlan-mapping |
Configuring a rule for tagged traffic WB-3P-PTP6(config):/interface/wlan0/wlan/sta# mac-priority Configuring a rule for untagged traffic WB-3P-PTP6(config):/interface/wlan0/wlan/sta# mac-priority |
For packets going from access point (AP) to client (STA), src-mac is the MAC address of the access point (AP), dst-mac is the destination MAC address. For packets going from client (STA) to access point (AP), src-mac is the source MAC address, dst-mac is the MAC address of the access point (AP). |
Configuring a rule for tagged traffic WB-3P-PTP6(config):/interface/wlan0/wlan/sta# ip-priority Configuring a rule for untagged traffic WB-3P-PTP6(config):/interface/wlan0/wlan/sta# ip-priority |
If a packet matches more than one of the Vlan-Mapping, MAC-Priority, and IP-Priority rule types at the same time, the 802.1P priority assignment decision will be made based on the Priority-Order of the rule type, where 1 is the minimum priority and 100 is the maximum priority. For example, if a packet matches a Vlan-Mapping rule with Priority-Order of 1, a MAC-priority with Priority-Order of 25, and an IP-priority with Priority-Order of 80, then this packet will be assigned a priority according to the IP-Priority rule, since it has the highest Priority-Order. |
WB-3P-PTP6(config):/interface/wlan0/wlan/sta# priority-order |
LoopBack Detection configuration
This functionality can be configured only in the sta device mode. |
If a loop is detected on downstream equipment, the device blocks the Ethernet interface for the time specified in the configuration. |
If the functionality is enabled, the client (STA) checks for loops on downstream equipment and, if any are detected, blocks the Ethernet interface for the time specified in the device configuration. The presence of loops is checked by sending special packets to the LAN network with the destination address cf:00:00:00:00:00.
WB-3P-PTP6(root):/# configure |
BPDU filter configuration
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
MAC address learning limiting
WB-3P-PTP6(root):/# configure |
Changing the MTU size on interfaces
The remote device is configured in a similar way.
WB-3P-PTP6(root):/# configure |
The MTU value on the br0, nas0 interfaces is set automatically, in accordance with the value on eth0. The MTU value on the wlan0 interface is fixed and equals 2000. |
System settings
Upgrading the device firmware
| WB-3P-PTP6(root):/# firmware upload tftp <IP Address of TFTP server><Firmware file name> (example: firmware upload tftp 192.168.1.15 WB-3P-PTP6-2.6.1_build_X.tar.gz) WB-3P-PTP6(root):/# firmware upgrade |
| WB-3P-PTP6(root):/# firmware upload http <URL to download the firmware file> (example: firmware upload https://eltex.ru/storage/upload_center/files/XX/WB-3P-PTP6-2.6.1_build_X.tar.gz) WB-3P-PTP6(root):/# firmware upgrade |
| WB-3P-PTP6(root):/# firmware switch |
Device configuration management
| WB-3P-PTP6(root):/# manage-config reset-to-default |
| WB-3P-PTP6(root):/# manage-config reset-to-default-without-management |
| WB-3P-PTP6(root):/# manage-config download tftp <IP Address of TFTP server> (example: manage-config download tftp 192.168.1.15) |
| scp <User>@<IP-device address>:/etc/config/config.json config.json (example: scp admin@192.168.1.15:/etc/config/config.json config.json. This command is executed on the server/PC) |
WB-3P-PTP6(root):/# manage-config upload tftp <IP Address of TFTP server> <configuration file name> (example: manage-config upload tftp 192.168.1.15 config.json) |
Ping watchdog
The availability control feature (ping watchdog) allows one to detect a loss of network connectivity and reboot the device or its interfaces without user intervention. When an interface restarts, the DHCP client on the current WAN interface also restarts.
WB-3P-PTP6(config):/ping-watchdog# enable true (enabling ping watchdog. By default: false) |
Device reboot
| WB-3P-PTP6(root):/# reboot |
| WB-3P-PTP6(root):/# reboot delay X (where X — time in seconds after which the scheduled device reboot will occur. Possible values: 0–86400) |
| WB-3P-PTP6(root):/# reboot at hh:mm:ss (where hh:mm:ss — time at which the scheduled device reboot will occur. Possible values: hh:mm, hh:mm:ss) |
| WB-3P-PTP6(root):/# reboot cancel |
Configuring authentication mode
The device has a factory account admin with password password. This account cannot be deleted. The password can be changed using the commands below.
WB-3P-PTP6(root):/# configure |
Additional users can be created for local authentication and for authentication via RADIUS.
New users must be assigned one of two roles: |
Additional users are created with the following commands:
WB-3P-PTP6(root):/# configure |
To authenticate via RADIUS server, access parameters should be configured:
WB-3P-PTP6(root):/# configure |
With radius-local-fallback disabled, authorization occurs only via RADIUS server. If the server is unavailable or the credentials are incorrect, authorization will fail. With radius-local-fallback enabled, if there is no connection to RADIUS server, authorization can be performed using the local admin account. Authorization through other local accounts will fail. |
For authentication via RADIUS server: accounts with appropriate roles are created only on it. |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
Configuring DHCP-snooping
WB-3P-PTP6(root):/# configure |
By default, only eth0 is considered a trusted port. |
Configuring date and time
WB-3P-PTP6(root):/# configure WB-3P-PTP6(config):/date-time/common# save (saving settings) |
For the MD5 algorithm, the key length must be from 1 to 16 characters; the # character is not allowed. The SHA1 algorithm requires exactly 40 characters in hexadecimal format (digits 0–9 and letters a–f). key-id, key-type, and key-value are optional parameters. They are used only when connecting to an NTP server with authentication. |
Advanced system settings
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
WB-3P-PTP6(root):/# configure |
Monitoring
Wireless Peer/Wireless Clients
Device mode ap-ptp
Displaying useful information about the wireless peer status from the access point (AP):
WB-3P-PTP6(root):/# monitoring wireless-peer
|
Displaying brief information about the wireless peer status in horizontal view from the access point (AP):
WB-3P-PTP6(root):/# monitoring wireless-peer brief
|
Displaying full information about the wireless peer status from the access point (AP):
WB-3P-PTP6(root):/# monitoring wireless-peer detailed
|
Device mode ap-pmp
Displaying useful information about the wireless clients (STA) from the access point (AP):
WB-3P-PTP6(root):/# monitoring clients
|
Displaying useful information about a wireless client (STA) from the access point side (AP):
WB-3P-PTP6(root):/# monitoring clients station ec:b1:e0:2d:a1:00
|
Displaying brief information about wireless clients (STA) in horizontal view from the access point side (AP):
WB-3P-PTP6(root):/# monitoring clients brief
|
Displaying brief information about a wireless client (STA) in horizontal view from the access point side (AP):
WB-3P-PTP6(root):/# monitoring clients station ec:b1:e0:2d:a1:00 brief
|
Displaying full information about wireless clients (STA) from the access point side (AP):
WB-3P-PTP6(root):/# monitoring clients detailed
|
Displaying full information about a wireless client (STA) from the access point side (AP):
WB-3P-PTP6(root):/# monitoring clients station ec:b1:e0:2d:a1:00 detailed
|
Device mode sta
Displaying information about the wireless peer status from the client (STA):
WB-3P-PTP6(root):/# monitoring wireless-peer
|
Displaying brief information about the wireless peer status in horizontal view from the client (STA):
WB-3P-PTP6(root):/# monitoring wireless-peer brief
|
Displaying full information about the wireless peer status from the client (STA):
WB-3P-PTP6(root):/# monitoring wireless-peer detailed
|
Device information
WB-3P-PTP6(root):/# monitoring information
|
Network information
WB-3P-PTP6(root):/# monitoring wan-status
WB-3P-PTP6(root):/# monitoring ethernet
WB-3P-PTP6(root):/# monitoring arp
WB-3P-PTP6(root):/# monitoring route
WB-3P-PTP6(root):/# monitoring lldp
|
Wireless interfaces
WB-3P-PTP6(root):/# monitoring radio-interface
|
Event logs
WB-3P-PTP6(root):/# monitoring events
|
Environment scan
While scanning the environment, the device radio interface will be disabled, which will make it impossible to transfer data to client devices during scanning. |
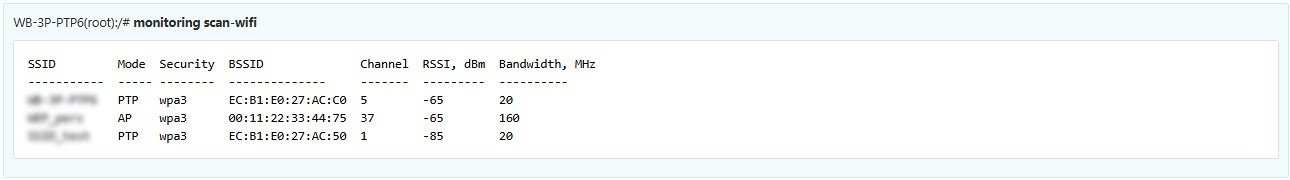
Spectrum analyzer
The spectrum analyzer provides information on channel congestion. The analysis time for all radio channels in the range is approximately 1 minute.
While the spectrum analyzer is running, client devices disconnect. The client devices will only reconnect when the spectrum analyzer has finished its work. |
As a result of the spectrum analyzer operation, information about the load of each channel (in percent) will be displayed on the console:
WB-3P-PTP6(root):/# monitoring spectrum-analyzer
|
Obtaining troubleshooting information
WB-3P-PTP6(root):/# get-troubleshooting-file |
After executing the command, the troubleshooting.tar.gz archive will be created, сontaining troubleshooting data and device status information.
Get the troubleshooting.tar.gz archive from the device to a server or PC using the TFTP protocol:
This protocol is unavailable to created users; available only to admin. |
WB-3P-PTP6(root):/# tftp upload <IP Address TFTP-of the server>troubleshooting.tar.gz |
Get the troubleshooting.tar.gz archive from the device to a server or PC using the SCP protocol:
This protocol is unavailable to created users; available only to admin. |
scp <User>@<IP-device address>:troubleshooting.tar.gztroubleshooting.tar.gz (example: scp admin@192.168.1.15:troubleshooting.tar.gztroubleshooting.tar.gz. This command is executed on the server/PC) |
Auxiliary utilities
Perftest utility 
The perftest utility performs a built-in radio link speed test.
WB-3P-PTP6(root):/# configure |
The perftest utility can be run with the following commands:
Perf-test station <MAC remote device> downlink — initiates speed testing to the remote device (Downlink) |
Manage-remote utility
The manage-remote utility allows running commands from access point (AP) on client (STA).
These commands can be executed when there is no access to the client (STA) via IP address. |
Rebooting
For device mode ap-ptp:
| WB-3P-PTP6(root):/# manage-remote reboot |
For device mode ap-pmp:
| WB-3P-PTP6(root):/# manage-remote reboot station XX:XX:XX:XX:XX:XX (where XX:XX:XX:XX:XX:XX — MAC address of the device to be rebooted) |
Scan environment
For device mode ap-ptp:
| WB-3P-PTP6(root):/# manage-remote scan-wifi |
For device mode ap-pmp:
| WB-3P-PTP6(root):/# manage-remote scan-wifi station XX:XX:XX:XX:XX:XX (where XX:XX:XX:XX:XX:XX — MAC address of the device on which air scanning will be performed) |
Spectrum Analyzer
For device mode ap-ptp:
| WB-3P-PTP6(root):/# manage-remote spectrum-analyzer |
For device mode ap-pmp:
| WB-3P-PTP6(root):/# manage-remote spectrum-analyzer station XX:XX:XX:XX:XX:XX (where XX:XX:XX:XX:XX:XX — MAC address of the device on which spectrum analysis will be performed) |
Obtaining troubleshooting information
For device mode ap-ptp:
| WB-3P-PTP6(root):/# manage-remote upload-troubleshooting WB-3P-PTP6(root):/# manage-remote upload-troubleshooting-checksum |
For device mode ap-pmp:
WB-3P-PTP6(root):/# manage-remote upload-troubleshooting station XX:XX:XX:XX:XX:XX (where XX:XX:XX:XX:XX:XX — MAC address of the device from which troubleshooting information will be obtained) |
The upload-troubleshooting-checksum command verifies the integrity of the received data. It is used for more reliable data transfer but may require more time. |
A specified channel on which the spectrum scan will be performed /tmp/troubleshooting/ with received data, troubleshooting_remote.tar.gz and troubleshooting_remote_checksum.tar.gz respectively. After the commands are executed, archives containing the collected data — troubleshooting_remote.tar.gz and troubleshooting_remote_checksum.tar.gz, respectively — will be created in the /tmp/troubleshooting/ directory. |
Uploading files from the device:
These commands are unavailable to created users; available only to admin. |
WB-3P-PTP6(root):/# tftp upload <IP address of TFTP server> /tmp/troubleshooting/troubleshooting_remote.tar.gz |
Scp <User>@<IP-device address>: /tmp/troubleshooting/troubleshooting_remote.tar.gztroubleshooting_remote.tar.gz (example: scp admin@192.168.1.15: /tmp/troubleshooting/troubleshooting_remote.tar.gztroubleshooting_remote.tar.gz. This command is executed on the server/PC) |
Traceroute utility
The utility shows the nodes (routers) a packet passes through and the time it takes to process the packet at each node.
This utility is unavailable to created users; available only to admin. |
WB-3P-PTP6(root):/# traceroute <test host> |
Tcpdump utility
The tcpdump utility allows capturing packets on a specified interface.
This utility is unavailable to created users; available only to admin. |
Traffic capture from the active interface
Capturing Ethernet interface packets.
WB-3P-PTP6(root):/# tcpdump interface eth0 |
Capturing Ethernet interface packets and saving them to a file.
WB-3P-PTP6(root):/# tcpdump interface eth0 file <filename> |
Air Sniffer
It is necessary to enable a special interface on the device's operating channel that captures packets from the air.
WB-3P-PTP6(root):/# configure |
Capturing air packets on radio0-interface.
WB-3P-PTP6(root):/# tcpdump interface radio0 |
Capturing air packets on radio0-interface with saving to file.
WB-3P-PTP6(root):/# tcpdump interface radio0 file <filename> |
Uploading the file from device to server
This command is executed on the server/PC.
| scp <User>@<IP-device address>:tcpdump.pcap tcpdump.pcap (example: scp admin@192.168.1.15:tcpdump.pcap tcpdump.pcap) |
Iperf/iperf3 utility
This utility is used to initiate a traffic stream from one device to another. The sending side is referred to as the client, and the receiving side as the server.
iperf
Example of initiating a traffic stream from device to server:
WB-3P-PTP6(root):/# iperf server |
WB-3P-PTP6(root):/# iperf client X.X.X.X (where X.X.X.X — IP Address of the server) |
iperf3
Example of launching a traffic stream from device to server:
WB-3P-PTP6(root):/# iperf3 server |
WB-3P-PTP6(root):/# iperf3 client X.X.X.X (where X.X.X.X — IP Address of the server) |
 Antenna Align
Alignment refers to adjusting the device antenna position in space to obtain the maximum signal.
WB-3P-PTP6(root):/# antenna-align
|
List of changes
| Document Version | Release Date | List of changes |
|---|---|---|
| Version 1.6 | 08.2026 | Synchronization with firmware version 2.6.1 |
| Version 1.5 | 06.2026 | Synchronization with firmware version 2.6.0 Added: 10.12.9 "Troubleshooting" submenu 12.11.8 Obtaining troubleshooting information Modified: 10.7.7 "Radio Information" submenu 10.8.1 "Radio" submenu 10.9 "AP" menu 10.10 "STA" menu 10.12.7.2 NTP Server 10.13.1 "Antenna Align" submenu 10.13.2 "Speed Testing" submenu 12.3.1 Advanced Radio settings 12.5.2 Advanced settings for access point (AP) 12.5.4 Advanced settings for client (STA) 12.10.7 Configuring date and time 12.11 Monitoring 13.2.4 Obtaining troubleshooting information 13.5 Iperf/iperf3 utility 13.6 Antenna Align |
| Version 1.4 | 03.2026 | Synchronization with firmware version 2.5.1 Added: 13.2.4 Obtaining troubleshooting information Modified: 10.6 "Quick Start" menu 10.7.7 "Radio Information" submenu 10.8 "Radio" menu 10.9 "AP" menu 10.10 "STA" menu 10.12.5 "Authentication" submenu 12.2.2 Configuring 802.1p priority for Management VLAN 12.3.1 Advanced Radio settings 12.10.5 Configuring authentication mode 12.11 Monitoring |
| Version 1.3 | 12.2025 | Synchronization with firmware version 2.4.4 Modified: 12.5.2 Advanced settings for access point (AP) 12.5.4 Advanced settings for client (STA) |
| Version 1.2 | 10.2025 | Synchronization with firmware version 2.4.1 Added: 10.4 Test mode 10.12.3 "Ping Watchdog" submenu 10.12.5 "Authentication" submenu 12.10.3 Ping watchdog 12.10.5 Configuring authentication mode 13.4.1 Traffic capture from the active interface 13.4.3 Uploading the file from the device to the server Modified: 12.3.1 Advanced Radio settings |
| Version 1.1 | 07.2025 | Synchronization with firmware version 2.3.1 Added: 10.11.7 "LEDs" submenu 10.12.2 "Speed Testing" submenu 12.7 BPDU filter configuration 12.8 MAC address learning limiting Modified: 10.6.1 "Wireless Peer/Wireless Clients" submenu 10.6.3 "Scan Environment" submenu 10.8.1 "Access Point" submenu 10.9.1 "Station / Client" submenu 12.2.3 Remote management configuration 12.3 Radio Settings 12.3.1 Advanced Radio settings 12.5 Configuring the wireless network 12.5.2 Advanced settings for AP 12.5.3 Network settings for STA 12.5.4 Advanced settings for STA 12.10.4 Device reboot 12.10.5 Configuring authentication mode 12.10.8 Advanced system settings |
| Version 1.0 | 05.2025 | First issue |
| Software version 2.6.1 | ||