
Update options
Using a single server for the SSD does not provide redundancy. Therefore, upgrading to a new version without interrupting traffic is not possible.
There are two ways to upgrade.
The first option is to stop traffic and update PostgreSQL and all ecss packages on the working SSD, then activate the service and start traffic. The advantage of this option is a simple upgrade process. The disadvantage is a longer traffic interruption.
The second option is to perform a complete fresh installation of the OS on a separate host (physical or virtual), and then install the SSD using temporary IP addresses. During the installation, you will also need to copy the databases (Mnesia + PostgreSQL) from the old host to the new one. Once the new SSD is installed, the temporary IP addresses are replaced with those of the old SSD (at this point, the old SSD is disabled) and the MSR files are configured. After this, the new SSD begins serving traffic. The advantage of this option is minimal traffic interruption. The disadvantage is a more complex and time-consuming update procedure.
Select the appropriate option.
ECSS-10 version 3.17 supports two licensing types: file-based licenses (with or without a token) and ELM licenses. Depending on the licensing type, different commands will be executed during the update.
You can check which type is used on your SWS using the following command:
/cluster/storage/ds1/licence/list-licence
When using a file license, the output will be:
/cluster/storage/ds1/licence/list-licence
┌──┬───────────────────┬────────────┬──────┬───────────────────┬────────────────────┬────────────┐
│Id│Creation date(UTC) │   SSW ID   │Active│    Description    │Expiration date(UTC)│ Time left  │
├──┼───────────────────┼────────────┼──────┼───────────────────┼────────────────────┼────────────┤
│1 │31.10.2025 14:16:00│ECSS 010070 │*     │Eltex SC softswitc │31.12.2026 23:59:59 │224d 21h 31m│
│0 │                   │ECSS DEFAULT│      │Default licence    │                    │            │
└──┴───────────────────┴────────────┴──────┴───────────────────┴────────────────────┴────────────┘
When using an ELM license, the output will be:
/cluster/storage/ds1/licence/list-licence
┌──┬───────────────────┬────────────┬──────┬────────────────┬────────────────────┬────────────┐
│Id│Creation date(UTC) │   SSW ID   │Active│  Description   │Expiration date(UTC)│ Time left  │
├──┼───────────────────┼────────────┼──────┼────────────────┼────────────────────┼────────────┤
│1 │02.12.2025 13:51:39│ECSS2000000 │*     │ECSS ELM License│02.12.2026 13:51:39 │364d 11h 47m│
│0 │01.01.1990 00:00:00│ECSS DEFAULT│      │Default licence │                    │            │
└──┴───────────────────┴────────────┴──────┴────────────────┴────────────────────┴────────────┘
Attention
Before performing the update procedure, perform a full backup.
If you need the latest billing data, you need to finalize the current CDR and download the CDR files to a remote server:
/domain/test_domain/cdr/make_finalize_cdr
Created file(s): cdr_20260522_11_51_16_1_c.csv
First option
Attention
Perform a full backup- You need to mask all nodes on the server and disable node autostart:on ecss1
sudo systemctl mask --now ecss-ds ecss-mycelium ecss-mediator ecss-core ecss-pa-sip ecss-sorm
When the attached command is executed, a notification will be displayed.
Warning: The unit file, source configuration file or drop-ins of ecss-ds.service changed on disk. Run 'systemctl daemon-reload' to reload units.
Warning: The unit file, source configuration file or drop-ins of ecss-mycelium.service changed on disk. Run 'systemctl daemon-reload' to reload units.
Warning: The unit file, source configuration file or drop-ins of ecss-mediator.service changed on disk. Run 'systemctl daemon-reload' to reload units.
Warning: The unit file, source configuration file or drop-ins of ecss-core.service changed on disk. Run 'systemctl daemon-reload' to reload units.
Warning: The unit file, source configuration file or drop-ins of ecss-pa-sip.service changed on disk. Run 'systemctl daemon-reload' to reload units.
These messages are not errors. Continue with the procedure.
- Update the ssw repository:on ecss1
sudo sh -c "echo deb [arch=amd64] http://archive.eltex.org/ssw/jammy/3.18 stable main extras external > /etc/apt/sources.list.d/eltex-ecss10-stable.list"
- Perform package update:on ecss1
sudo apt update
If you see this system message:
W: http://archive.eltex.org/ssw/jammy/3.18/dists/unstable/InRelease: Key is stored in legacy trusted.gpg keyring (/etc/apt/trusted.gpg), see the DEPRECATION section in apt-key(8) for details.
Run the following command:
on both hostssudo cp /etc/apt/trusted.gpg /etc/apt/trusted.gpg.d
- Updating PostgreSQL:
- Turn off the Docker container:on ecss2
sudo docker compose -f /srv/ecss/ecss-postgres-bdr-ssw/docker-compose.container.yml down
Example:sudo docker compose -f /srv/ecss/ecss-postgres-bdr-ssw/docker-compose.container.yml down [+] down 2/2 ✔ Container ecss-postgres-bdr-ssw-postgres-container-1 Removed ✔ Network ecss-postgres-bdr-ssw_default Removed
- Remove the old deb package, since the upgrade option is not supported:on ecss2
sudo apt remove ecss-postgres-bdr-ssw
!!Important!!
Run remove, not purge, because remove preserves the volumes directory with our database tables.
Example:sudo apt remove ecss-postgres-bdr-ssw Reading package lists... Done . . . The following packages will be REMOVED: ecss-postgres-bdr-ssw . . . Do you want to continue? [y/n] y Deleting ecss-postgres-bdr-ssw (17.1.0.59+ssw) …
- Install a new deb package:on ecss2
sudo apt install ecss-postgres-bdr-ssw
!!IMPORTANT!!
During installation, you will be asked the same questions as during the initial installation:
The answers must exactly match those specified in the procedure, otherwise an attempt will be made to create a new database and the installation will fail.
Question Reply Example The current IP address of the network interface.
10.0.10.41 (select) 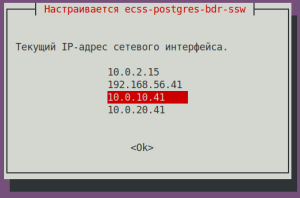
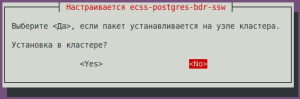
Install on a cluster?
Select <Yes> if the package is installed on a cluster node.
No (select) 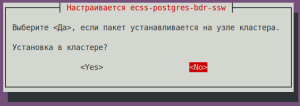 If the installation is successful, at the stage of raising replication we will see:
sudo apt install ecss-postgres-bdr-ssw
. . .
==================
 Create databases
==================
Database ecss_storekeeper_db already exists, skipping...
Database web_conf already exists, skipping...
Extension btree_gist already exists, skipping...
Extension bdr already exists, skipping...

===================================
 Creating Postgres Exporter Schema
===================================
Node IP: localhost
psql:/srv/ecss/ecss-postgres-bdr-ssw/schema.sql:1: NOTICE:  schema "postgres_exporter" already exists, skipping
CREATE SCHEMA
GRANT
CREATE FUNCTION
CREATE VIEW
GRANT
CREATE FUNCTION
CREATE VIEW
GRANT
psql:/srv/ecss/ecss-postgres-bdr-ssw/schema.sql:28: NOTICE:  extension "pg_stat_statements" already exists, skipping
CREATE EXTENSION
CREATE FUNCTION
CREATE VIEW
GRANT
. . .
=======================================================
=======================================================
 ecss-postgres-bdr-ssw successfully installed/updated!
=======================================================
=======================================================


┏┓┏┓┏┓┏┳┓┏┓┳┓┏┓┏┓  ┳┓┳┓┳┓  ┏┓┏┓┓ ┏
┃┃┃┃┗┓ ┃ ┃┓┣┫┣ ┗┓  ┣┫┃┃┣┫  ┗┓┗┓┃┃┃
┣┛┗┛┗┛ ┻ ┗┛┛┗┗┛┗┛  ┻┛┻┛┛┗  ┗┛┗┛┗┻┛
- After installation, check that the new image has been pulled in and Docker has started by running the command:on ecss2
sudo docker ps
example:sudo docker ps CONTAINER ID IMAGE COMMAND CREATED STATUS PORTS NAMES bf73743d3e09 git.eltex.loc:4567/ecss/ecss-postgresbdr:3.18 "/docker-entrypoint.…" About a minute ago Up About a minute 0.0.0.0:5439->5432/tcp, [::]:5439->5432/tcp ecss-postgres-bdr-ssw-postgres-container-1
- Turn off the Docker container:
- Updating the ecss-dns-env package:on ecss1
sudo apt install ecss-dns-env
After the update, you need to update the configuration by running the command. The answers to the questions are similar to the installation procedure:on ecss1sudo dpkg-reconfigure ecss-dns-env
- Update the ecss-user package:
When updating, you need to apply new configuration files (confirm with -Y).
on ecss1sudo apt install ecss-user
- Update the ecss-utils package:on ecss1
sudo apt install ecss-utils
Install the License Provider package:
on ecss2sudo apt install ecss-license-provider
When installing the ecss-license-provider package the following questions will be asked:
Questions Answers Examples License Provider listen ip:
0.0.0.0 (default value) 
License Provider listen port: 4321 (default value) 
Log level: info (default value),
possible options: debug, error, info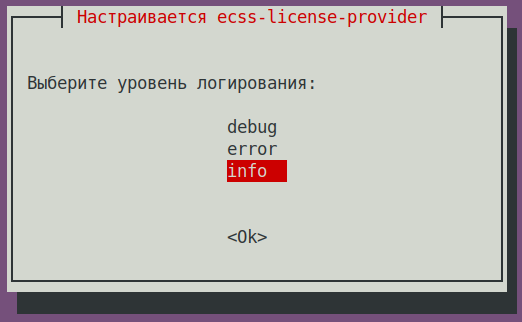
License Provider cluster key: specify a unique name
ecss-lm-cluster (default value)Managers with the same names will attempt to form a cluster for mutual redundancy.
What services should be restarted? ecss-license-provider.service (default value)
The data is saved to the /etc/ecss/ecss-license-provider/config.env file:
ECSS_LM_HOST=0.0.0.0
ECSS_LM_PORT=4321
ECSS_LM_LOG_LEVEL=info
RELEASE_COOKIE=ecss-abf-lm-cluster
Configuring License Provider (LP)
The
ecss-license-providerservice uses two configuration files:/etc/ecss/ecss-license-provider/config.envand/etc/ecss/ecss-license-provider/config.yaml.The information is saved to the
config.envfile when the ecss-license-provider is installed.The config.yaml file contains general settings for connecting to the ELM server and information about licenses: what licenses to take, where to take them from, and where to send them, all this information should be configured manually.
To fill out these fields, open theinformation in the file after installationelm_addresses: [] licenses: [] ecss_nodes: []
ecss-elm-adapterconfiguration file used in the version 3.17/etc/ecss/ecss-elm-adapter/config.env:on ecss2сat /etc/ecss/ecss-elm-adapter/config.env ELM_HOST=elm.eltex-co.ru ELM_PORT=8099 ECSS_PRODUCT_ID=ECSS2000000 ECSS_LICENSE_KEY=ssw987654 LOG_LEVEL=info LICENCE_FAIL_TIMER_SECONDS=10 LICENCE_PULL_TIMER_SECONDS=360
In the
elm_addressesfield, you must specify a list of ELM servers to which you want to connect to obtain licenses. First address in the list is used as the main one. Additional lines contain backup addresses.
Example:
- "elm.eltex-co.ru:8099"
- "192.168.111.22:8099"
- "elm-3.eltex.loc:8099"
Then licenses in the licenses field are specified.- The id can be anything, as long as it is unique for each license. It only affects the license address on the License Provider itself (e.g., 0, 1, 2, 3).
- kind. For SSW, only SSW (in uppercase) is supported.
- type is set to elm if this license is to be requested from the ELM server. If you need to use an SSW file-based license, set the type to ecss_license.
- For the elm type, you must specify the license_key and product_id fields to identify the license.
- For the ecss_license type, specify the license field, which contains the static license key.
license_key = ECSS_LICENSE_KEY and product_id = ECSS_PRODUCT_ID parameters must match the data previously uploaded to the ELM server.
ecss_nodes block.
You must specify the details of the services that will receive the license. A service is defined by three parameters:
- id - the service identifier. In the case of SSW, this must match the ECSS_ID of the SSW being licensed.
- kind - the type of service being licensed. As with the licenses block, the SSW and AUP types are supported. For SSW, only the SSW type is supported.
- license_id - the identifier of the license that will be sent to this service. It corresponds to the license identifiers from the licenses block
Two SSWs with different ECSS_IDs cannot receive the same license; a configuration with such an assignment will be marked as invalid.
Additionally, two SSWs with identical ECSS_IDs cannot simultaneously obtain the same license from a single License Provider; therefore, it is extremely important to set your ECSS_ID correctly and ensure it is unique, at least within the scope of the License Provider being used.ECSS_ID format.
It must begin and end with a Latin letter or a digit; periods and dashes may be used within the string.[A-Za-z0-9][A-Za-z0-9.-][A-Za-z0-9]
Example of a config.yaml file based on data from the fileelm_addresses: - "elm.eltex-co.ru:8099" licenses: - id: 0 kind: SSW type: elm license_key: "ssw987654" product_id: "ECSS2000000" ecss_nodes: - id: eltex1.test kind: ssw license_id: 0
Restart the
ecss-license-provider.serviceservice to up date the configuration from the/etc/ecss/ecss-license-provider/config.yamlfile via the following command:on both hosts if there is a clustersudo systemctl restart ecss-license-provider.service
- Update the ecss-node package:on ecss1
sudo apt install ecss-node
During installation, you will be prompted to configure the settings required to generate the configuration files; examples of possible answers are provided below.
ecss-node questions Answers for ecss1 Example Cookies for the core node:
ecss-core (default value)
It is recommended to replace this with a unique value
Cookies for the ds node:
ecss-ds (default value)
It is recommended to replace this with a unique value
Cookies for the mediator node:
ecss-mediator (default value)
It is recommended to replace this with a unique value
Cookies for the pa-sip node:
ecss-pa-sip (default value)
It is recommended to replace this with a unique value
Cookies for the mycelium node:
ecss-mycelium (default value)
It is recommended to replace this with a unique value
Use the current version of the configuration file?
No (default value)
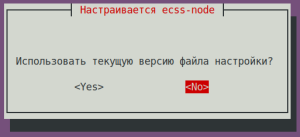
When updating, you must apply the new configuration files (confirm with -Y).
- Enable the nodes.
Enable the SSW services using the following commands:on ecss1sudo systemctl unmask ecss-ds ecss-mycelium ecss-mediator ecss-core ecss-pa-sip ecss-sorm
on ecss1sudo systemctl enable ecss-ds ecss-mycelium ecss-mediator ecss-core ecss-pa-sip ecss-sorm
- Starting SSW on ecss1. Start the following services:
ecss-myceliumecss-dson ecss1sudo systemctl start ecss-mycelium
ecss-coreon ecss1sudo systemctl start ecss-ds
ecss-mediatoron ecss1sudo systemctl start ecss-core
on ecss1sudo systemctl start ecss-mediator
Do not start PA-SIP yet
- Check the status of services by running the
system-statuscommand in CoCon:performed in CoCon/system-status Checking... ┌─┬───────────────┬────────────────────────┬───────────────┬────────────┬──────┐ │ │ Node │ Release │ Erlang nodes │Mnesia nodes│Uptime│ ├─┼───────────────┼────────────────────────┼───────────────┼────────────┼──────┤ │ │core1@ecss1 │ecss-core-3.18.0.271 │core1@ecss1 │not running │14m 4s│ │ │ds1@ecss1 │ecss-ds-3.18.0.271 │ds1@ecss1 │ds1@ecss1 │14m 4s│ │ │md1@ecss1 │ecss-mediator-3.18.0.271│md1@ecss1 │md1@ecss1 │14m 4s│ │ │mycelium1@ecss1│ecss-mycelium-3.18.0.271│mycelium1@ecss1│not running │14m 4s│ │ │sorm1@ecss1 │ecss-sorm-3.18.0.271 │sorm1@ecss1 │not running │14m 5s│ └─┴───────────────┴────────────────────────┴───────────────┴────────────┴──────┘ All services are started. Active media resource selected list specific: ┌─────────────┬───────────┬────────────┬───────────┬───────────┐ │ Node │ MSR │ MSR │ Cc-status │ Cc-uptime │ │ │ │ version │ │ │ ├─────────────┼───────────┼────────────┼───────────┼───────────┤ │ core1@ecss1 │ msr.ecss1 │ 3.17.1.1.7 │ connected │ 00:43:03 │ └─────────────┴───────────┴────────────┴───────────┴───────────┘
- Режимы лицензирования.
- Updating the
ecss-restfspackage.Accept all new configuration files by choosing Y.
on ecss1sudo apt install ecss-restfs
- Updating the
ecss-media-serverpackage.Perform an update:The Media Server analyzes the configuration in the files located in the /etc/ecss/ecss-media-server/ directory. Version 3.17 introduces a new feature for managing codec priorities. If, for any reason, multiple files contain a codec section that lists the same codec more than once, a conflict will occur after the update, and the Media Server will not function.
Therefore, there should be no conflicts regarding codec priorities in the configuration files of a single Media Server (there should be only one entry for one codec, and it should not be repeated in other files). The decision regarding which specific files need to be configured is left to the discretion of the system administrator.
Accept all new configuration files by choosing Y.
Update the configuration:on ecss1sudo apt install ecss-media-server
on ecss1sudo dpkg-reconfigure ecss-media-server
- Updating the ecss-media-resources packageon ecss1
sudo apt install ecss-media-resources
- Updating the ecss-web-conf packageon ecss1
sudo apt install ecss-web-conf
- Launch ecss-pa-sip:Check the status of services by running the /system-status command:on ecss1
sudo systemctl start ecss-pa-sip
Verify that active registrations have been migrated to the updated host. To do this, check the registered subscribers on SSW. Execute the following command in CoCon:performed in CoCon/system-status Checking... ┌─┬───────────────┬────────────────────────┬───────────────┬────────────┬───────┐ │ │ Node │ Release │ Erlang nodes │Mnesia nodes│Uptime │ ├─┼───────────────┼────────────────────────┼───────────────┼────────────┼───────┤ │ │core1@ecss1 │ecss-core-3.18.0.271 │core1@ecss1 │not running │54m 27s│ │ │ds1@ecss1 │ecss-ds-3.18.0.271 │ds1@ecss1 │ds1@ecss1 │54m 27s│ │ │md1@ecss1 │ecss-mediator-3.18.0.271│md1@ecss1 │md1@ecss1 │54m 27s│ │ │mycelium1@ecss1│ecss-mycelium-3.18.0.271│mycelium1@ecss1│not running │54m 27s│ │ │sip1@ecss1 │ecss-pa-sip-3.18.0.271 │sip1@ecss1 │sip1@ecss1 │54m 27s│ │ │sorm1@ecss1 │ecss-sorm-3.18.0.271 │sorm1@ecss1 │not running │54m 27s│ └─┴───────────────┴────────────────────────┴───────────────┴────────────┴───────┘ All services are started. Active media resource selected list specific: ┌─────────────┬───────────┬──────────┬───────────┬───────────┐ │ Node │ MSR │ MSR │ Cc-status │ Cc-uptime │ │ │ │ version │ │ │ ├─────────────┼───────────┼──────────┼───────────┼───────────┤ │ core1@ecss1 │ msr.ecss1 │ 3.18.0.7 │ connected │ 00:01:17 │ └─────────────┴───────────┴──────────┴───────────┴───────────┘
performed in CoCon/domain/test_domain/sip/user/registered sip * 450 make users list ... [**********************************************************************] 28mks 450 users information read ... [**********************************************************************] 1ms Executed on the sip1@ecss1 ┌───────────────┐ │ elements: 436 │ └───────────────┘
- After the update is complete, verify that all SSW services are functioning properly.
Second option
Initial data
Use temporary IP addresses during installation (10.0.10.51/10.0.20.51 in the example). In the final steps, the temporary addresses will be replaced with the actual IP addresses for SSW version 3.17 (10.0.10.41/10.0.20.41 in the example).
According to the technical specifications, the hardware platform must be determined.
Connecting to the network
To ensure redundancy, it is recommended to use two switches when configuring the server’s network topology.
 draw.io
Figure 1 – Network connection diagram
Option 1. Active-backup configuration
The switches are interconnected in an ERPS ring.
All four physical network interfaces are combined into a single aggregated link (bond). The server’s port aggregation is configured in active-backup mode, meaning that only one network interface is active at any given time. The server’s network interfaces are connected in pairs to the switches, on which the port aggregation (port-channel) is also configured in active-backup mode.
For example, eth1 and eth2 are connected to the first switch, while eth3 and eth4 are connected to the second.
Option 2. LACP diagram
The switches are linked together in a stack. The stack must function logically as a single switch capable of providing port aggregation in LACP mode across different physical switches. An example is the MES3124 switches with specialized firmware.
All four physical network interfaces are also combined into a single aggregated link (bond). Server port aggregation is configured in 802.3ad mode. Aggregated groups of network cards with the same speed and duplex settings are created. With this configuration, data transmission utilizes all channels in the active aggregation in accordance with the IEEE 802.3ad standard. The choice of which interface to send a packet through is determined by a policy. By default, this is the XOR policy; the “xmit_hash” policy can also be used.
Requirements:
- Ethtool support in the driver to retrieve information about the speed and duplex settings on each network interface;
- Support for the IEEE 802.3ad standard on the switch;
The server’s network interfaces are also connected in pairs to switches on which port aggregation (port-channel) is configured in LACP mode. For example, eth1 and eth2 are connected to the first switch (port-channel 1), and eth3 and eth4 are connected to the second (port-channel 2).
Installing the OS
"Оптимизация" операционной системы
Выставить параметры ОС в режим производительности
Используем утилиту cpufrequtils.
sudo apt install cpufrequtils
по умолчанию после установки Ubuntu используется режим "ondemand" - "по запросу" (производительность CPU по запросу приложений, экономит электроэнергию, но снижает производительность):
cat /etc/init.d/cpufrequtils | grep GOVERNOR=
в выходном сообщении системы режим работы по умолчанию после установки - "ondemand" :
GOVERNOR="ondemand"
Установить режим результативности/производительности - в файле /etc/init.d/cpufrequtils значение "ondemand" заменить на "performance"
sudo sed -i 's/GOVERNOR="ondemand"/GOVERNOR="performance"/g' /etc/init.d/cpufrequtils
Перезапустить утилиту:
sudo /etc/init.d/cpufrequtils restart
Затем выполнить команду:
sudo systemctl daemon-reload
Отключить SWAP
Ubuntu сервер SSW работает в реальном масштабе времени , поэтому все необходимые данные должны находится в оперативной памяти, использование файла подкачки (swap-файл - /swap. img) может привести к увеличению времени обработки вызовов приложения SSW ECSS10 , что недопустимо. Swap - отключаем.
Выполнить последовательно три команды:
Отключение Swap:
sudo swapoff -a
Удалить файл swap.img.
sudo rm /swap.img
Закомментировать строку - /swap.img none swap sw 0 0 - в файле /etc/fstab - выполнив команду "sudo nano /etc/fstab"
привести её к виду # /swap.img none swap sw 0 0
либо удалить эту строчку (/swap.img none swap sw 0 0)
sudo nano /etc/fstab
Для проверки выполните команду free -h:
free -h
Размер Swap равен 0 — значит, он выключен
free -h
total used free shared buff/cache available
Mem: 3,9G 110M 3,2G 820K 535M 3,5G
Swap: 0B 0B 0B
Установка часового пояса
При инсталляции Ubuntu-22 не предлагается установить часовой пояс (по умолчанию — UTC). Его нужно установить вручную (для корректной работы системы тарификации, работ по расписанию и т. д.), например:
sudo timedatectl set-timezone Asia/Novosibirsk
Улучшение работы высоконагруженных серверов
Улучшить работу высоконагруженных серверов можно увеличив лимит открытых файлов.
Для установки лимита открытых файлов необходимо:
Проверить текущий лимит командой:
ulimit -a
результат :
eltex@ecss1:~$ ulimit -a core file size (blocks, -c) 0 data seg size (kbytes, -d) unlimited scheduling priority (-e) 0 file size (blocks, -f) unlimited pending signals (-i) 15515 max locked memory (kbytes, -l) 65536 max memory size (kbytes, -m) unlimited open files (-n) 1024 pipe size (512 bytes, -p) 8 POSIX message queues (bytes, -q) 819200 real-time priority (-r) 0 stack size (kbytes, -s) 8192 cpu time (seconds, -t) unlimited max user processes (-u) 15515 virtual memory (kbytes, -v) unlimited file locks (-x) unlimited
Данного лимита (open files 1024 ) недостаточно для нормальной работы высоконагруженных серверов.
Установить лимит открытых файлов для каждого пользователя:
sudo sed -i '55i\* soft nproc 65536\n* hard nproc 131072\n* soft nofile 65536\n* hard nofile 131072\nroot - memlock unlimited' /etc/security/limits.conf
ВАЖНО
Обновление программного обеспечения операционной системы
- Для установки системы ECSS-10 необходимо добавить репозиторий ELTEX:на новом ssw
sudo sh -c "echo 'deb [arch=amd64] http://archive.eltex.org/ssw/jammy/3.18 stable main extras external' > /etc/apt/sources.list.d/eltex-ecss10-stable.list"
Далее необходимо выполнить импорт ключа командой:
на новом sswsudo apt-key adv --keyserver keyserver.ubuntu.com --recv-keys 33CB2B750F8BB6A5
Перед началом установки необходимо обновить ОС:
на новом sswsudo apt update
Если вы видите такое сообщение системы:
W: http://archive.eltex.org/ssw/jammy/3.18/dists/stable/InRelease: Key is stored in legacy trusted.gpg keyring (/etc/apt/trusted.gpg), see the DEPRECATION section in apt-key(8) for details.
Выполните следующую команду:
на новом sswsudo cp /etc/apt/trusted.gpg /etc/apt/trusted.gpg.d
на новом sswsudo apt upgrade
Установка и настройка программного обеспечения
установка пакетов deb
┌ версия ПО ECSS. Сейчас в заявке на сертификацию она заявлена как 3.
| Мы её менять не будем до следующей сертификации или │ выпуска принципиально новой версии системы. │ │ ┌ версия System Release. Общая версия для всех компонент входящих в конкретный релиз.
| | Меняем её централизовано, когда
│ │ принимаем решение о выпуске нового релиза. Релизы между собой обычно не совместимы.
┌─┴┐ ┌──┴─┐
ECSS.SysRel.SubMaj.SubMin
└──┬─┘ └──┬─┘
│ └ версия Subsystem minor. Минорную версию подсистемы устанавливает разработчик подсистемы. | Минорную версию
│ меняем при добавлении патча. Как правило, минорные версии в рамках одной мажорной версии
│ совместимы между собой и отличаются в рамках конкретных патчей.
│
└ версия Subsystem major. Мажорная версия устанавливается разработчиком подсистемы. Мажорную версию подсистемы необходимо менять при внесении в подсистему существенных изменений.
Утилита установки пакетов APT анализирует версию пакета слева направо, для примера мы имеем пакет 14.14.7.7 ,
в репозитории находятся пакеты
14.14.7.8
14.14.7.9
14.14.8.1
14.14.20 -14.14.28
то при выполнении команды sudo apt install имя пакета → будет автоматически проверен и установлен пакет 14.14.28 , так как он самый последний, анализ будет выполнен по 3-й позиции (major), анализ по 4-й (minor) выполнен не будет (аналогичным образом будет выполнятся команда sudo apt upgrade).
В случае если для конкретной ситуации требуется перейти с версии 14.14.7.7 на версию 14.14.7.9 , стандартная команда → sudo apt upgrade , нам не поможет, так как будет выбран самый новый пакет, в данной ситуации нам необходимо в явном виде указать какую версию пакета мы хотим установить, в данном примере мы должны выбрать команду → sudo apt install имя пакета=14.14.7.9 . Обычно это необходимо для тестирования определенного патча, для стандартных обновлений достаточно выбора привычной команды установки /обновления пакета
Устанавливаем все предложенные пакеты:
sudo apt install ntp ntpdate tcpdump vlan dnsmasq aptitude atop ethtool htop iotop mc minicom mtr-tiny nmap pptpd pv screen ssh tftpd vim sngrep tshark cpanminus gnuplot libgraph-easy-perl debconf-utils wget rsync ncdu
Перед началом установки пакетов ecss , нужно убедиться в соответствии полосы пропускания СПД необходимым требованиям.
Для этого выполнить команду sudo ethtool <имя интерфейса> для всех физических интерфейсов.
Проверить значение следующих параметров:
Advertised auto-negotiation: Yes
Speed: 1000Mb/s (не менее)
Duplex: Full
Настройка пакета ecss-dns-env
Выполнить следующую команду:
sudo apt install -y ecss-dns-env
Настройщик предложит выбрать разделы для настройки по вопросам ниже. Нужно выбрать broker. (для примера 10.0.10.51)
| Вопрос ecss-dns-env | Ответы для ecss1 | |
|---|---|---|
| [Primary broker] Введите адрес ([Primary broker] Enter ip) | 10.0.10.51 (необходимо ввести) |
|
| [Secondary broker] Введите адрес ([Secondary broker] Enter ip) | 10.0.10.51 (необходимо ввести) |
|
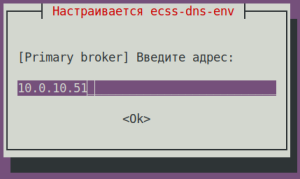
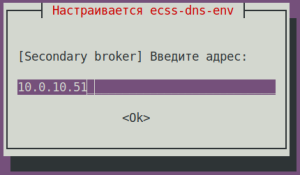
ВАЖНО
В случае последующей коррекции IP-адресов следует использовать команду:
sudo dpkg-reconfigure ecss-dns-env
Установка Postgres
Примечание
Перед установкой ecss-postgres-bdr-ssw в системе, в apt sources, должен быть добавлен docker для этого выполнить следующие команды:
sudo install -m 0755 -d /etc/apt/keyrings
sudo curl -fsSL https://download.docker.com/linux/ubuntu/gpg -o /etc/apt/keyrings/docker.asc
sudo chmod a+r /etc/apt/keyrings/docker.asc
sudo sh -c "echo 'deb [arch=amd64 signed-by=/etc/apt/keyrings/docker.asc] https://download.docker.com/linux/ubuntu jammy stable' >> /etc/apt/sources.list.d/docker.list"
sudo apt update && sudo apt upgrade
Установка пакета ecss-postgres-bdr-ssw
Выполнить установку пакета ecss-postgres-bdr-ssw:
sudo apt install ecss-postgres-bdr-ssw
При конфигурации пакета ecss-postgres-bdr-ssw будут заданы вопросы:
| Вопросы ecss-postgres-bdr-ssw | Ответы для ecss1 | Пример |
|---|---|---|
| Текущий IP-адрес сетевого интерфейса (Выбрать адрес ранее используемый MySQL). | Выбрать из списка IP-адрес для работы с Postgres |
|
| Установка в кластере? | No (необходимо выбрать) |
|
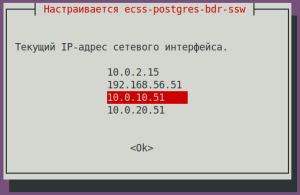
. . . ================== Create databases ================== CREATE DATABASE CREATE DATABASE CREATE EXTENSION CREATE EXTENSION =================================== Creating Postgres Exporter Schema =================================== Node IP: localhost CREATE SCHEMA GRANT CREATE FUNCTION CREATE VIEW GRANT CREATE FUNCTION CREATE VIEW GRANT CREATE EXTENSION CREATE FUNCTION CREATE VIEW GRANT ======================================================= ======================================================= ecss-postgres-bdr-ssw successfully installed/updated! ======================================================= ======================================================= ┏┓┏┓┏┓┏┳┓┏┓┳┓┏┓┏┓ ┳┓┳┓┳┓ ┏┓┏┓┓ ┏ ┃┃┃┃┗┓ ┃ ┃┓┣┫┣ ┗┓ ┣┫┃┃┣┫ ┗┓┗┓┃┃┃ ┣┛┗┛┗┛ ┻ ┗┛┛┗┗┛┗┛ ┻┛┻┛┛┗ ┗┛┗┛┗┻┛
Установить пакет License Provider:
sudo apt install ecss-license-provider
При установке пакета ecss-license-provider будут заданы вопросы:
| Вопросы | Ответы | Примеры |
|---|---|---|
Адрес для соединения с License Provider: | 0.0.0.0 (значение по умолчанию) |
|
| Порт для соединения c License Provider: License Provider listen port: | 4321 (значение по умолчанию) |
|
| Выберите уровень логирования: Log level: | info (значение по умолчанию), возможные варианты: debug, error, info |
|
| Ключ-имя кластера резервирования: License Provider cluster key: | указать уникальное имя Менеджеры с одинаковыми именами попытаются собраться в кластер и резервировать друг друга. |
|
Данные сохраняются в файле /etc/ecss/ecss-license-provider/config.env:
ECSS_LM_HOST=0.0.0.0 ECSS_LM_PORT=4321 ECSS_LM_LOG_LEVEL=info RELEASE_COOKIE=ecss-abf-lm-cluster
Конфигурация License Provider (LP)
Сервис ecss-license-provider использует два конфигурационных файла: /etc/ecss/ecss-license-provider/config.env и /etc/ecss/ecss-license-provider/config.yaml.
В файл config.env информация сохраняется в момент установки пакета ecss-license-provider.
Config.yaml файл содержит основные настройки для подключения к ELM-серверу, откуда брать лицензии, какие лицензии, и куда их потом передавать, все это нужно сконфигурировать вручную.
elm_addresses: []
licenses: []
ecss_nodes: []
сat /etc/ecss/ecss-elm-adapter/config.env
ELM_HOST=elm.eltex-co.ru
ELM_PORT=8099
ECSS_PRODUCT_ID=ECSS2000000
ECSS_LICENSE_KEY=ssw987654
LOG_LEVEL=info
LICENCE_FAIL_TIMER_SECONDS=10
LICENCE_PULL_TIMER_SECONDS=360
В поле elm_adresses нужно прописать список серверов ELM, к которым мы хотим подключаться для получения лицензий. Первый адрес в списке используется как основной. Дополнительные строки с адресами работают как резерв.
пример:
- "elm.eltex-co.ru:8099"
- "192.168.111.22:8099"
- "elm-3.eltex.loc:8099"
Дальше задаются сами лицензии в поле licenses.
- id может быть любой, главное чтоб был уникальный у каждой лицензии. Влияет только на адрес лицензии на самом License Provider (например 0, 1, 2, 3).
- kind. Для SSW поддерживается только SSW (заглавными буквами).
- type выбирается как elm, если запрашивать данную лицензию нужно с ELM-сервера. Если нужно использовать файловую лицензию SSW, то тип выбирается как ecss_license.
- при elm типе необходимо задать поля license_key и product_id для идентификации лицензии.
- при ecss_license типе задается поле license, содержащее ключ статичной лицензии.
Параметры license_key = ECSS_LICENSE_KEY и product_id = ECSS_PRODUCT_ID должны быть согласованы с данными, ранее загруженными на ELM-сервере.
Блок ecss_nodes.
В нем нужно задать данные сервисов, которые будут получать лицензию. Сервис задается тремя параметрами:
- id - идентификатор сервиса. В случае с SSW должен совпадать с ECSS_ID лицензируемого SSW.
- kind - тип лицензируемого сервиса. По аналогии с блоком лицензий, поддерживаются типы SSW и AUP. Для SSW поддерживается только SSW.
- license_id - идентификатор лицензии, которая будет отправляться на данный сервис. Соответствует идентификаторам лицензии из блока licenses.
Кроме того, два SSW с одинаковыми ECSS_ID не смогут одновременно получать одну и ту же лицензию с одного License Provider, поэтому крайне важно корректно устанавливать свой ECSS_ID и делать его уникальным как минимум в зоне видимости используемого License Provider.
ECSS_ID указанный в файле /etc/ecss/ecss-license-provider/config.yaml, должен совпадать с ECSS_ID ( идентификатор ECSS-узла) которое указываем при установке пакета ecss-node
При обновлении, имя нового ECSS-узла (ECSS_ID) нужно обязательно указывать отличное от имени старого ECSS-узла. В противном случае при их совпадении сервис ecss-mycelium не активируется.
Формат ECSS_ID:
Начинается и заканчивается обязательно латинской буквой или цифрой, в теле же могут использоваться точки и тире.
[A-Za-z0-9][A-Za-z0-9.-][A-Za-z0-9]
elm_addresses:
 - "elm.eltex-co.ru:8099"
licenses:
 - id: 0
   kind: SSW
   type: elm
   license_key: "ssw987654"
   product_id: "ECSS2000000"
ecss_nodes:
 - id: test.update
   kind: ssw
   license_id: 0
Выполнить перезагрузку сервиса ecss-license-provider.service для обновления конфигурации из файла /etc/ecss/ecss-license-provider/config.yaml следующей командой:
sudo systemctl restart ecss-license-provider.service
Установка ecss-node
Установка обязательного пакета ecss-node включает в себя установку и первоначальную настройку основных подсистем.
В системе уже должен быть установлен пакет ecss-postgres-bdr-ssw
Для установки пакета ecss-node выполните команду:
sudo apt install -y ecss-node
Во время установки пакета создается пользователь ssw, от имени которого запускаются все сервисы ecss*. Создаются необходимые каталоги, выполняется настройка DNS, идет настройка SSL-сертификатов.
При установке также будет установлен пакет ecss-user
Во время установки будет предложено настроить параметры, необходимые для формирования конфигурационных файлов, примеры ответов следует ниже.
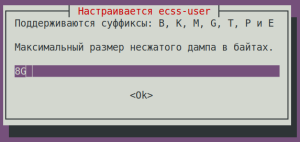
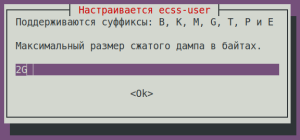
| Вопросы ecss-user | Ответы для ecss1 | Пример |
|---|---|---|
Хотите ли вы использовать стандартные настройки? | Yes (значение по умолчанию) |
|
| Вопросы ecss-node | Ответы для ecss1 | Пример |
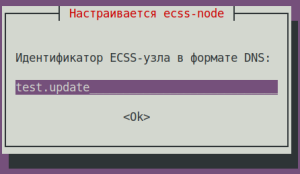
Идентификатор ECSS-узла в формате DNS (Настройка имени кластера): (любое уникальное имя, в примере test.update) При обновлении, имя нового ECSS-узла нужно обязательно указывать отличное от имени старого ECSS-узла. В противном случае при их совпадении сервис ecss-mycelium не активируется. Идентификатор ECSS-узла должен совпадать с ECSS_ID указанном в файле конфигурации провайдера лицензий - /etc/ecss/ecss-license-provider/config.yaml.
| test.update (необходимо ввести) Формат ECSS_ID: [A-Za-z0-9][A-Za-z0-9.-][A-Za-z0-9] |
|
| Хотите ли вы использовать стандартные настройки? | Yes (значение по умолчанию) |
|
| Вопросы ecss-user | Ответы для ecss1 | Пример |
| Максимальный размер несжатого дампа в байтах. | 8G (значение по умолчанию) |
|
| Максимальный размер сжатого дампа в байтах. | 2G (значение по умолчанию) |
|
| Максимальный размер, который может занять каталог /var/lib/systemd/coredump: | default (значение по умолчанию) |
|
| Минимальный объем свободного дискового пространства в байтах. | 30G (значение по умолчанию) |
|
Сохраните в безопасное место и удалите файл /etc/ecss/ssl/ecss10root.key! | Ok (значение по умолчанию) |
|
Cookie для ноды core: | ecss-core (необходимо ввести) |
|
Cookie для ноды ds: | ecss-ds (необходимо ввести) |
|
Cookie для ноды mediator: | ecss-mediator (необходимо ввести) |
|
Cookie для ноды pa-sip: | ecss-pa-sip (необходимо ввести) |
|
Cookie для ноды mycelium: | ecss-mycelium (необходимо ввести) |
|
Cookie для ноды sorm: | ecss-sorm (необходимо ввести) |
|
Проверить информацию о состоянии синхронизации c NTP, используется команда ntpq –p . Если использовать дополнительный ключ –n, вместо имени сервера будет указан IP-адрес:
ntpq -p
     remote           refid      st t when poll reach   delay   offset  jitter
==============================================================================
*185.125.190.56  17.253.28.253    2 u   45   64    1   83.893   +0.470   2.177
Остановить сервисы:
sudo systemctl stop ecss-core ecss-pa-sip ecss-ds ecss-mediator ecss-mycelium
Создать backup для oasys (скопировать БД Mnesia со старого на новый ecss1), выполнить следующие команды:
cd /var/lib/ecss/oasys/
sudo rsync -a <Ваш_пользователь>@<IP_add_старого_сервера>:/var/lib/ecss/oasys/Mnesia.ds1@ecss1/ Mnesia.ds1@ecss1/
sudo rsync -a <Ваш_пользователь>@<IP_add_старого_сервера>:/var/lib/ecss/oasys/Mnesia.md1@ecss1/ Mnesia.md1@ecss1/
cd ~
Перезапустить сервисы SSW:
sudo systemctl restart ecss-core ecss-pa-sip ecss-ds ecss-mediator ecss-mycelium
Если лицензия поддерживает СОРМ3, то запустить также сервис ecss-sorm.
sudo systemctl start ecss-sorm
Проверить статус сервисов, для этого выполнить в CoCon команду system-status:
/system-status
Checking...
┌─┬───────────────┬─────────────────────────┬───────────────┬────────────┬──────┐
│ │     Node      │         Release         │ Erlang nodes  │Mnesia nodes│Uptime│
├─┼───────────────┼─────────────────────────┼───────────────┼────────────┼──────┤
│ │core1@ecss1    │ecss-core-3.18.0.271     │core1@ecss1    │not running │3m 55s│
│ │ds1@ecss1      │ecss-ds-3.18.0.271       │ds1@ecss1      │ds1@ecss1   │4m 40s│
│ │md1@ecss1      │ecss-mediator-3.18.0.271 │md1@ecss1      │md1@ecss1   │3m 50s│
│ │mycelium1@ecss1│ecss-mycelium-3.18.0.271 │mycelium1@ecss1│not running │5m 28s│
│ │sip1@ecss1     │ecss-pa-sip-3.18.0.271   │sip1@ecss1     │sip1@ecss1  │3m 45s│
│ │sorm1@ecss1    │ecss-sorm-3.18.0.271     │sorm1@ecss1    │not running │1m 55s│
└─┴───────────────┴─────────────────────────┴───────────────┴────────────┴──────┘
Режимы лицензирования.
Лицензирование с использованием файловой лицензии
Лицензирование с использованием ELM сервиса
Установка пакетов ecss-restfs, ecss-media-server, ecss-web-conf
Далее устанавливаются пакеты ecss-restf затем ecss-media-server, ecss-media-resources, , ecss-web-conf и другие в любом порядке:
ecss-restfs
sudo apt install -y ecss-restfs
Установка ecss-restfs.
При установке пакета ecss-restfs будет предложено задать параметры конфигурации. Ответы на вопросы приведены ниже. Также инсталлятор предложит установить и настроить пакет Text2speech от Yandex.
| Вопросы ecss-restfs | Ответы |
|---|---|
Использование функции TTS (Use TTS service) | No (значение по умолчанию) |
Настройка телефонной книги (Configure phone book) | No (значение по умолчанию) |
Настроить сервис определения речи (Configure speech recognition service) | No (значение по умолчанию) |
Ничего не выбирать | Ok |
после установки пакета ecss-restfs проверьте наличие wav файлов автоинформатора в директории /var/lib/ecss/restfs/system/sounds/ командой :
ll /var/lib/ecss/restfs/system/sounds/
наличие wav-файлов в указанной выше директории говорит о корректности установки пакета ecss-restfs
Отсутствия wav файлов в указанной выше директории, директории свидетельствует о проблеме при установке пакета ecss-restfs. Для ее решения выполните команду:
sudo apt --fix-broken install
и повторите команду проверки:
ll /var/lib/ecss/restfs/system/sounds/
осталось проверить доступность этих файлов извне. Для проверки выполните команду:
wget http://ecss1:9990/system/sounds/ai_you.wav
wget http://ecss1:9990/system/sounds/ai_you.wav
--2026-04-18 17:43:29--  http://ecss1:9990/system/sounds/ai_you.wav
Resolving ecss1 (ecss1)... 127.0.1.1, 10.0.10.51
Connecting to ecss1 (ecss1)|127.0.1.1|:9990... connected.
HTTP request sent, awaiting response... 200 OK
Length: 11670 (11K) [audio/x-wav]
Saving to: ‘ai_you.wav’

ai_you.wav                                  100%[========================================================================================>]  11,40K  --.-KB/s    in 0s

2026-04-18 17:43:29 (301 MB/s) - ‘ai_you.wav’ saved [11670/11670]
проверочный файл можно удалить
rm ai_you.wav
Перенести записи разговоров со старого сервера на новый, выполнив следующую команду:
sudo rsync -a <ваш_пользователь>@<IP_add_старого_ecss1>:/var/lib/ecss/restfs/domain/ /var/lib/ecss/restfs/domain/
abf@ecss1:/var/lib/ecss/restfs/domain$ ls -la /var/lib/ecss/restfs/domain
итого 8
drwxr-xr-x 2 www-data www-data 4096 апр 22 18:21 .
drwxr-xr-x 7 www-data www-data 4096 мая 28 15:07 ..

abf@ecss1:/var/lib/ecss/restfs/domain$ sudo rsync -a abf@10.0.10.10:/var/lib/ecss/restfs/domain/ /var/lib/ecss/restfs/domain/

abf@ecss1:/var/lib/ecss/restfs/domain$ ls -la test_domain/records/2026_05_28
итого 610
drwxrwxrwx 2 www-data www-data  4096 мая 28 14:56 .
drwxrwxrwx 3 www-data www-data  4096 мая 28 14:27 ..
-rw-r--r-- 1 www-data www-data 71892 мая 28 14:27 2026-05-28_14-27-02_t_42009-42007.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:27 2026-05-28_14-27-02_t_42009-42007.pcm.meta
-rw-r--r-- 1 www-data www-data 71892 мая 28 14:31 2026-05-28_14-31-19_o_42007-42009.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:31 2026-05-28_14-31-19_o_42007-42009.pcm.meta
-rw-r--r-- 1 www-data www-data 63904 мая 28 14:55 2026-05-28_14-55-24_o_42007-42009.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:55 2026-05-28_14-55-24_o_42007-42009.pcm.meta
-rw-r--r-- 1 www-data www-data 39940 мая 28 14:55 2026-05-28_14-55-31_o_42007-42009.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:55 2026-05-28_14-55-31_o_42007-42009.pcm.meta
-rw-r--r-- 1 www-data www-data 15976 мая 28 14:55 2026-05-28_14-55-37_o_42007-42009.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:55 2026-05-28_14-55-37_o_42007-42009.pcm.meta
-rw-r--r-- 1 www-data www-data 79880 мая 28 14:55 2026-05-28_14-55-48_o_42007-42009.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:55 2026-05-28_14-55-48_o_42007-42009.pcm.meta
-rw-r--r-- 1 www-data www-data 55916 мая 28 14:56 2026-05-28_14-55-59_o_42007-42009.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:55 2026-05-28_14-55-59_o_42007-42009.pcm.meta
-rw-r--r-- 1 www-data www-data 47928 мая 28 14:56 2026-05-28_14-56-04_o_42007-42009.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:56 2026-05-28_14-56-04_o_42007-42009.pcm.meta
-rw-r--r-- 1 www-data www-data 31952 мая 28 14:56 2026-05-28_14-56-28_t_42009-42007.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:56 2026-05-28_14-56-28_t_42009-42007.pcm.meta
-rw-r--r-- 1 www-data www-data 31952 мая 28 14:56 2026-05-28_14-56-37_t_42009-42007.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:56 2026-05-28_14-56-37_t_42009-42007.pcm.meta
-rw-r--r-- 1 www-data www-data 95856 мая 28 14:56 2026-05-28_14-56-42_t_42009-42007.pcm
-rw-rw-rw- 1 www-data www-data    86 мая 28 14:56 2026-05-28_14-56-42_t_42009-42007.pcm.meta
ecss-media-server
sudo apt install -y ecss-media-server
Для медиасервера (ecss-media-server/MSR) можно выполнить начальную настройку с записью параметров в файл конфигурации,
для этого нужно провести конфигурацию transport bind-addr,mcc bind-addres:
Укажите IP-адреса старого SSW версии 3.17 (в примере 10.0.20.41).
| Вопросы ecss-media-server | Ответы для ecss1 |
|---|---|
| [ MSR SIP ] Введите bind-ip адрес (Enter) | 10.0.20.41 (необходимо ввести) |
| [MSR Control-Channel] Введите bind-ip-адрес | 10.0.20.41 (необходимо ввести) |
После формирования конфигураций по умолчанию выполните проверку:
cat /etc/ecss/ecss-media-server/config.xml
Внутри лежит конфигурация для msr: config.xml, в директории conf.d лежит конфигурация default.xml.
По своей сути default.xml — это дополнение config.xml, которое определяет секцию аккаунтов. Это сделано для того, чтобы после обновлений пакета данная конфигурация оставалась неизменной. Вид config.xml представлен здесь: файл конфигурации.
<?xml version="1.0" encoding="utf-8"?>
<config date="09:24:23 03.12.2025">
  <general log-level="3" log-rotate="yes" max-calls="2148" max-vid-calls="100" max-in-group="512" load-sensor="media" load-delta="10" calls-delta="100" spool-dir-size="100M" log-name="msr.log" log-path="/var/log/ecss/media-server" use-srtp="disabled" enable-ice-transport="no" ice-update="no" aggressive-ice="yes" stun-server="" suspicious-mode="no"/>
  <transport bind-addr="10.0.20.41" port="5040" transport="udp+tcp"/>
  <!-- By default configured public TURN-server -->
  <turn-server use-turn="no" host="numb.viagenie.ca" user="webrtc@live.com" password="muazkh"/>
  <media mixer-clock-rate="8000" use-vad="no" cng-level="0" jb-size="60" rtcp-timeout="0" rtp-timeout="350" udp-src-check="no" cn-multiplier="3" port-start="12000" port-range="4496" tias-in-sdp="no" thread-cnt="2" vid-enc-threads="2" vid-dec-threads="2" video-conf-layout="evenly" keyframe-interval="1000" vid-decode-delay="100" silent-codec-switch="yes" silence-threshold="-30" dtmf-flash-disable="no" video-dscp="0" other-dscp="0" dummy-video-src="/usr/share/ecss-media-server/video/dummy_video.yuv" video-enc-width="640" video-enc-height="360" finalsilence="1000" rtcp-stat-dump="yes" dtmf-tg-fpc-loop="10" dtmf-tg-fit="1" dtmf-tg-fot="2" dtmf-tg-volume="12288"/>
  <codec pcma="1" pcmu="2" ilbc="0" gsm="0" g722="3" g726="0" g729="0" speex="0" l16="0" g7221="0" opus="0" h264="1" h263-1998="2" t38="1" tel-event-pt="0"/>
  <accounts>
    <!-- <dynamic msr_name="msr.name"
            realm="sip:127.0.0.1:5000"
            dtmf_mode="rfc+inband+info"
            auth_name="user"
            auth_password="password" /> -->
  </accounts>
  <pbyte>
    <mcc bind-addr="10.0.20.41" port="5700"/>
  </pbyte>
  <conf_dir path="/etc/ecss/ecss-media-server/conf.d"/>
  <metrics enable="yes" use-pushgateway="yes" pushgateway-addr="127.0.0.1:9091" push-interval="5" port="8100" msr_name="msr2"/>
  <rtp>
    <auto addr-v4=""/>
  </rtp>
</config>
по умолчанию , после инсталляции ECSS-10 активизирует только кодеки - pcma, pcmu, g722, h264, h263-1998, t38. Остальные имеют статус =0 = выкл. Если хотите активизировать остальные кодеки, в редакторе nano измените приоритет с 0 на цифру приоритета (уровень приоритета не должен повторятся для сервиса audio/video/fax)
sudo nano /etc/ecss/ecss-media-server/config.xml
строчку -
<codec pcma="1" pcmu="2" ilbc="0" gsm="0" g722="3" g726="0" g729="0" speex="0" l16="0" g7221="0" opus="0" h264="1" h263-1998="2" t38="1" tel-event-pt="0"/>
привести к виду -
<codec pcma="1" pcmu="2" ilbc="6" gsm="4" g722="3" g726="11" g729="5" speex="7" l16="8" g7221="9" opus="10" h264="1" h263-1998="2" t38="1" tel-event-pt="0"/>
Недопустимо указывать у разных кодеков одинаковый приоритет, для примера g722="5" g729="5". В этом случае они будут работать некорректно/игнорироваться.
За исключением "0" - выключено.
Рассмотрим секцию аккаунтов (файл default.xml):
cat /etc/ecss/ecss-media-server/conf.d/default.xml
Проверить корректность данных.
<?xml version="1.0"?>
<config>
    <accounts>
        <dynamic msr_name="msr.ecss1" realm="sip:10.0.20.41:5000" dtmf_mode="rfc+inband+info" auth_name="user" auth_password="password">
            <via dynamic-ifaces="no">
                <iface name="net.20" ip="10.0.20.41"/>
            </via>
        </dynamic>
    </accounts>
</config>
В ней указаны текущие настройки, согласно которым происходит регистрация msr на core.
Основными параметрами здесь являются: msr_name и realm:
- msr_name — параметр, определяющий название msr. (рекомендуется задавать название msr. и к какому хосту он принадлежит, например msr.ecss1);
- realm — определяет адрес для регистрации на ядре. Точка входа по умолчанию: порт 5000, адрес: 127.0.0.1.
После изменения конфигурации файлов /etc/ecss/ecss-media-server/config.xml и /etc/ecss/ecss-media-server/conf.d/default.xml необходимо выполнить перезапуск сервиса ecss-media-server, чтобы изменения вступили в силу, следующей командой:
sudo systemctl restart ecss-media-server
Вы увидите сообщение:
Job for ecss-media-server.service failed because the control process exited with error code.
See "systemctl status ecss-media-server.service" and "journalctl -xeu ecss-media-server.service" for details.
Мы указали рабочие IP адреса для media сервиса, а они пока закреплены за старым ecss1. После переключения IP адресов сервис запустится автоматически.
ecss-web-conf
sudo apt install ecss-web-conf
Web-конфигуратор позволяет сделать управление системой более наглядным и комфортным. Установка web-конфигуратора не является обязательной, но рекомендуется.
Также при установке пакета ecss-web-conf автоматически устанавливается пакет ecss-subscriber-portal-ui. Приложение "Портал абонента" системы ECSS-10 позволяет абонентам системы самостоятельно управлять услугами, просматривать информацию по совершенным вызовам, активным конференциям, а также настраивать собственные IVR-скрипты для входящих вызовов. Описание работы веб-конфигуратора приведено в разделе "Портал абонента".
| Вопросы ecss-web-conf | Ответы для ecss1 | Пример |
|---|---|---|
| Хотите ли вы использовать стандартные настройки? | Yes (значение по умолчанию) |
|
Проверьте возможность подключения к веб-интерфейсу http://10.0.10.51, пользователь/пароль — admin/password. В настоящий момент не все функции будут доступны, но веб-интерфейс должен работать, а вход в систему — быть успешным.
Отключение SSW версии 3.17
Для отключения старого SSW версии 3.17 выполнить следующие команды:
Отключение сервисов
sudo systemctl mask --now ecss-ds ecss-mycelium ecss-mediator ecss-core ecss-pa-sip ecss-sorm
Копирование БД Postgres
Скопировать БД Postgres со старого ecss1, для этого выполнить команду:
sudo tar -Pcvf /tmp/postgres.tar /srv/ecss/ecss-postgres-bdr-ssw/volumes/
Скопировать postgres.tar на новый сервер, выполнив команду:
scp /tmp/postgres.tar <ваш_пользователь>@<IP_адрес_новый_ecss1>:/tmp/postgres.tar
Остановить docker БД Postgres командой:
sudo docker compose -f /srv/ecss/ecss-postgres-bdr-ssw/docker-compose.container.yml stop
Очистить подкаталог /srv/ecss/ecss-postgres-bdr-ssw/volumes:
sudo rm -R /srv/ecss/ecss-postgres-bdr-ssw/volumes/*
Распаковать БД Postgres на новом сервере ecss1.
sudo tar xvf /tmp/postgres.tar -C /
Запустить docker БД Postgres командой:
sudo docker compose -f /srv/ecss/ecss-postgres-bdr-ssw/docker-compose.container.yml start
Замена IP адресов на старом ecss1
Изменить IP адреса 10.0.10.41/10.0.20.41 на неиспользуемые на сети (для примера на 10.0.10.61/10.0.20.61):
sudo nano /etc/netplan/ecss.yaml
sudo netplan apply
Переключение нового SSW на рабочие IP адреса
После освобождения рабочих IP адресов со старого SSW можно подключить их к новому SSW. Выполнить команду:
sudo nano /etc/netplan/ecss.yaml
Изменить IP адреса 10.0.10.51/10.0.20.51 на используемые на сети для SSW (в примере 10.0.10.41/10.0.20.41):
sudo netplan apply
Обновить IP адрес в файле /etc/hosts:
sudo nano /etc/hosts
Обновить IP адрес в файле /etc/dnsmasq.d/ecss-broker:
sudo dpkg-reconfigure ecss-dns-env
/system/licence/manager/set --hosts [https://10.0.10.41:4321]
sudo systemctl restart ecss-ds ecss-mycelium ecss-mediator ecss-core ecss-pa-sip ecss-media-server
После выполнения обновления проверьте работу всех сервисов SSW.